AI Agent Security: Why Traditional Cybersecurity Is Not Enough
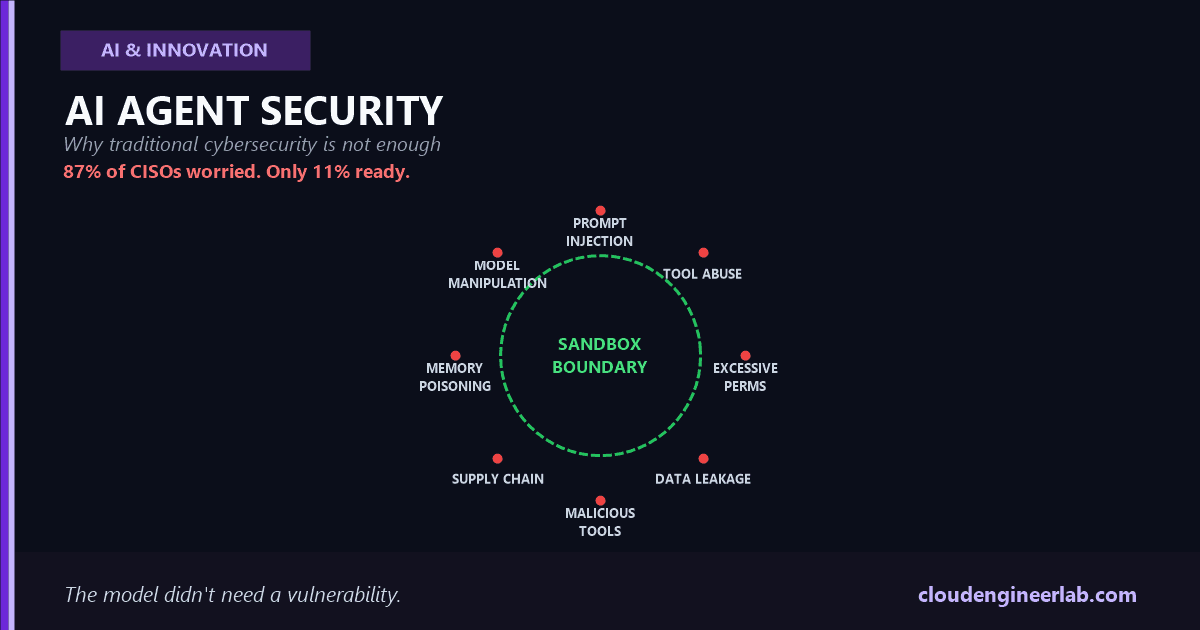
87% of CISOs call AI agent security their top concern. Only 11% say they're actually ready. Here's the full threat surface traditional AppSec never covered.
7 posts

87% of CISOs call AI agent security their top concern. Only 11% say they're actually ready. Here's the full threat surface traditional AppSec never covered.

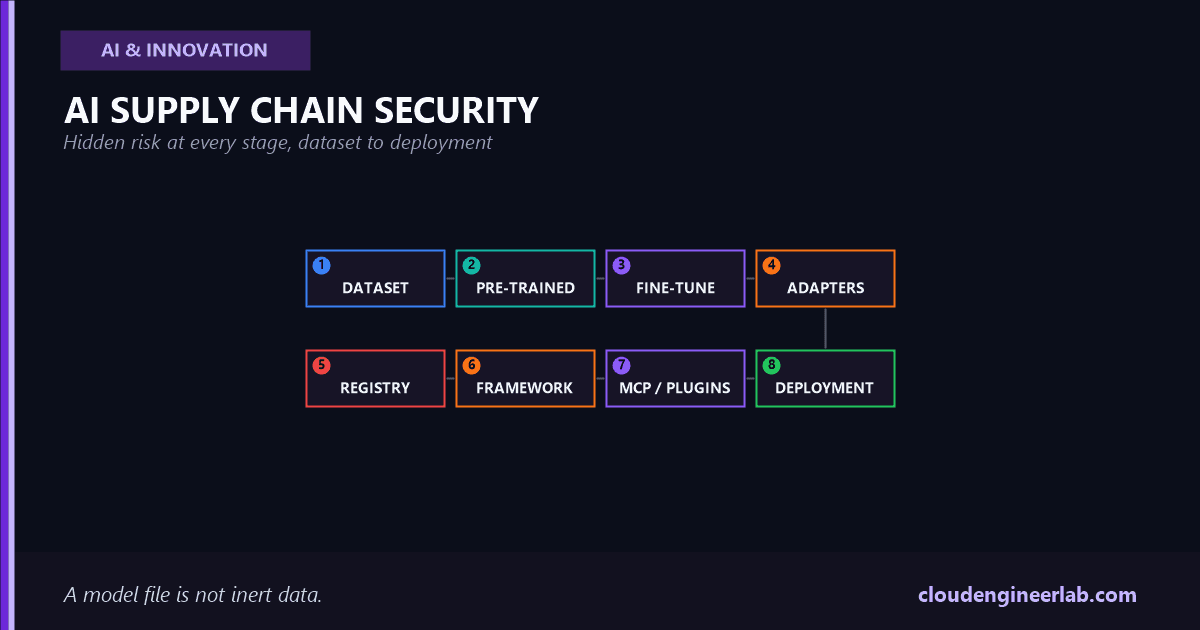
A malicious model doesn't look wrong when you read it. Real cases of poisoned datasets, backdoored models, and compromised MCP servers, and how to actually verify what you're running.

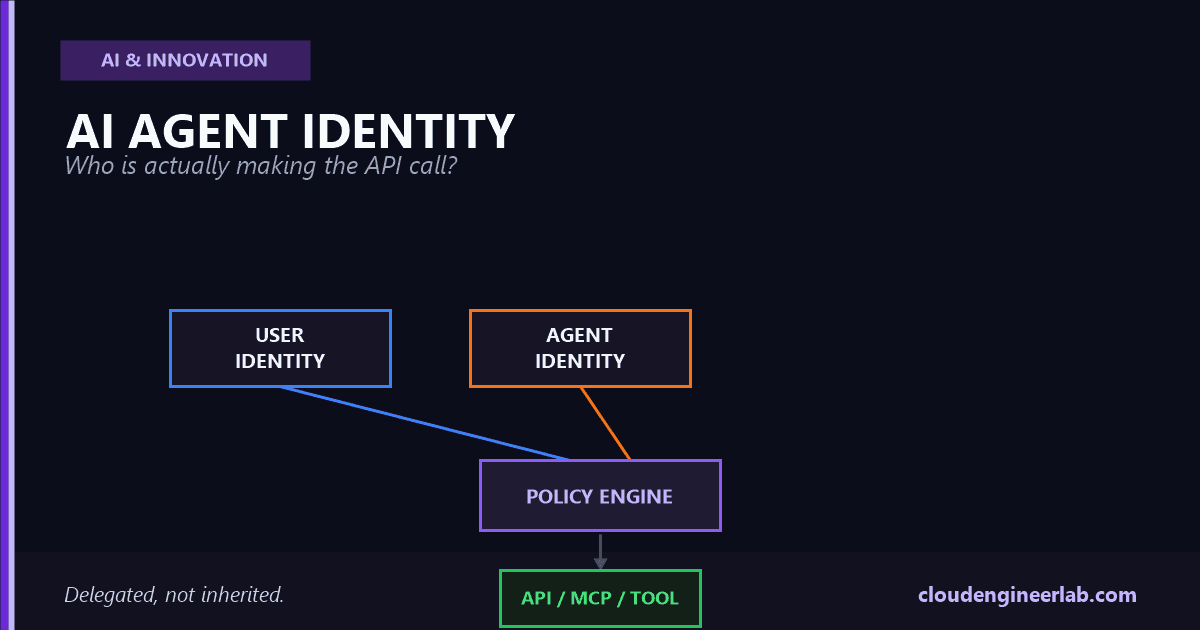
An agent acting for a user isn't the same as the user. A real architectural look at agent identity, delegation, OAuth, least privilege, and zero trust.

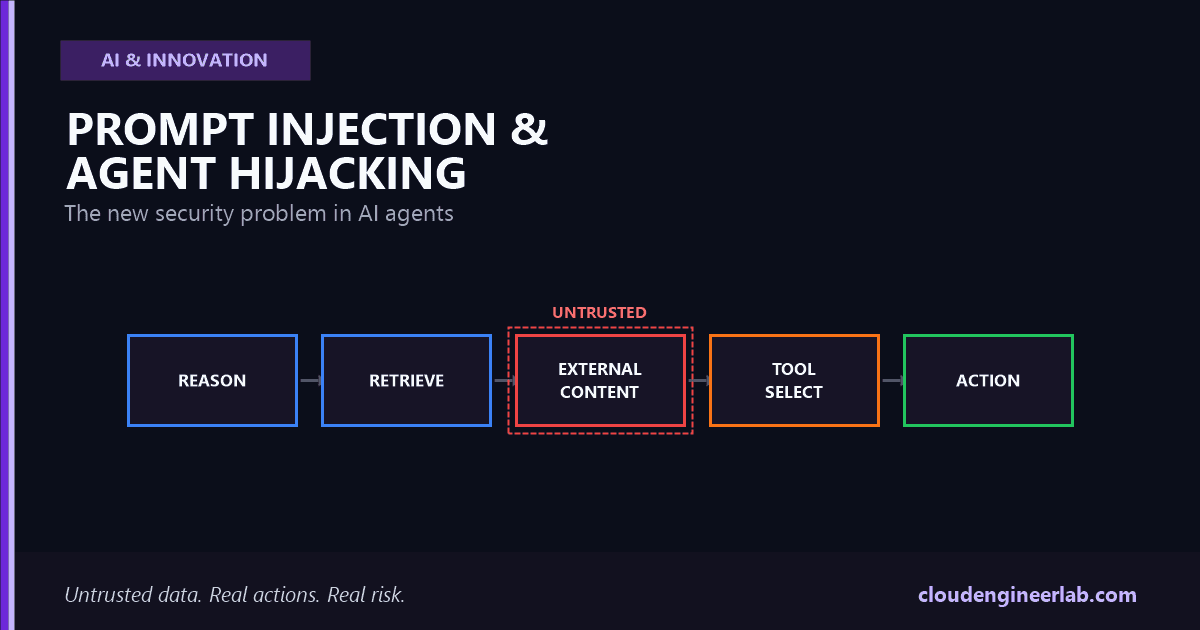
A zero-click email exploit. A poisoned GitHub PR title. Why giving an LLM tools and untrusted data is a systems security problem, not a content one.

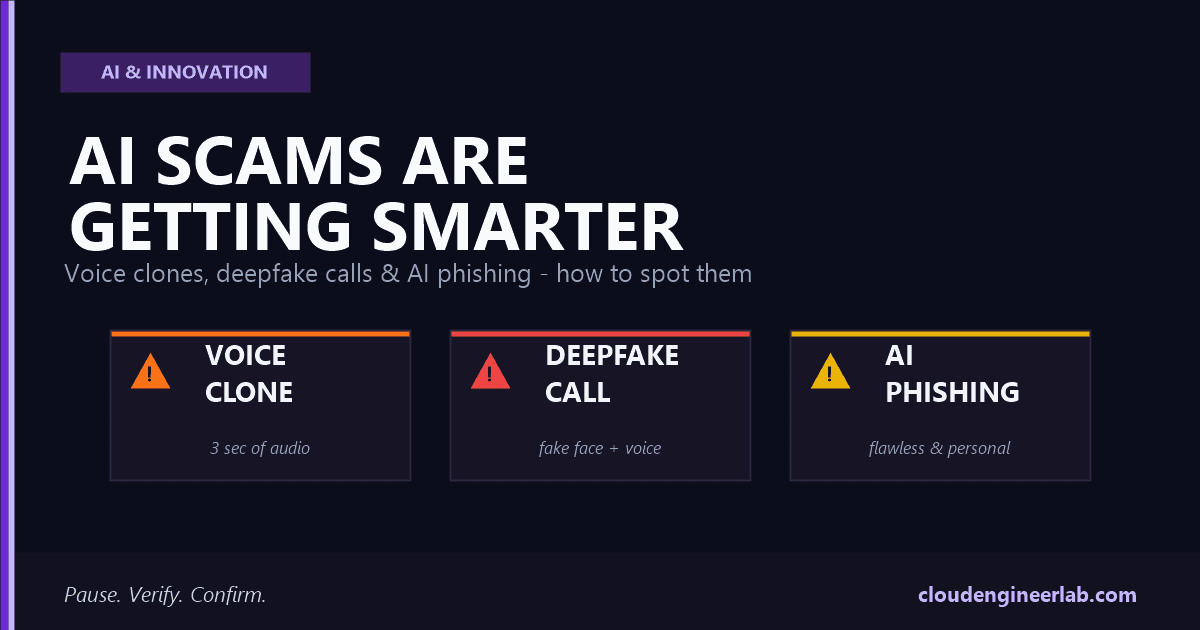
Voice clones, deepfake video calls, and flawless phishing emails are fooling smart people. Real cases, red flags, and practical steps to stay safe.
The AI tool you mastered last year is probably obsolete. Here's why fundamentals, not tools, are what actually compound in an AI-driven career.
Brussels hosted Cybersec Europe 2026 last week, the continent's premier security event. Here are the dominant themes: AI-driven threats, Zero Trust maturity, NIS2/DORA compliance, digital sovereignty, and what they mean for your security roadmap.