Conditional Access Policies Every Microsoft 365 Administrator Should Understand
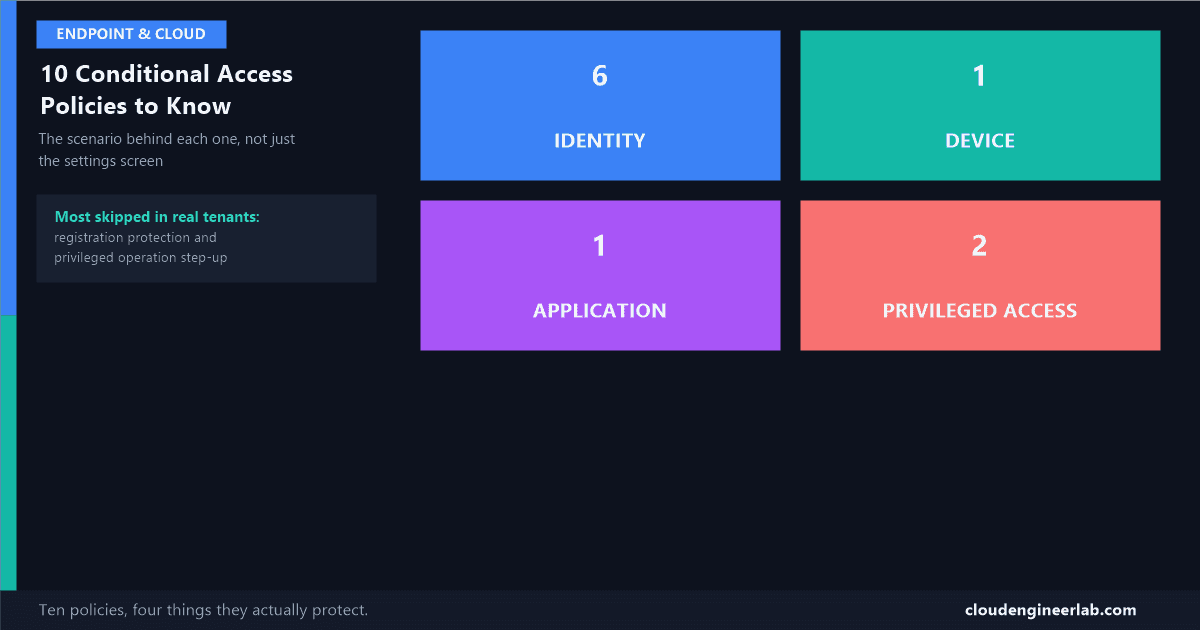
Ten real Conditional Access patterns explained through the actual scenario each one exists to stop, not just the settings screen you'd click through.
8 posts

Ten real Conditional Access patterns explained through the actual scenario each one exists to stop, not just the settings screen you'd click through.

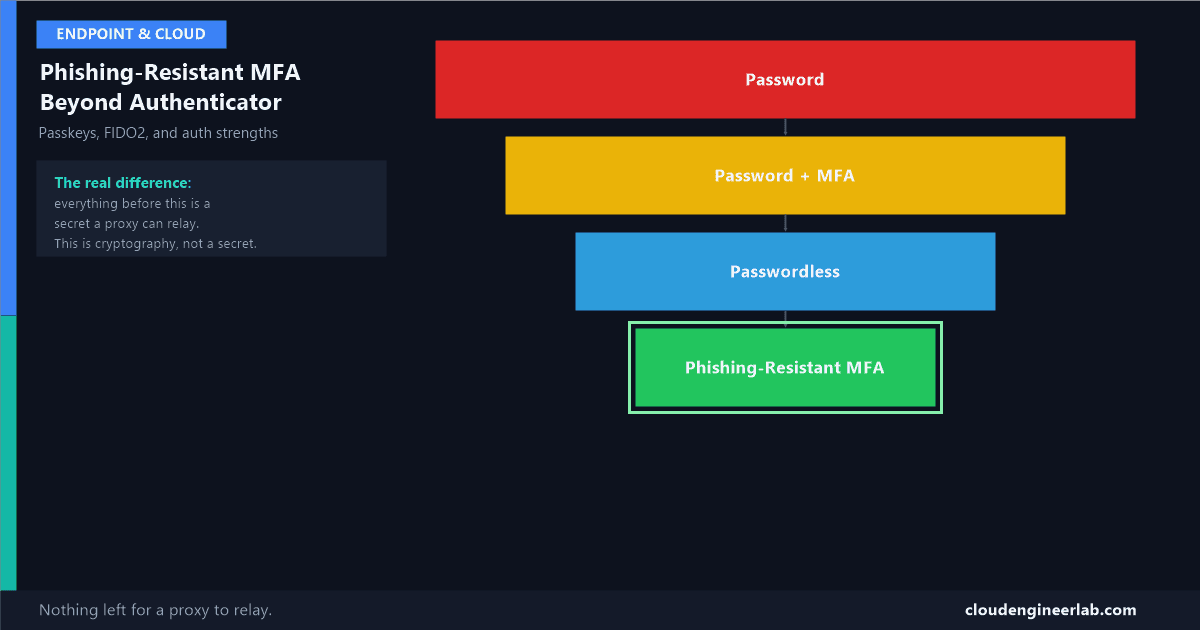
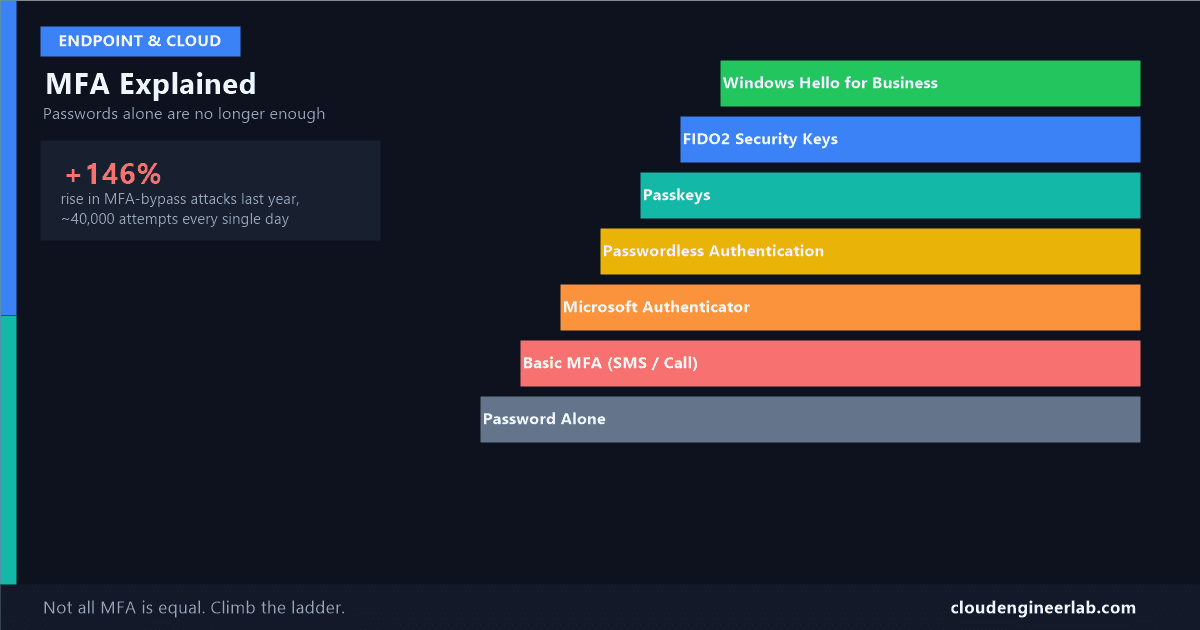
Push notifications and app codes still get phished in real time. Here's how passkeys and FIDO2 close that gap cryptographically, and how to actually enforce it.

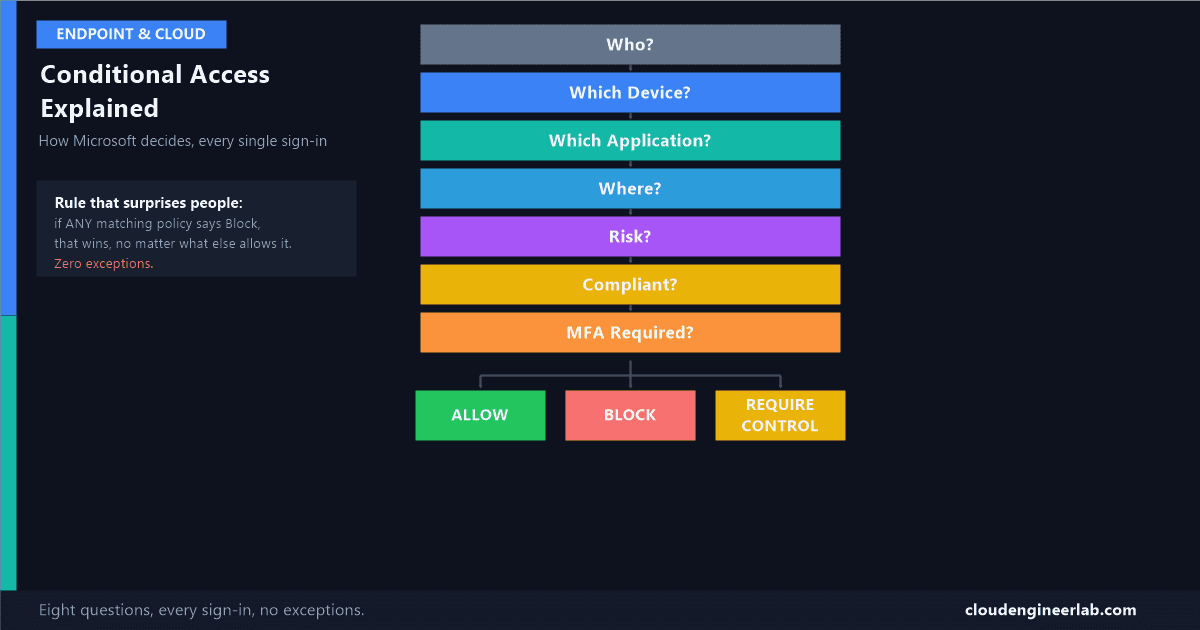
Every sign-in gets asked the same eight questions before Microsoft decides anything. Here's the actual decision engine, walked through with real examples.

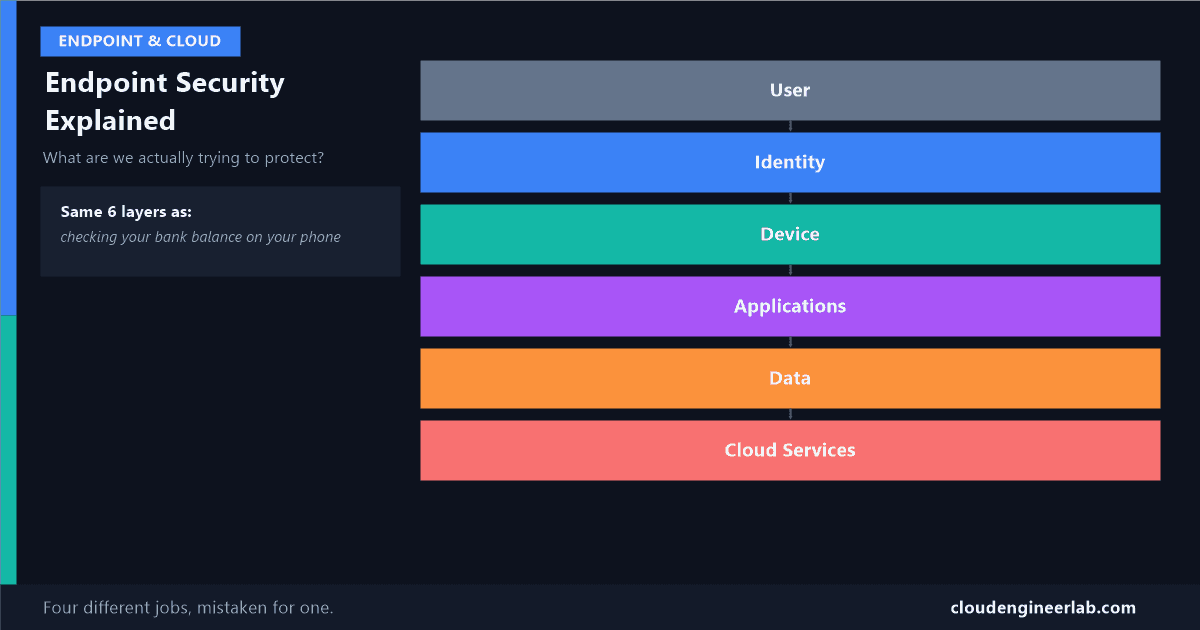
"Endpoint security" sounds like one thing. It's actually four different jobs stacked on top of each other, and mixing them up is how real breaches happen.

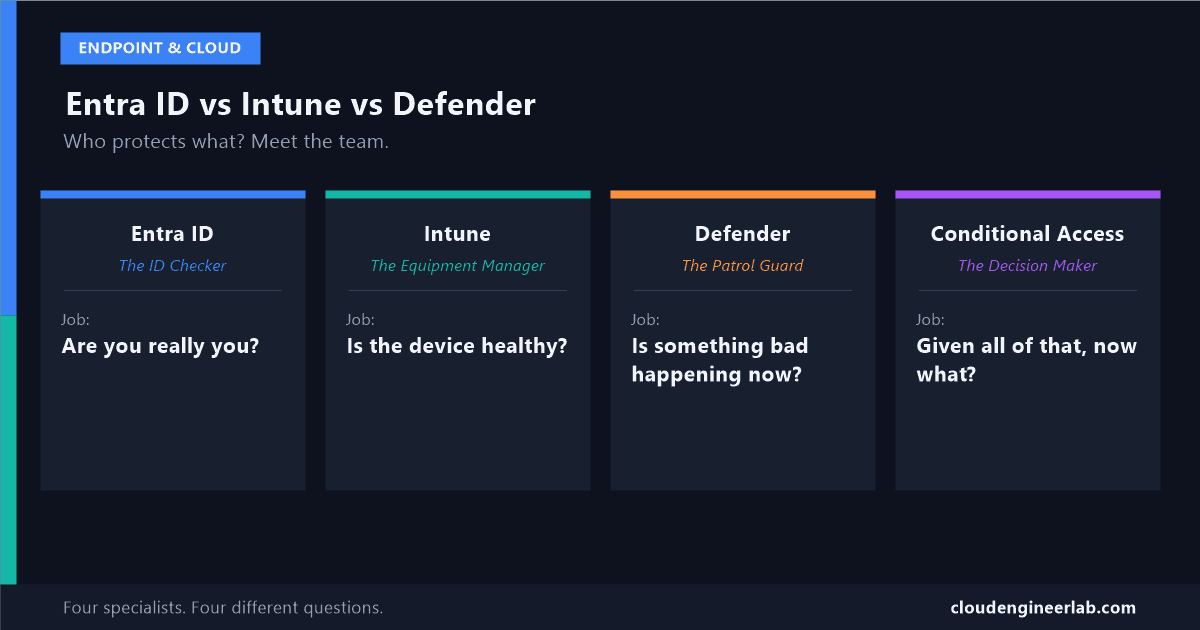
Three products, three different jobs, one common mistake: assuming any one of them alone is 'the security team.' Meet each one and find out who actually handles what.

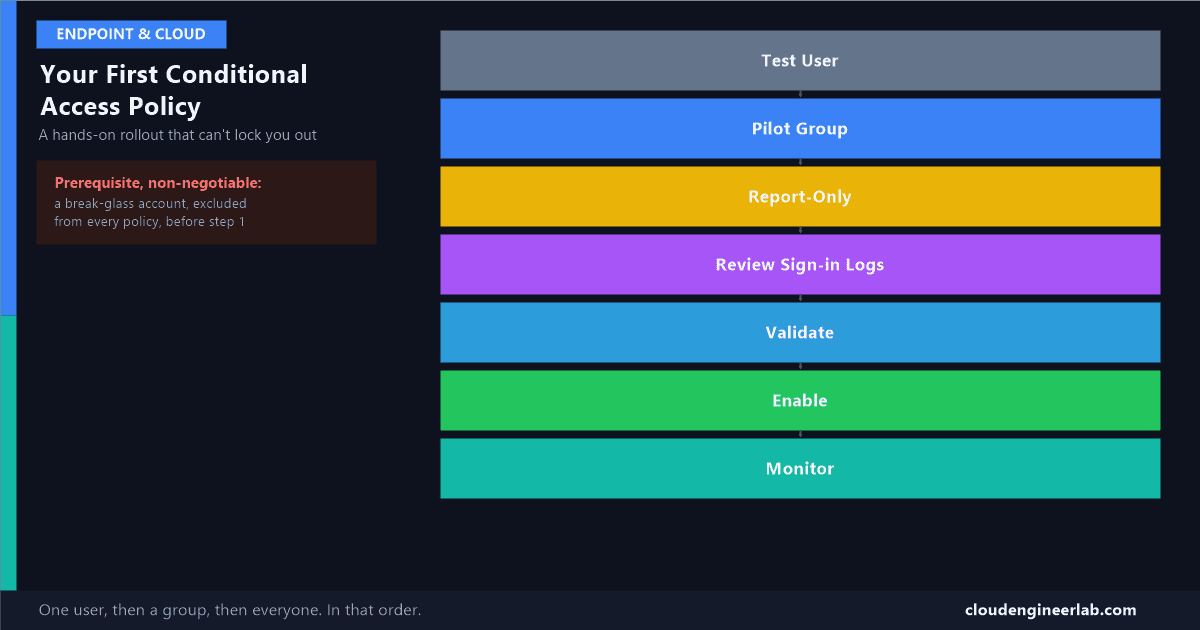
A real, step-by-step rollout, from one test user to full monitoring, built so your first policy can't accidentally lock out the whole organisation.


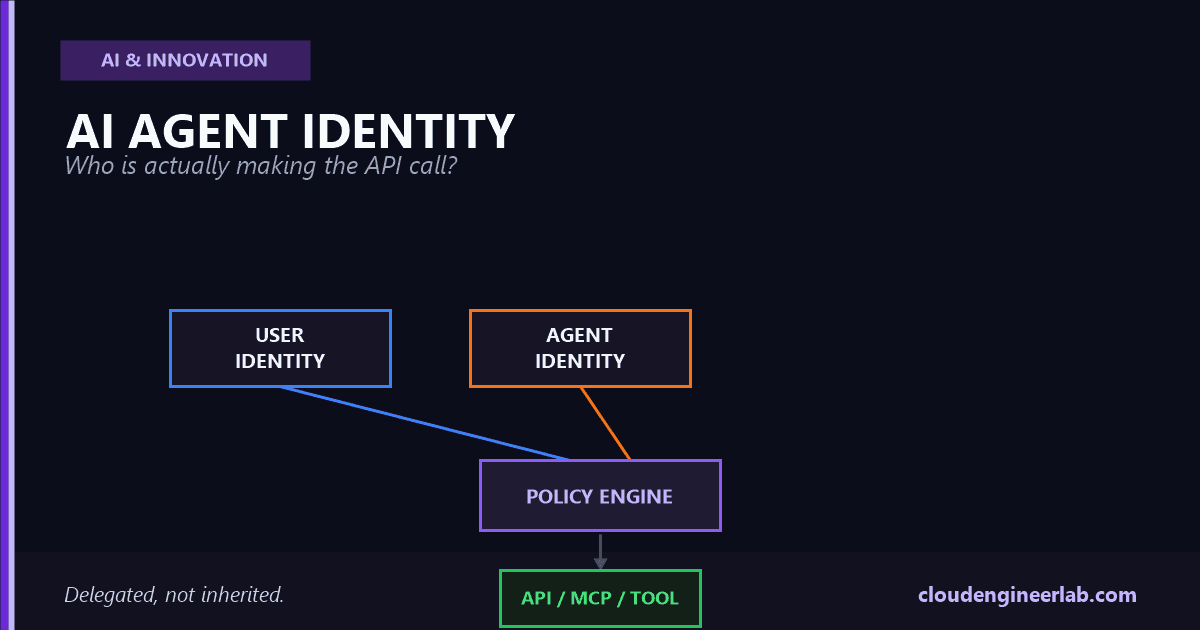
An agent acting for a user isn't the same as the user. A real architectural look at agent identity, delegation, OAuth, least privilege, and zero trust.