How to Build a Secure Windows Endpoint From Scratch: A Complete Practical Lab
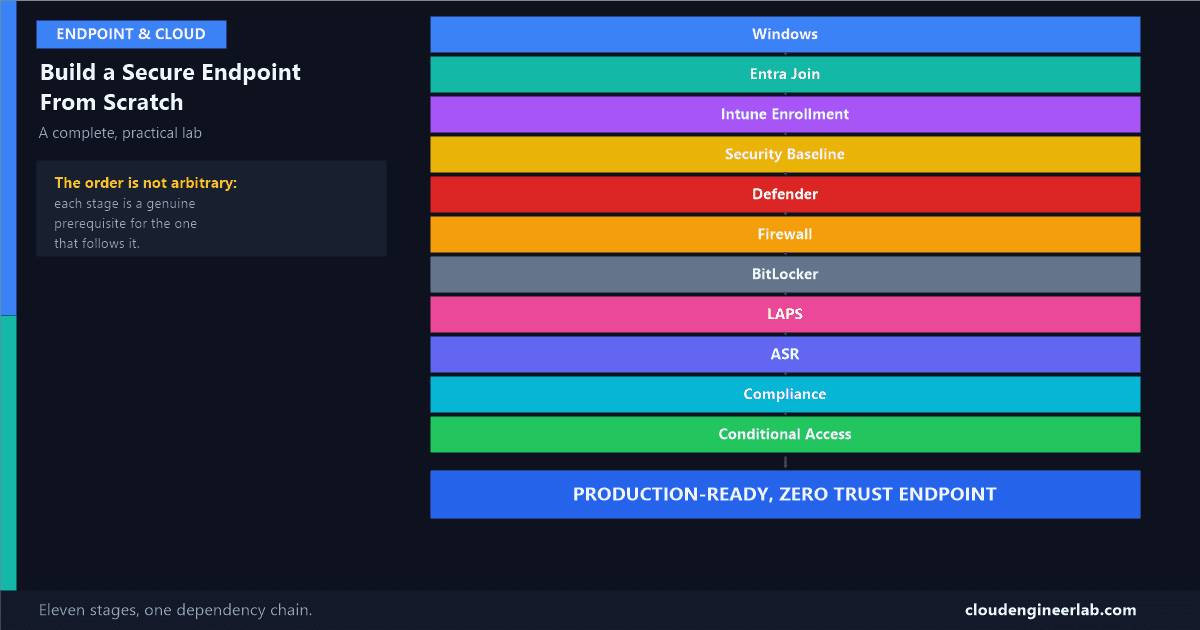
Eleven stages, in the exact order they actually depend on each other, from a blank Windows machine to a fully hardened, Conditional-Access-protected endpoint.
16 posts

Eleven stages, in the exact order they actually depend on each other, from a blank Windows machine to a fully hardened, Conditional-Access-protected endpoint.

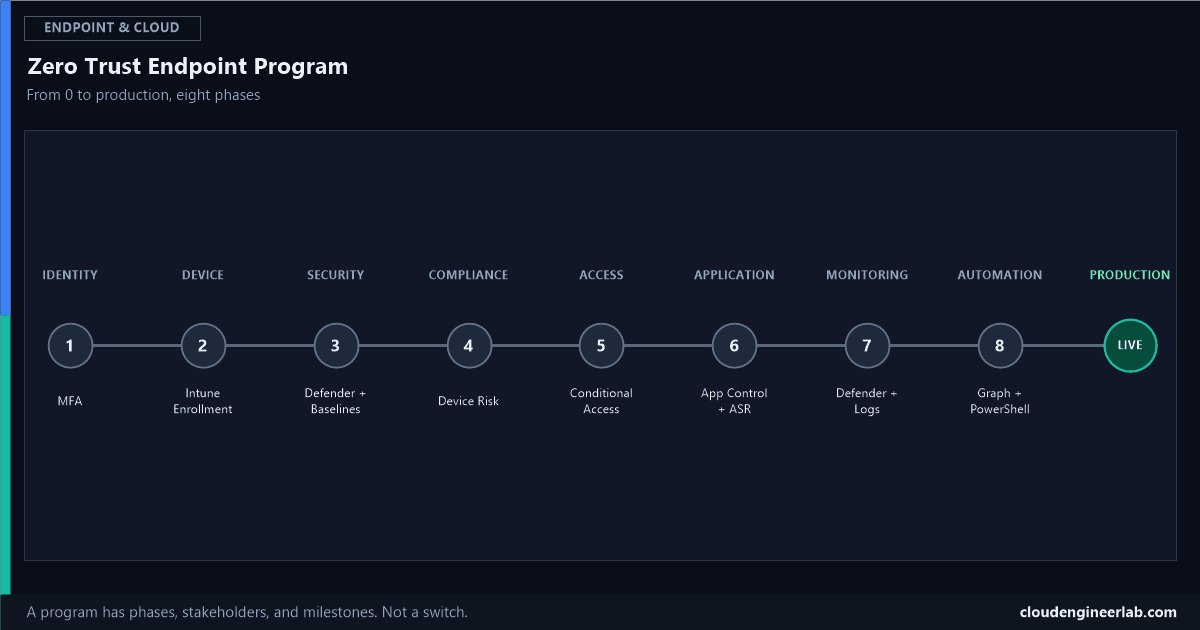
Deploying every control at once produces chaos, not Zero Trust. Eight phases, in the order a real enterprise program actually runs them, with the pitfall at each one.

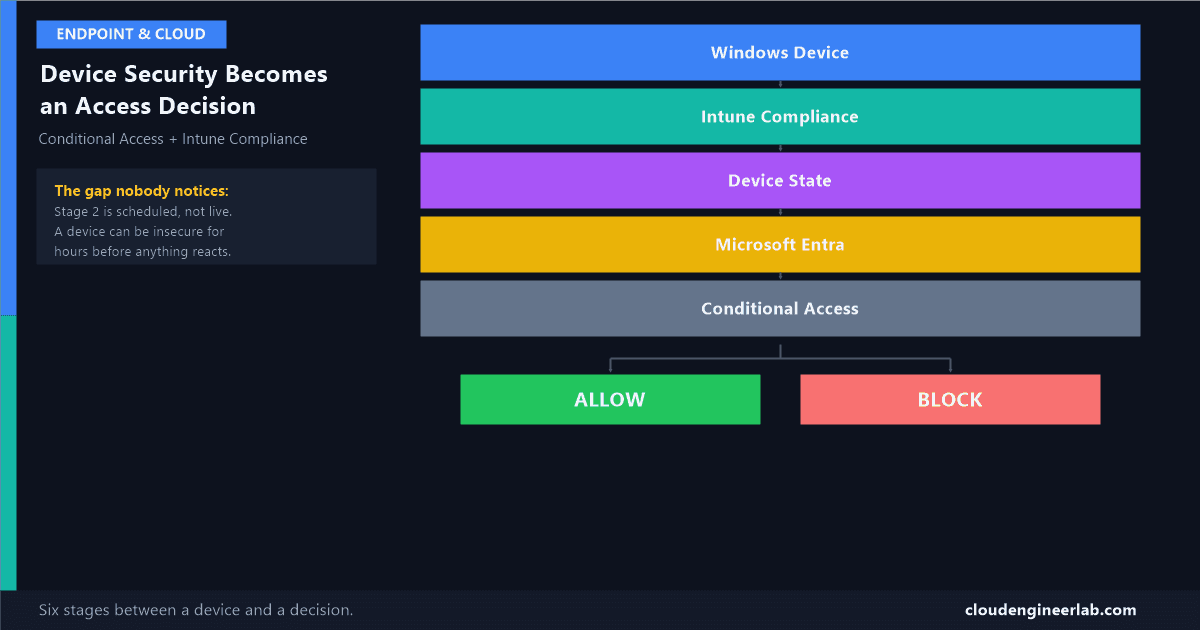
A device isn't just compliant or not. Follow the actual six-stage path a laptop's security state travels before it becomes an Allow or Block.

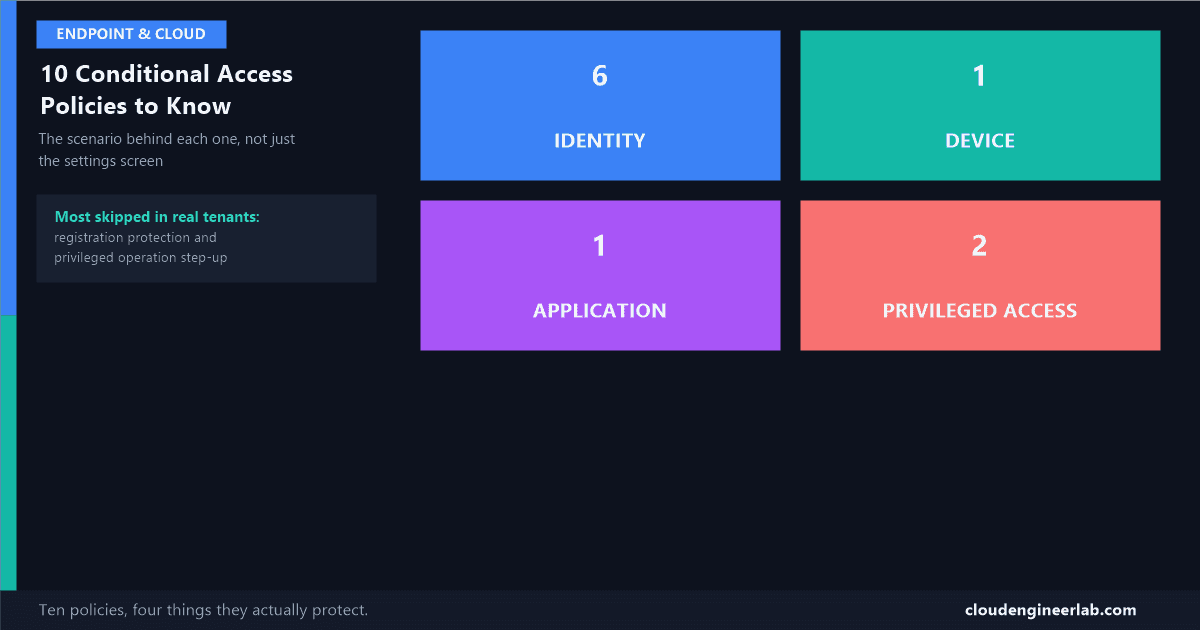
Ten real Conditional Access patterns explained through the actual scenario each one exists to stop, not just the settings screen you'd click through.

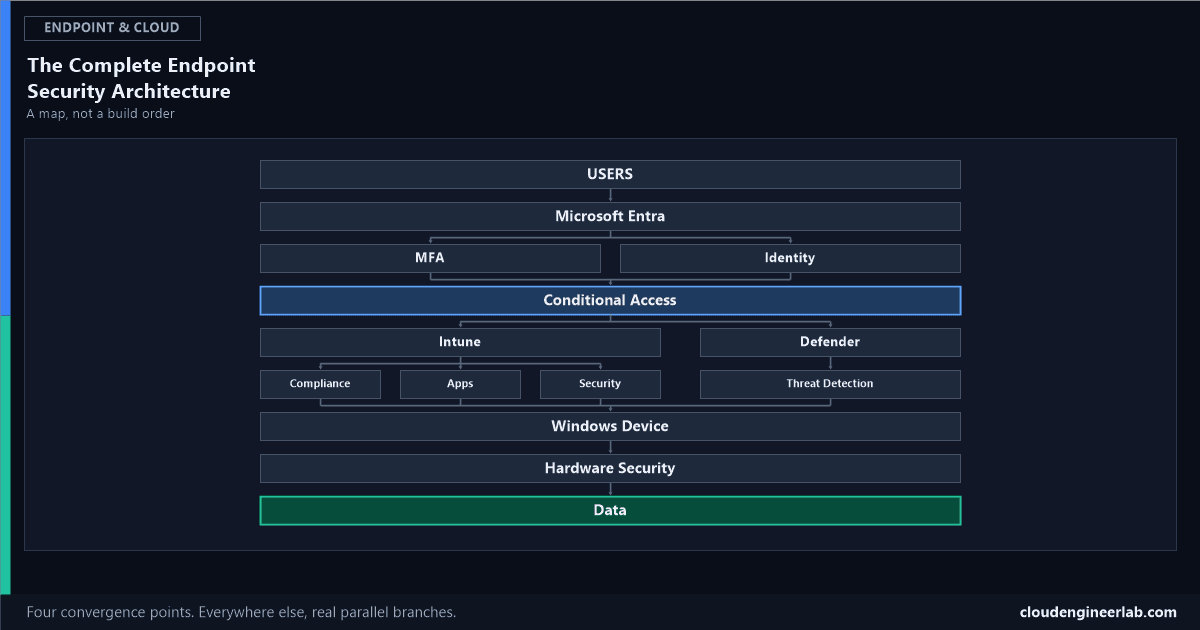
Every product covered on this site, placed on one map, showing exactly what branches in parallel and what has to converge before the next layer can trust it.

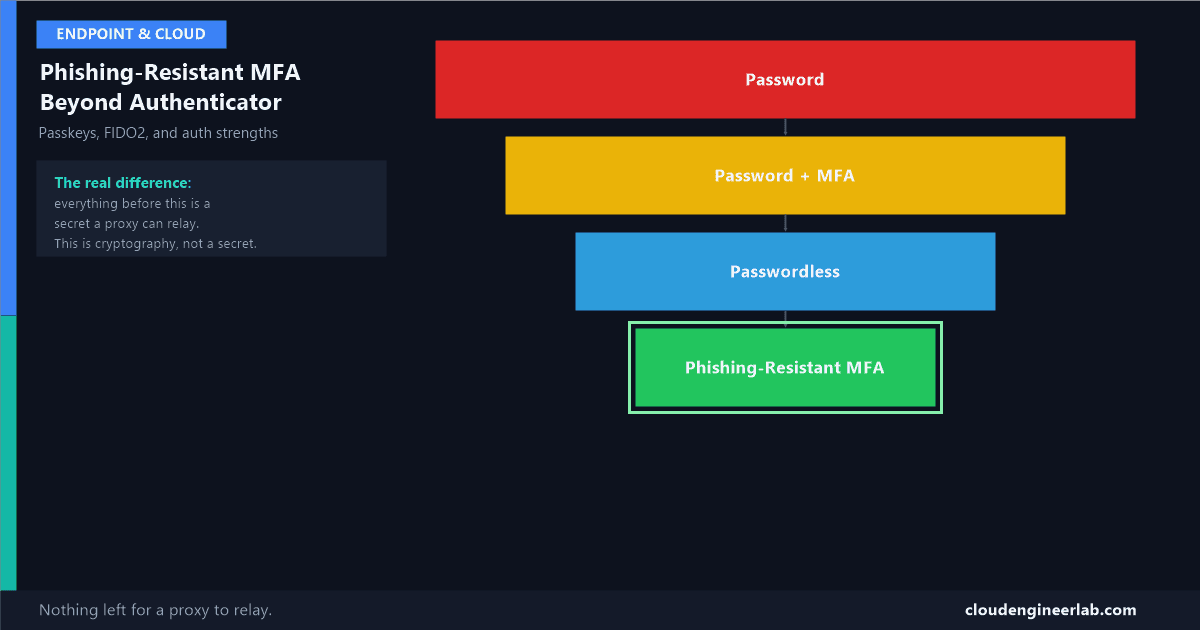
Push notifications and app codes still get phished in real time. Here's how passkeys and FIDO2 close that gap cryptographically, and how to actually enforce it.

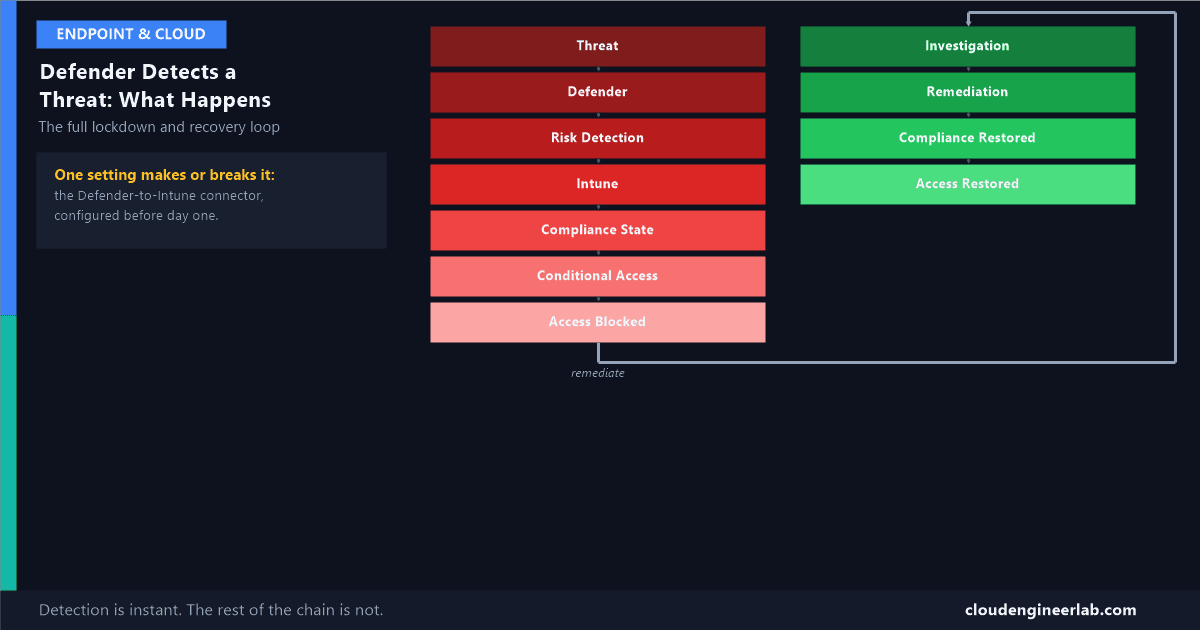
Eleven stages from a live threat to a locked-out device, and eleven more back to normal. The full closed loop, with the real lag at every handoff.

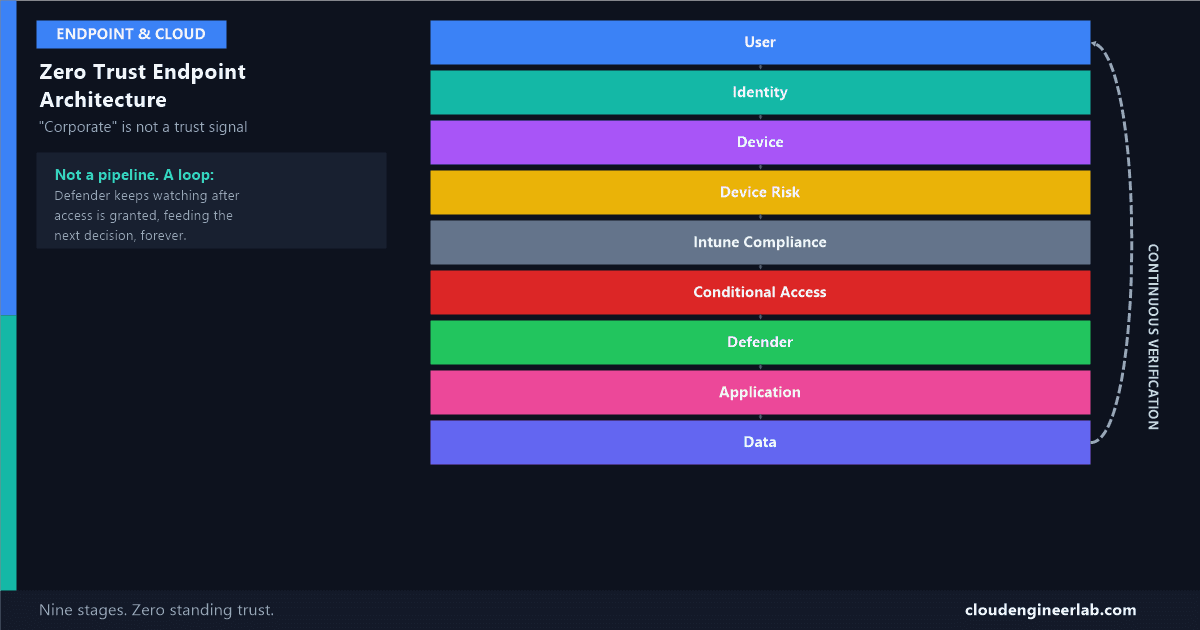
A domain-joined, company-issued laptop is not automatically trustworthy. Nine layers, one continuous loop, and why 'corporate' was never the actual trust signal.

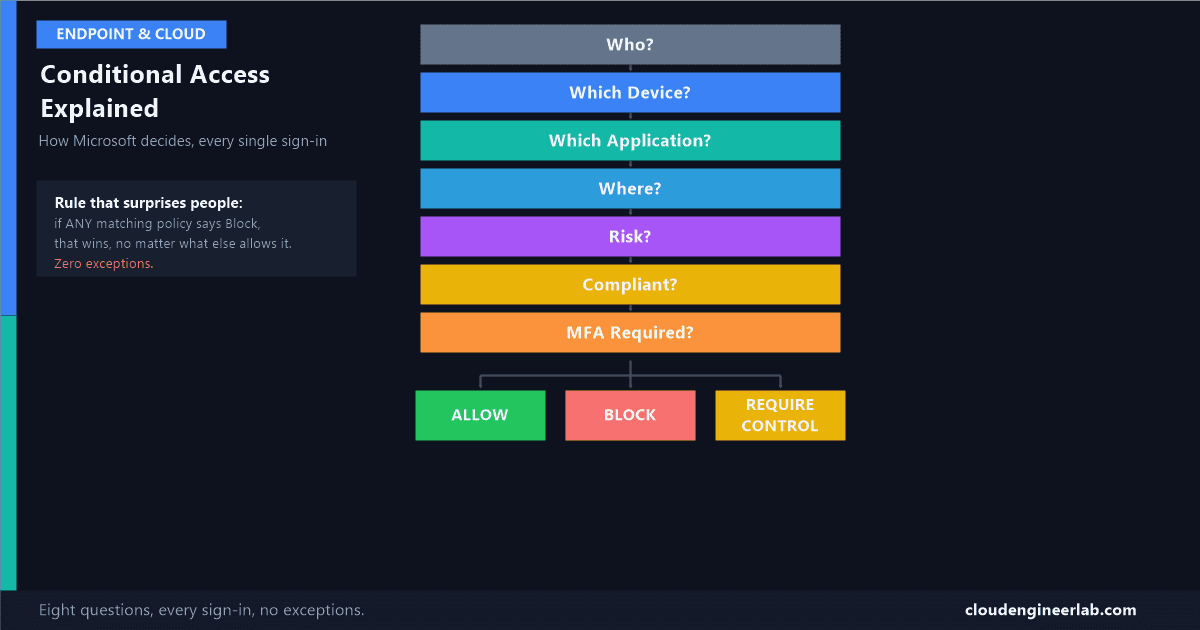
Every sign-in gets asked the same eight questions before Microsoft decides anything. Here's the actual decision engine, walked through with real examples.

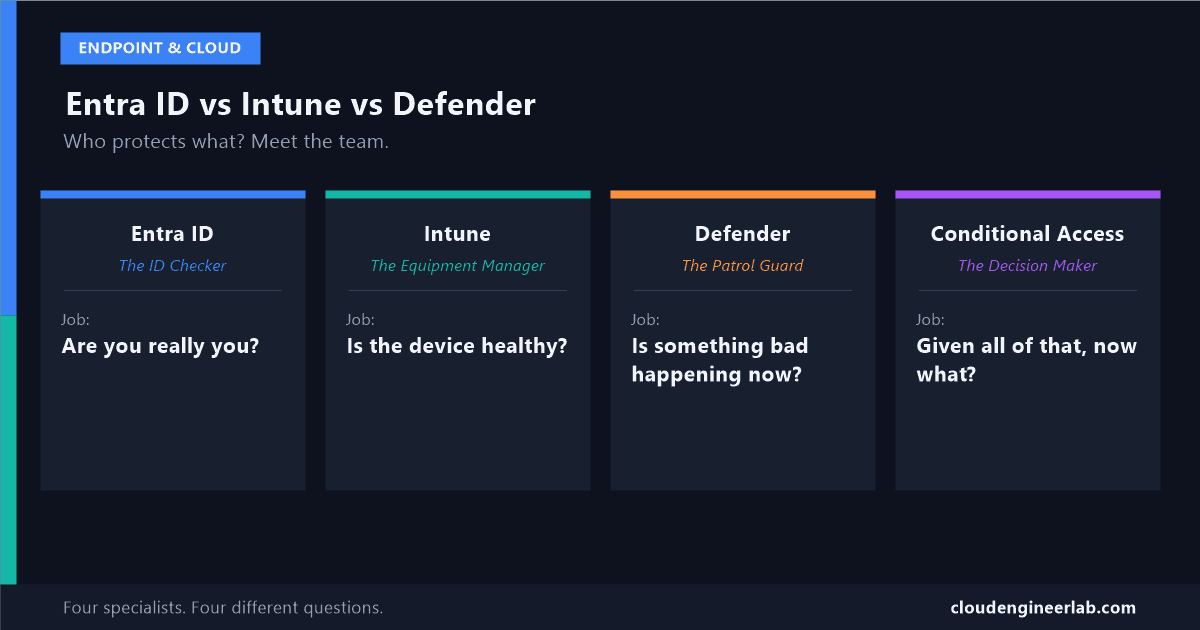
Three products, three different jobs, one common mistake: assuming any one of them alone is 'the security team.' Meet each one and find out who actually handles what.

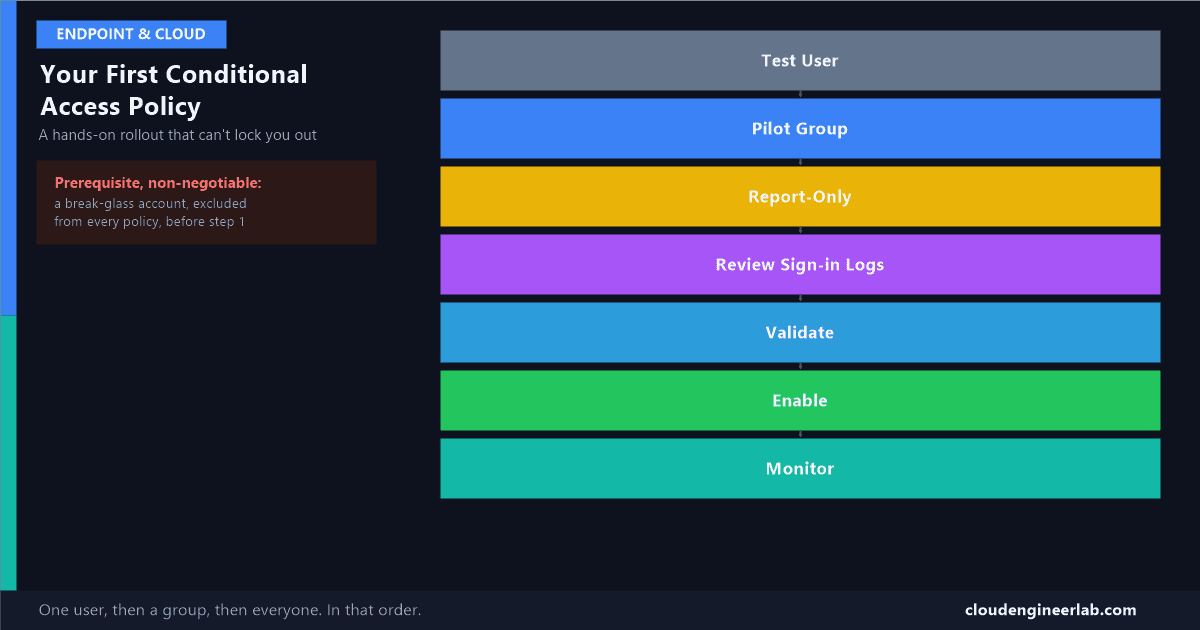
A real, step-by-step rollout, from one test user to full monitoring, built so your first policy can't accidentally lock out the whole organisation.

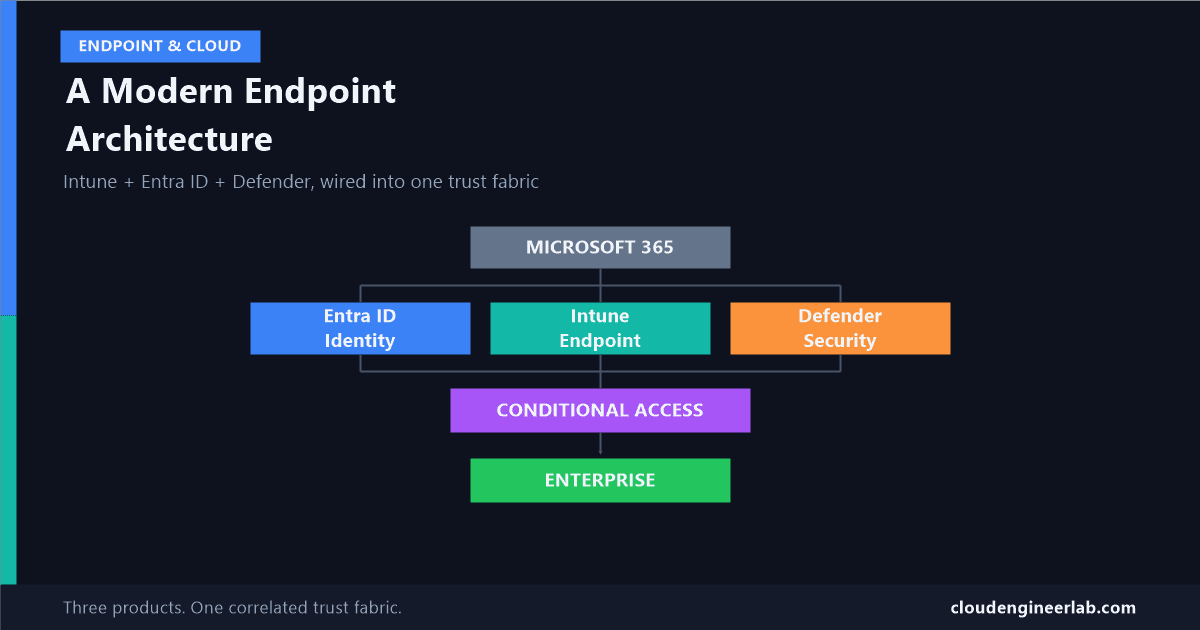
These three products aren't separate tools bolted together, they're one correlated trust fabric. Most tenants deploy all three and never actually wire them into it.

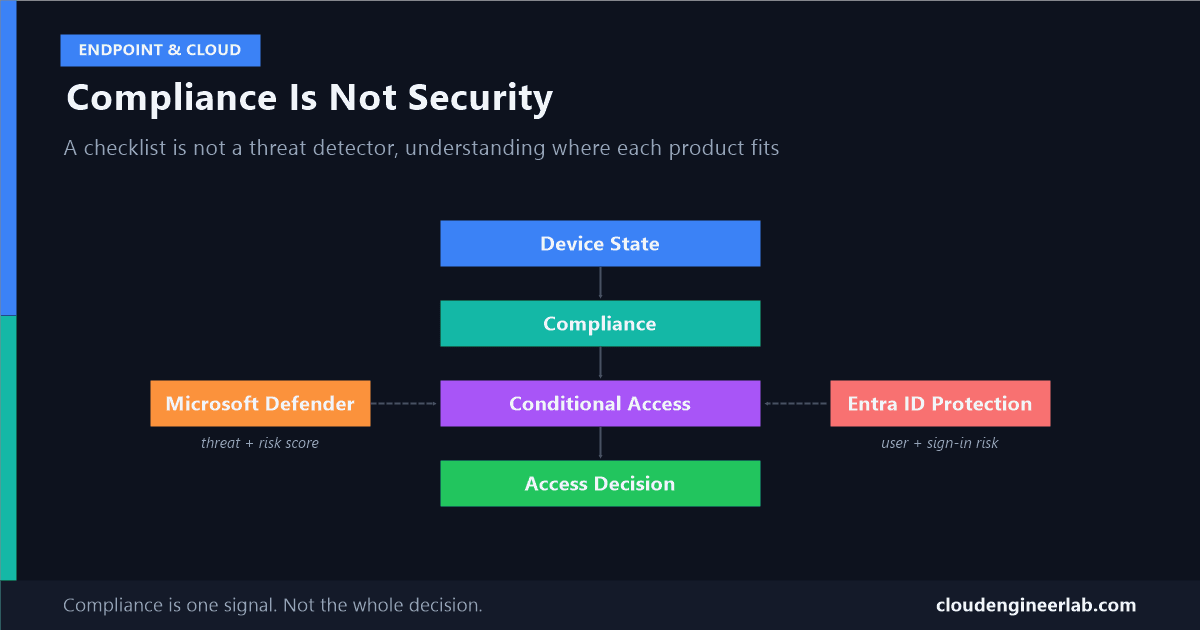
A fully patched, encrypted, PIN-locked device can still be actively compromised. Here's why compliance is a checklist, not a security guarantee, and what actually is.

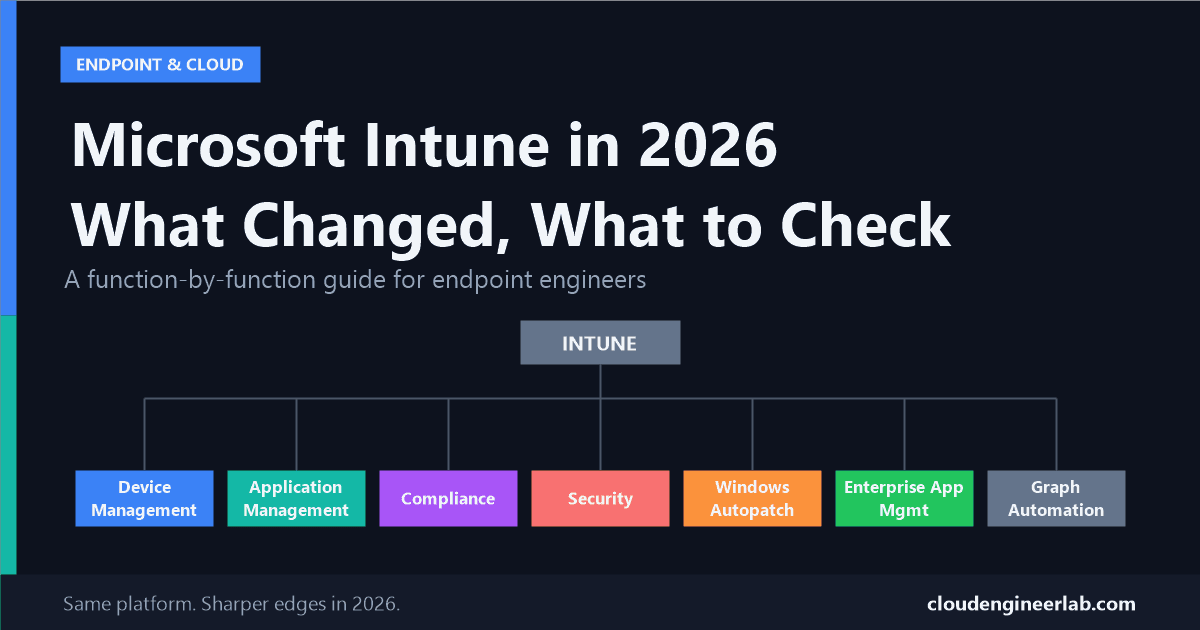
A function-by-function breakdown of what actually changed in Intune this year, and the specific checks every endpoint engineer should run in their own tenant.

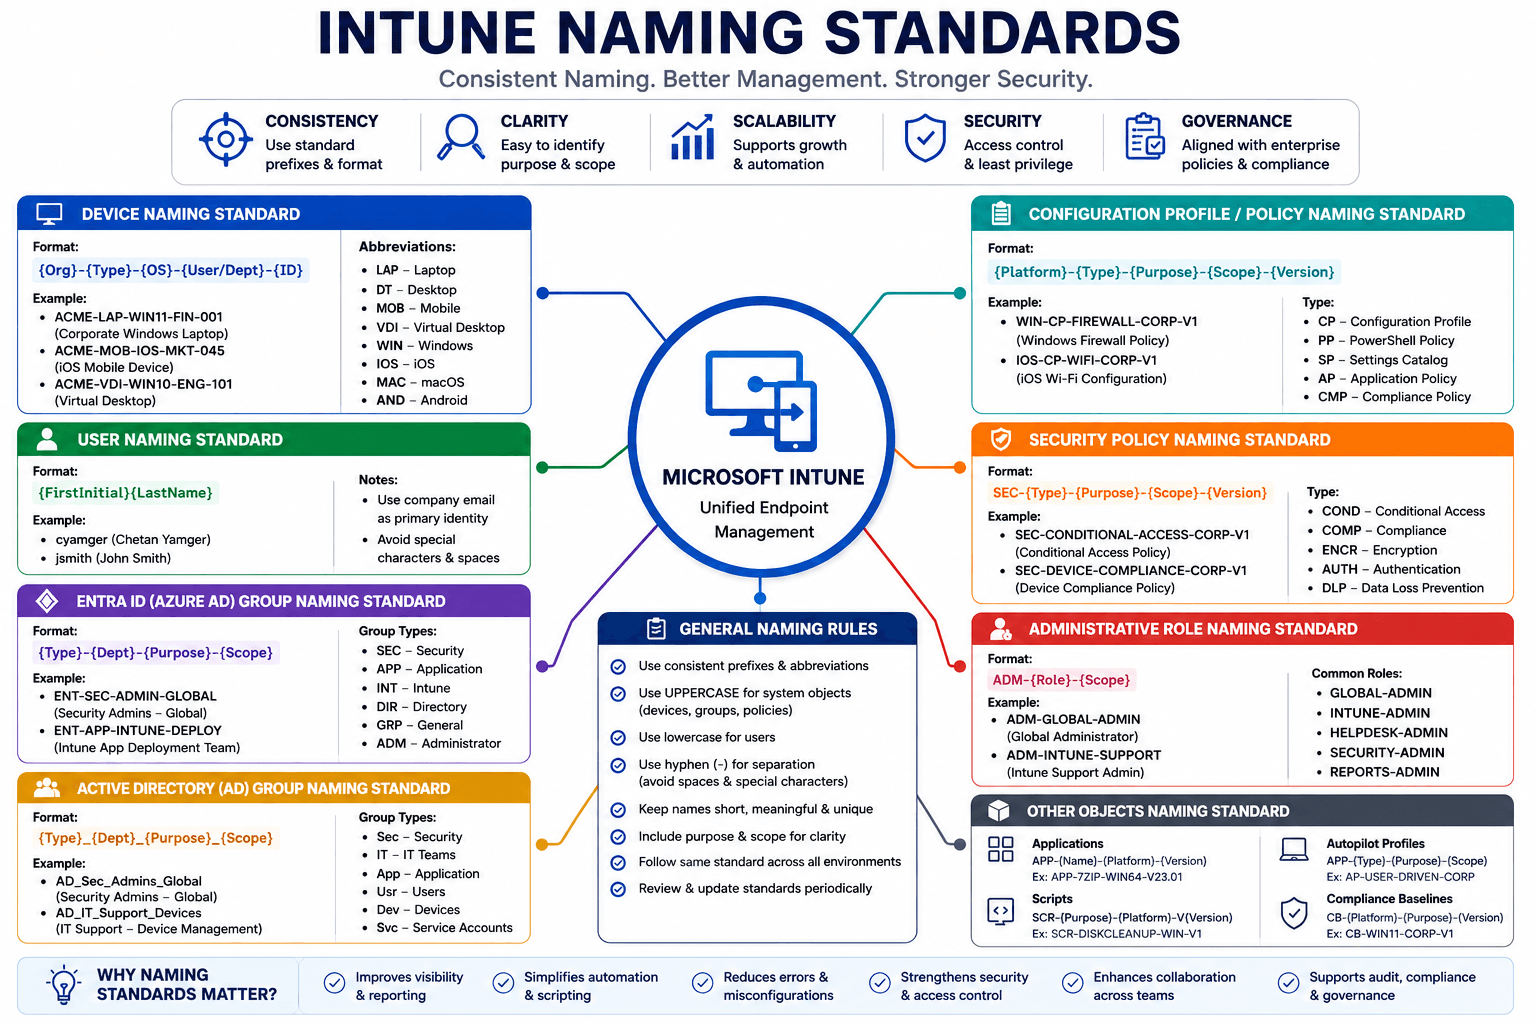
A complete naming convention guide for enterprise IT environments, covering Intune, Entra ID, Active Directory, Conditional Access, Configuration Profiles, Security Policies, Service Accounts, and every object type an admin touches daily.

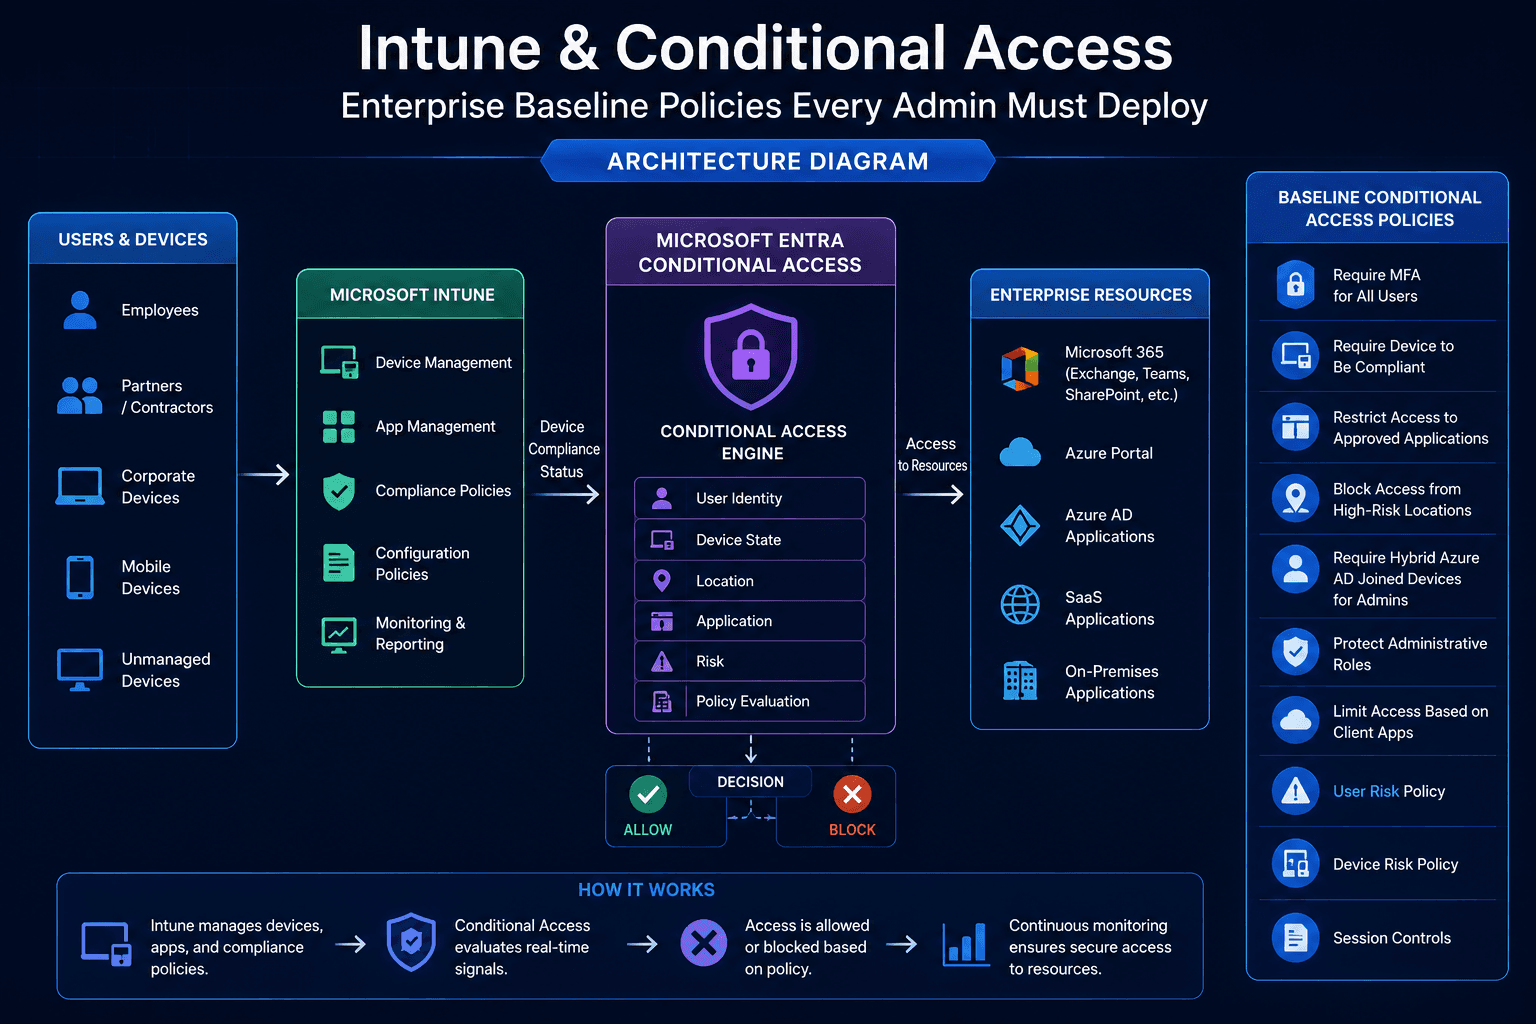
A complete enterprise guide to Conditional Access baseline policies: what to deploy, what to test before you flip the switch, what can go wrong, and why getting this wrong can lock out your entire organisation.