How to Build a Secure Windows Endpoint From Scratch: A Complete Practical Lab
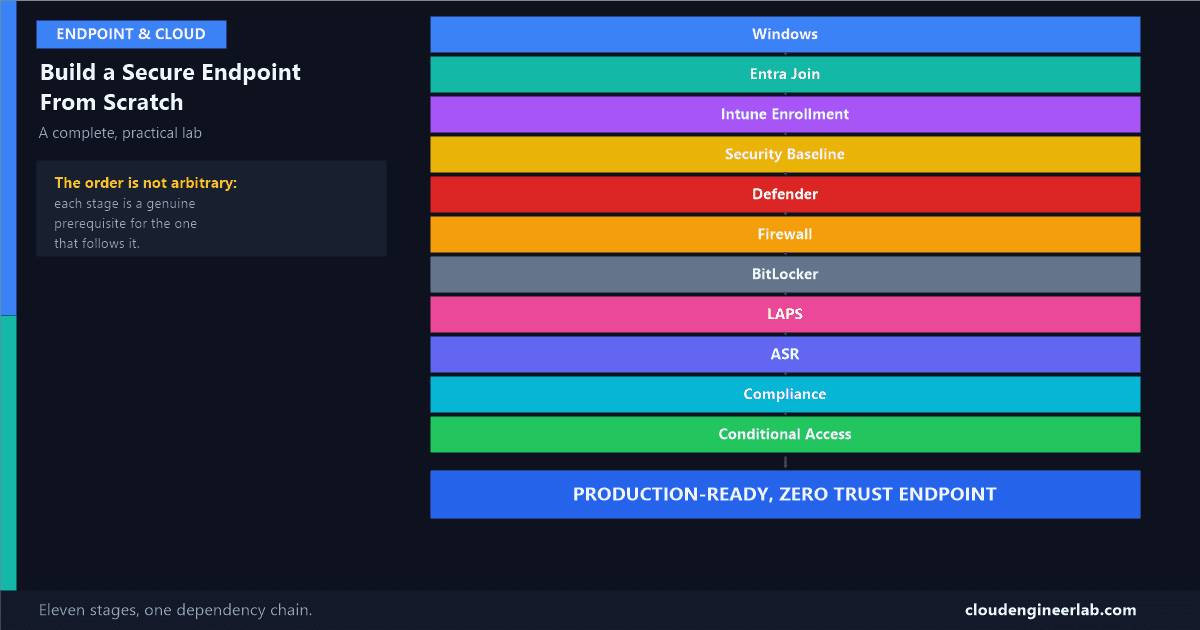
Eleven stages, in the exact order they actually depend on each other, from a blank Windows machine to a fully hardened, Conditional-Access-protected endpoint.
11 posts

Eleven stages, in the exact order they actually depend on each other, from a blank Windows machine to a fully hardened, Conditional-Access-protected endpoint.

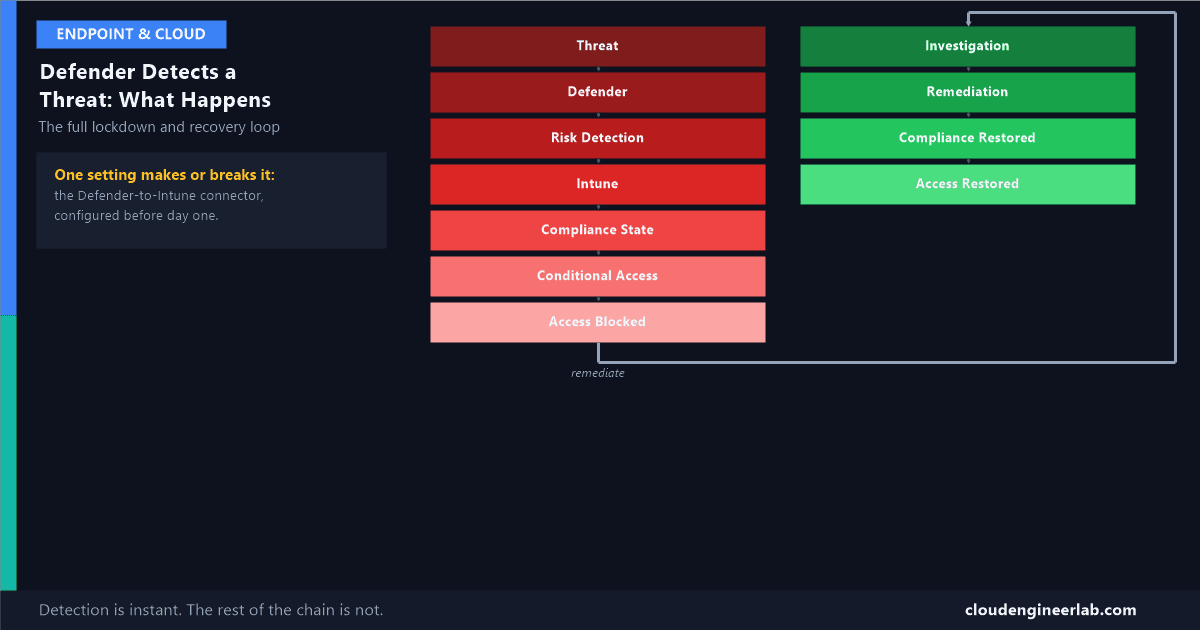
Eleven stages from a live threat to a locked-out device, and eleven more back to normal. The full closed loop, with the real lag at every handoff.

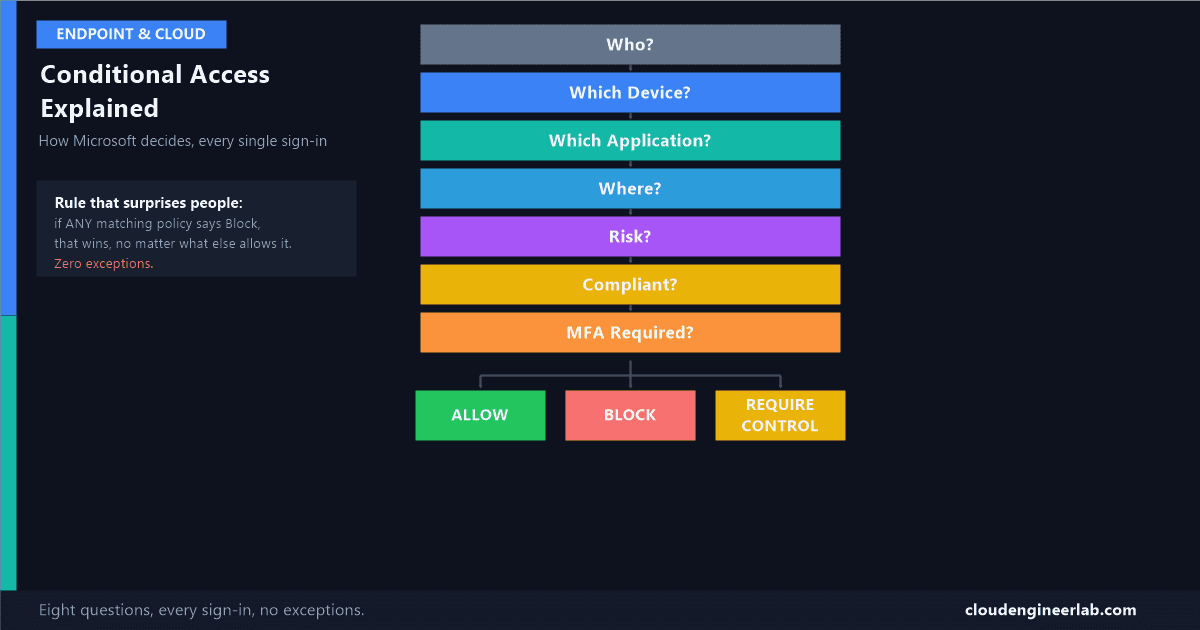
Every sign-in gets asked the same eight questions before Microsoft decides anything. Here's the actual decision engine, walked through with real examples.

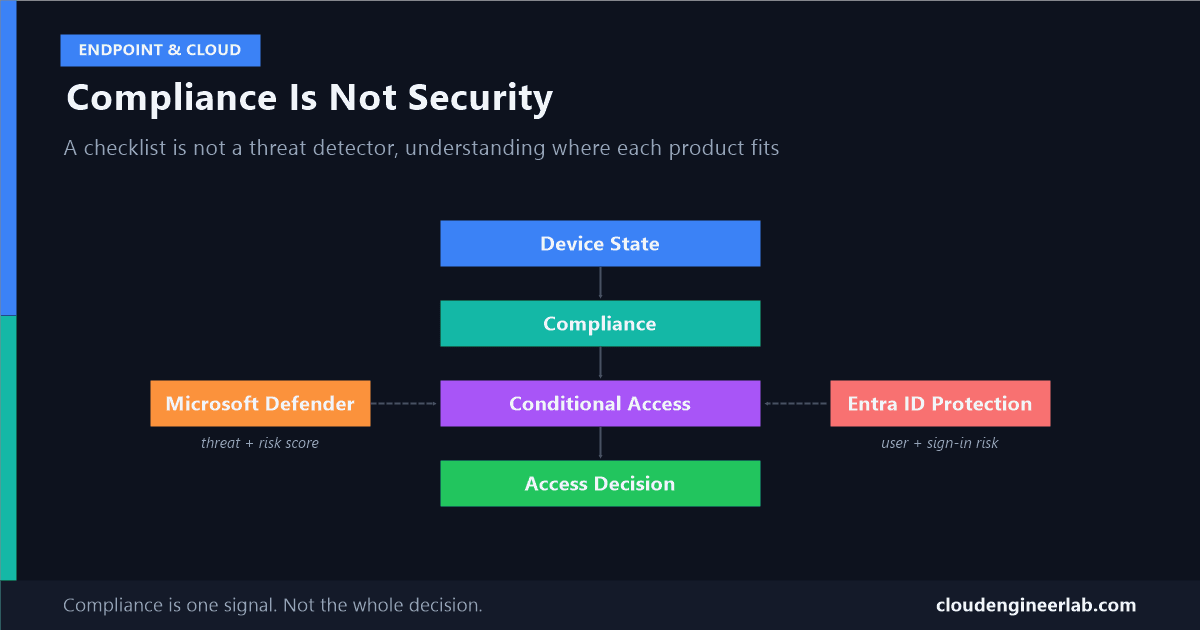
A fully patched, encrypted, PIN-locked device can still be actively compromised. Here's why compliance is a checklist, not a security guarantee, and what actually is.

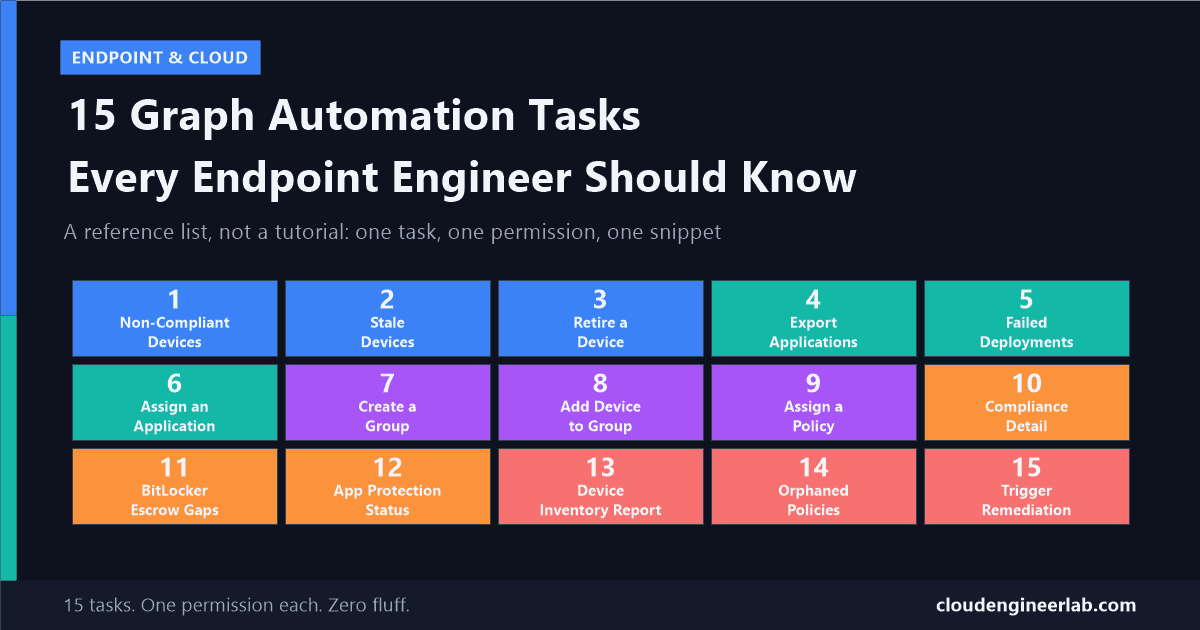
A reference list of 15 real, working Graph tasks, from finding stale devices to triggering remediation scripts, each with the exact permission and code.

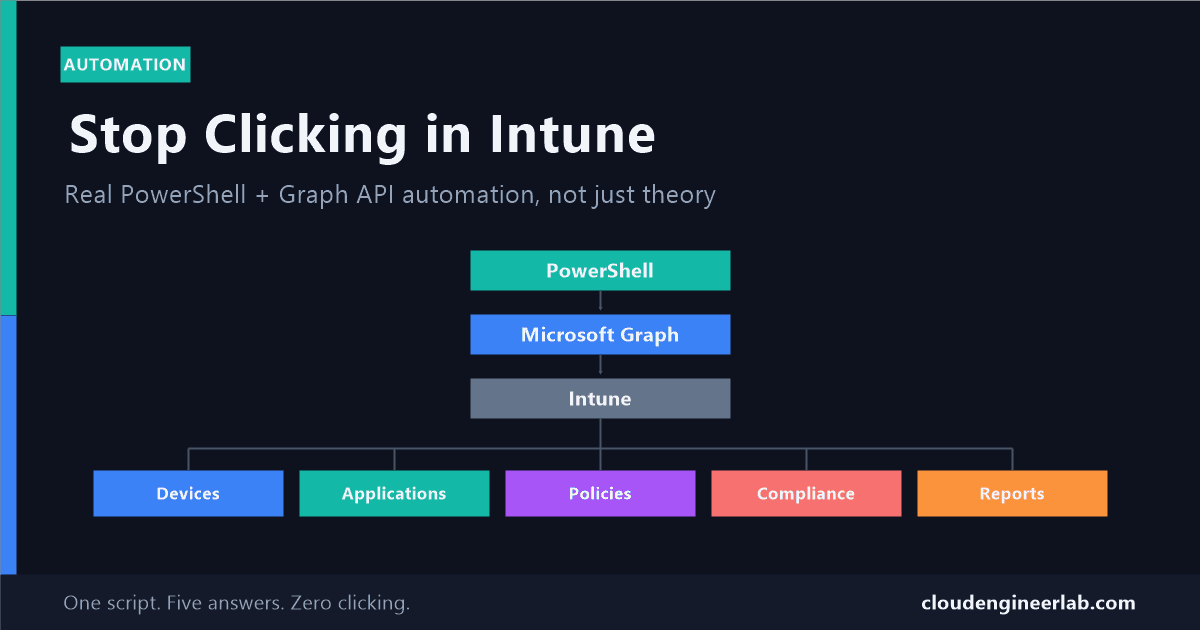
Real, working PowerShell and Graph examples across devices, apps, policies, compliance, and reports, not just theory about what the API can do.

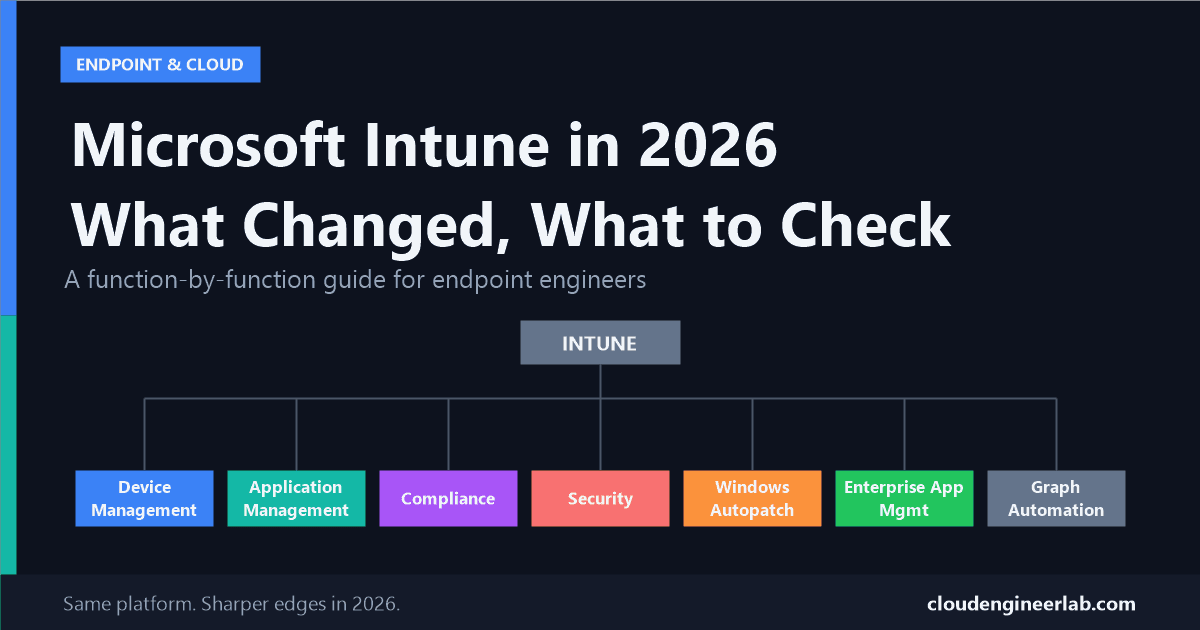
A function-by-function breakdown of what actually changed in Intune this year, and the specific checks every endpoint engineer should run in their own tenant.

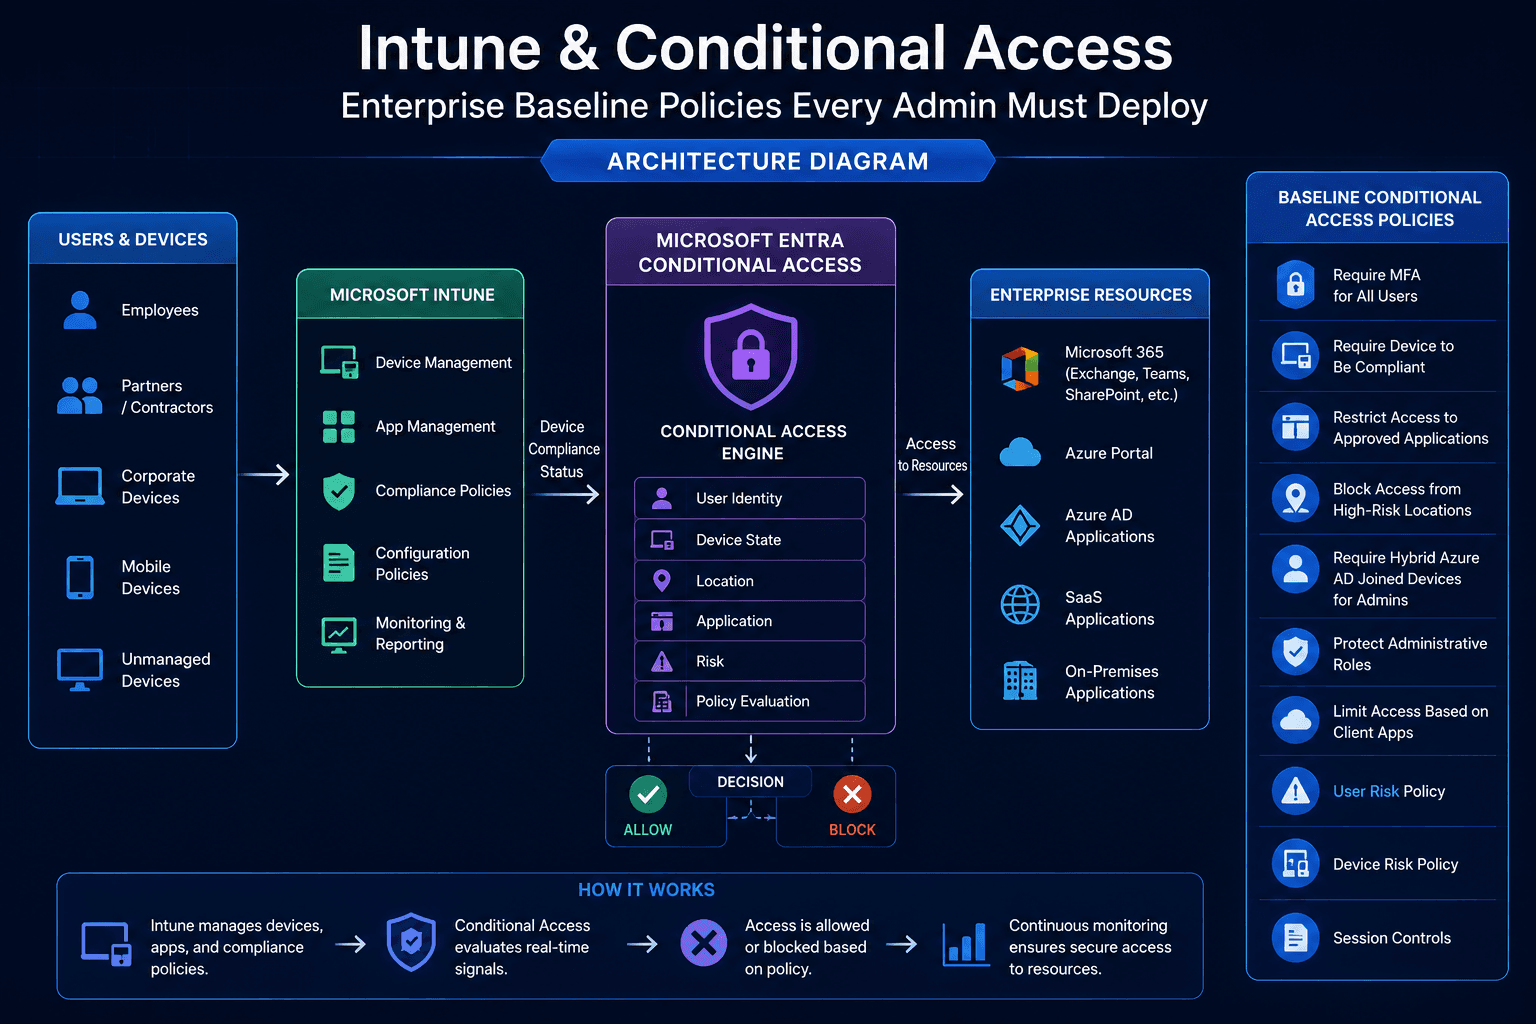
A complete enterprise guide to Conditional Access baseline policies: what to deploy, what to test before you flip the switch, what can go wrong, and why getting this wrong can lock out your entire organisation.

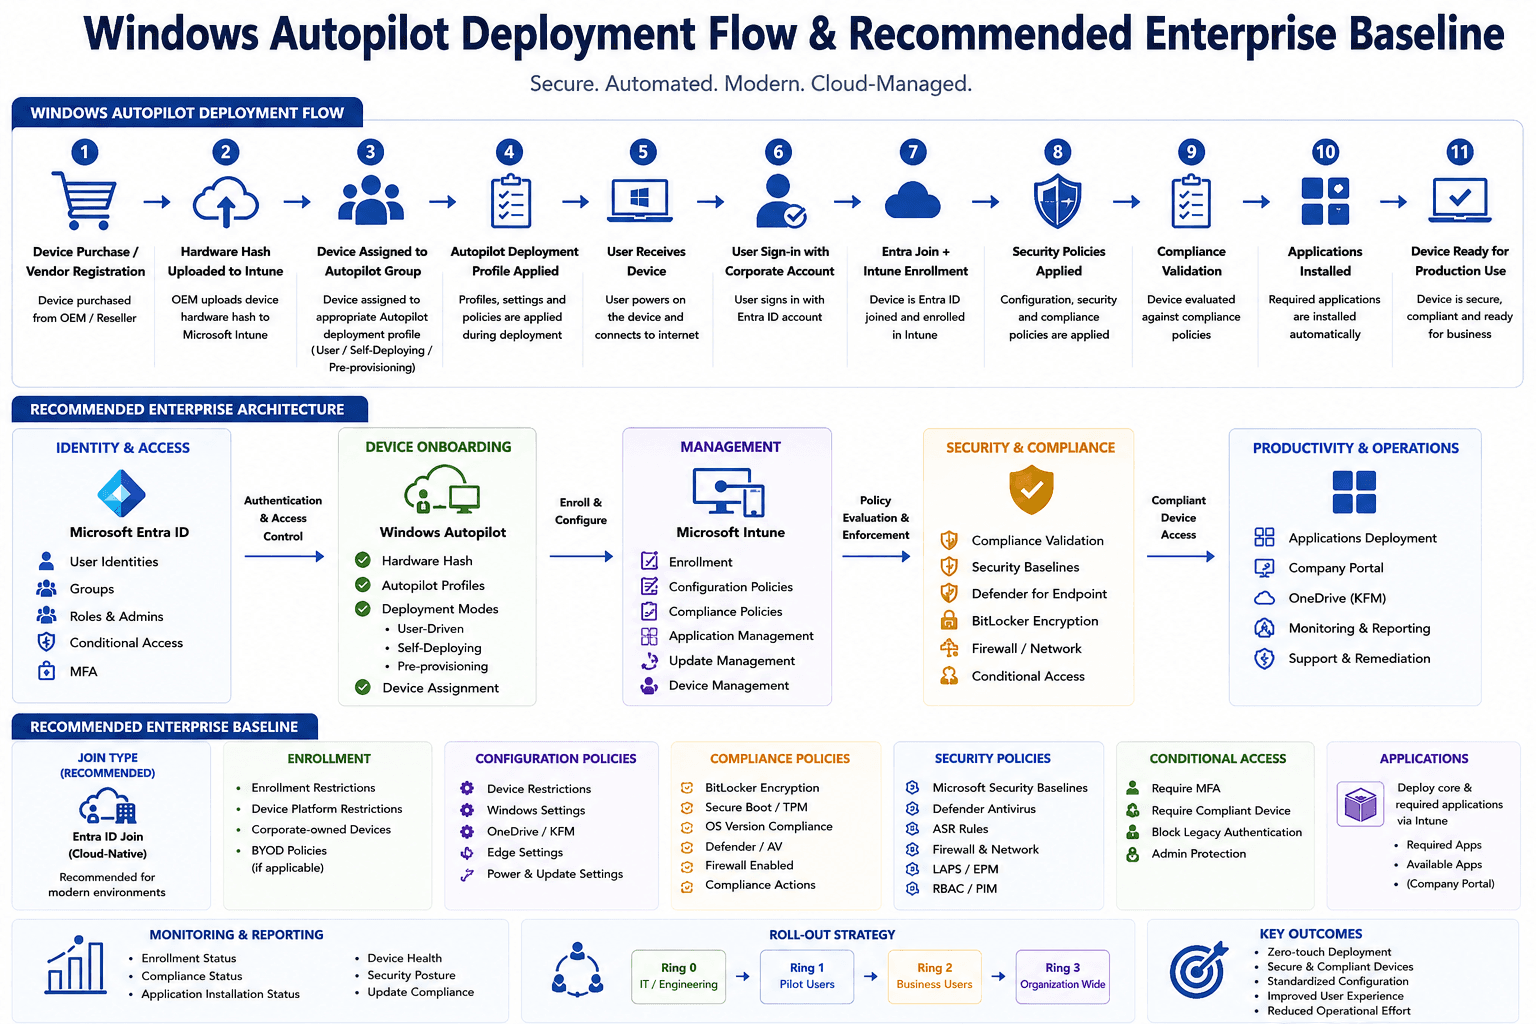
A complete guide to Windows Autopilot: every deployment mode explained, the full provisioning flow step by step, and the enterprise baseline every organisation should build on top of it.
Every Monday morning our team needed a full compliance report from Intune. I got tired of doing it manually, so I automated the whole thing with PowerShell and Microsoft Graph API. Here is exactly how I did it.

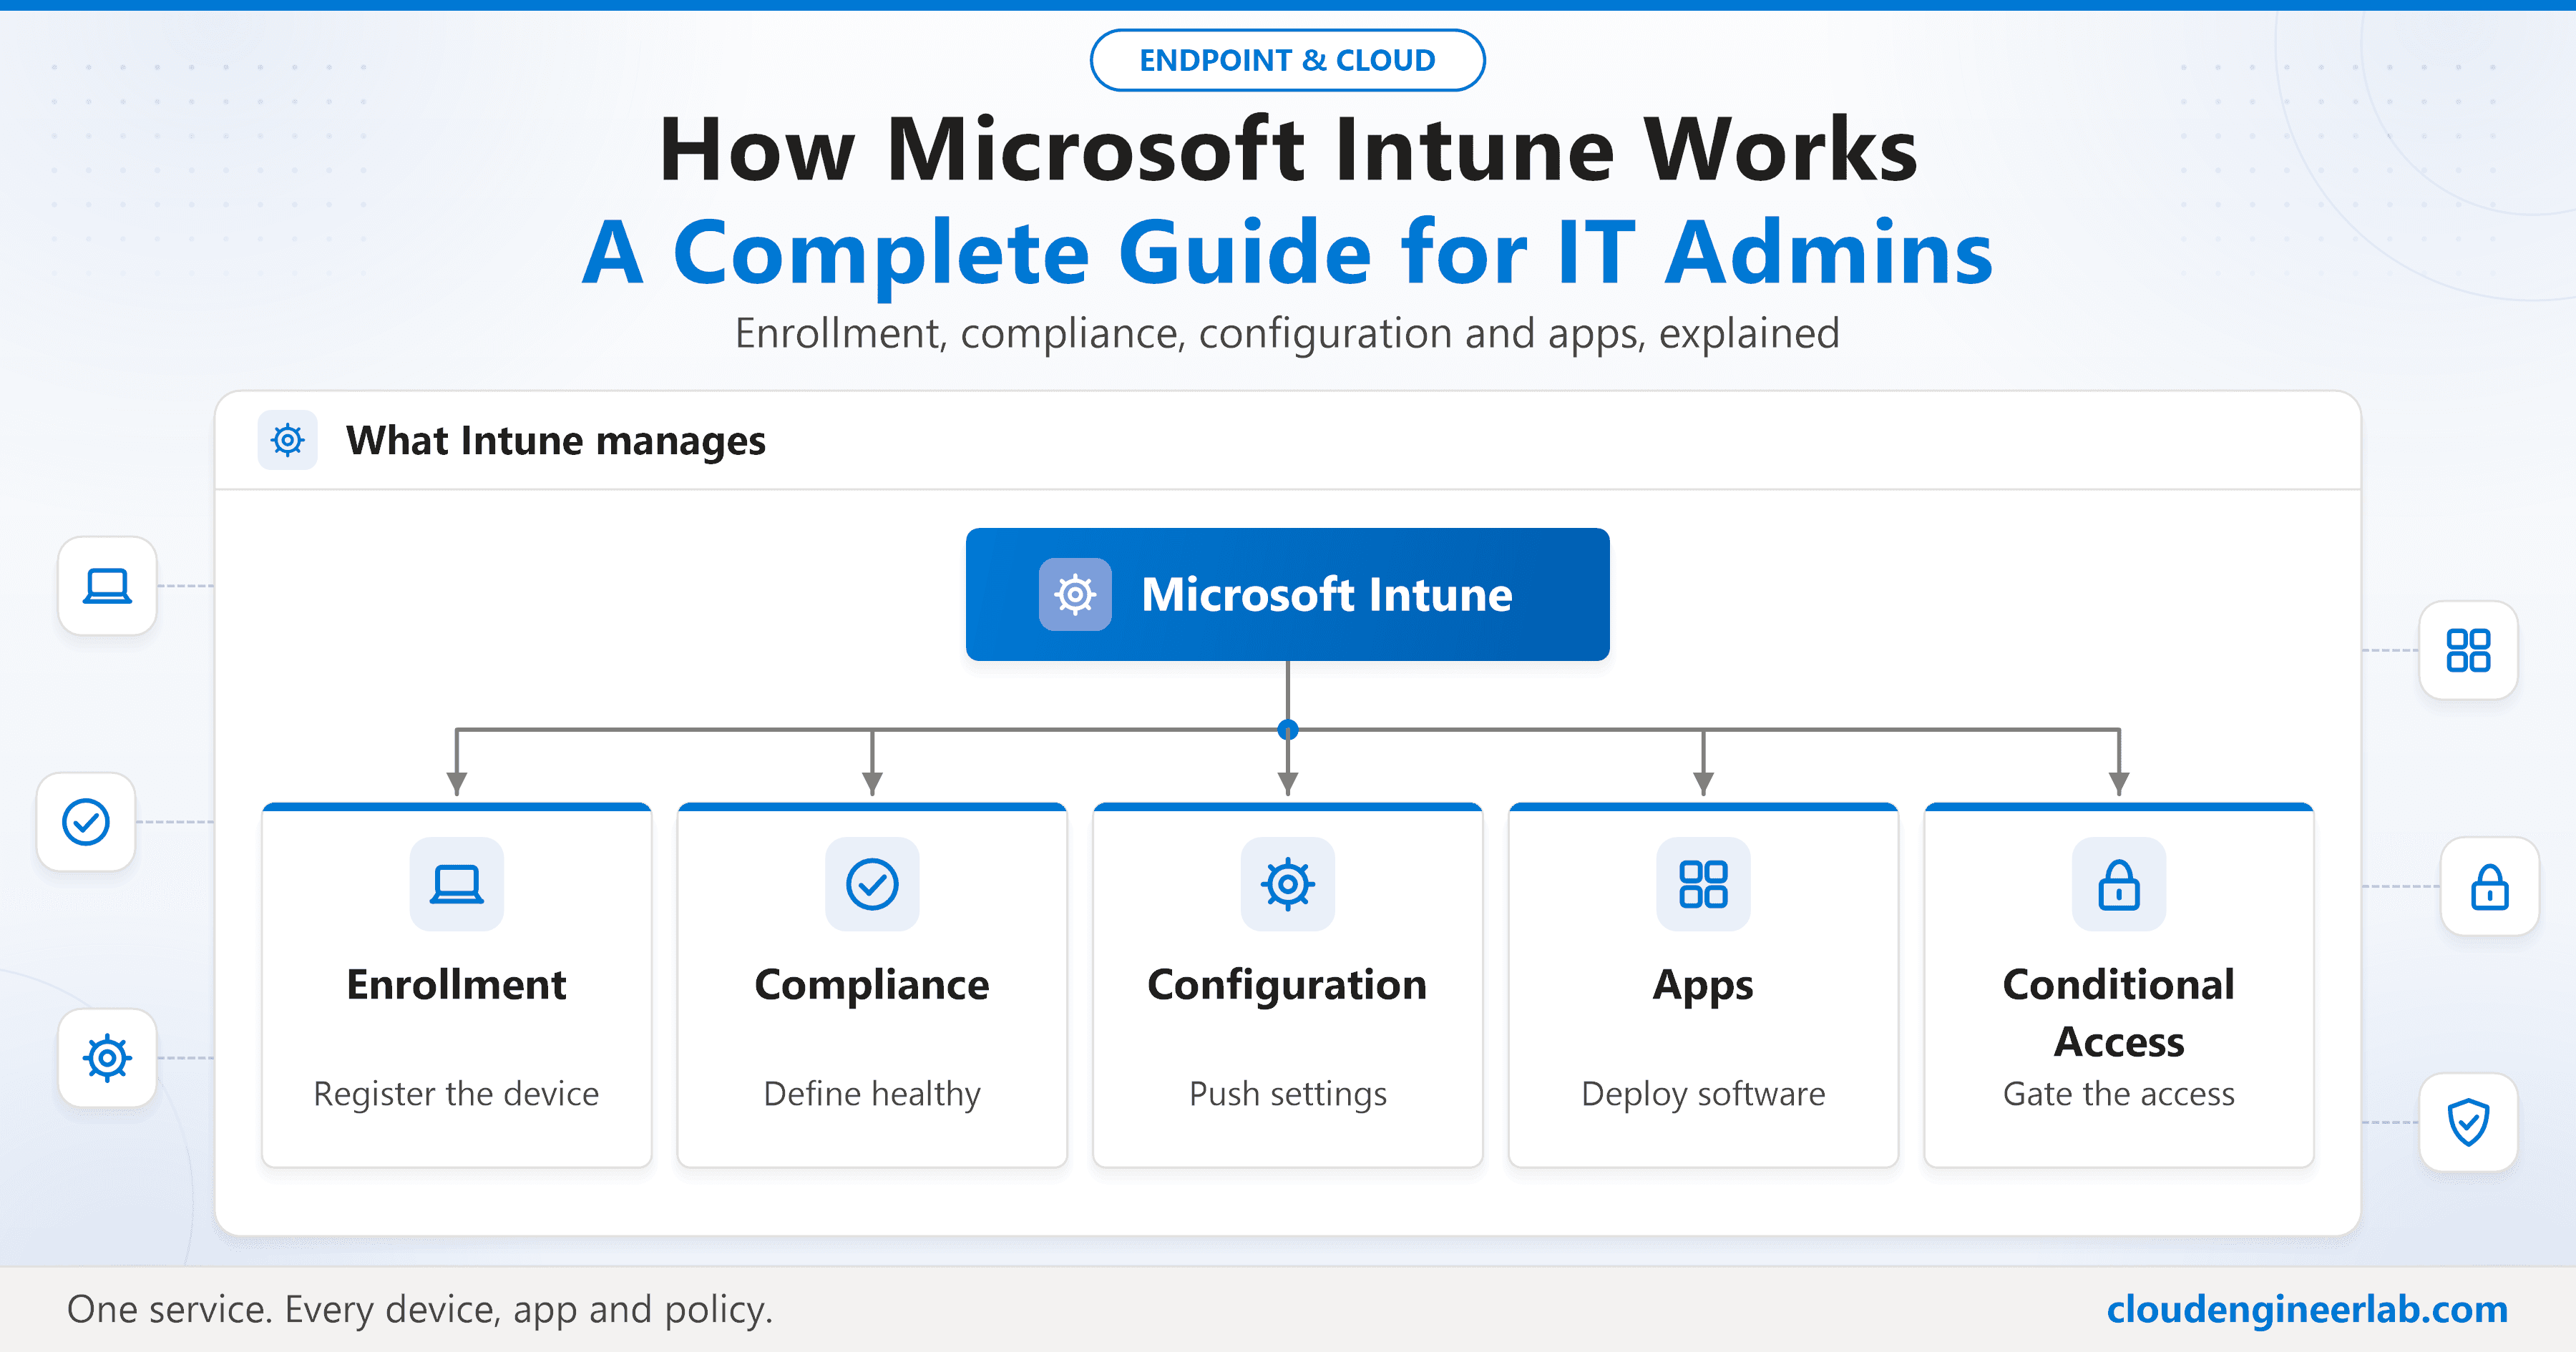
Microsoft Intune is the backbone of modern endpoint management. This guide explains how it works, how devices get enrolled, how compliance is enforced, and how it connects to Azure AD, with real-world examples from production environments.