Enterprise Application Management in Microsoft Intune: The Complete Guide
Deploying an app is the easy part. Protecting its data, configuring it on arrival, and retiring it cleanly is where most app management actually lives.
21 posts

Deploying an app is the easy part. Protecting its data, configuring it on arrival, and retiring it cleanly is where most app management actually lives.

Not how many applications you have. Whether they actually reached the devices they were supposed to, and specifically why the ones that didn't, didn't.

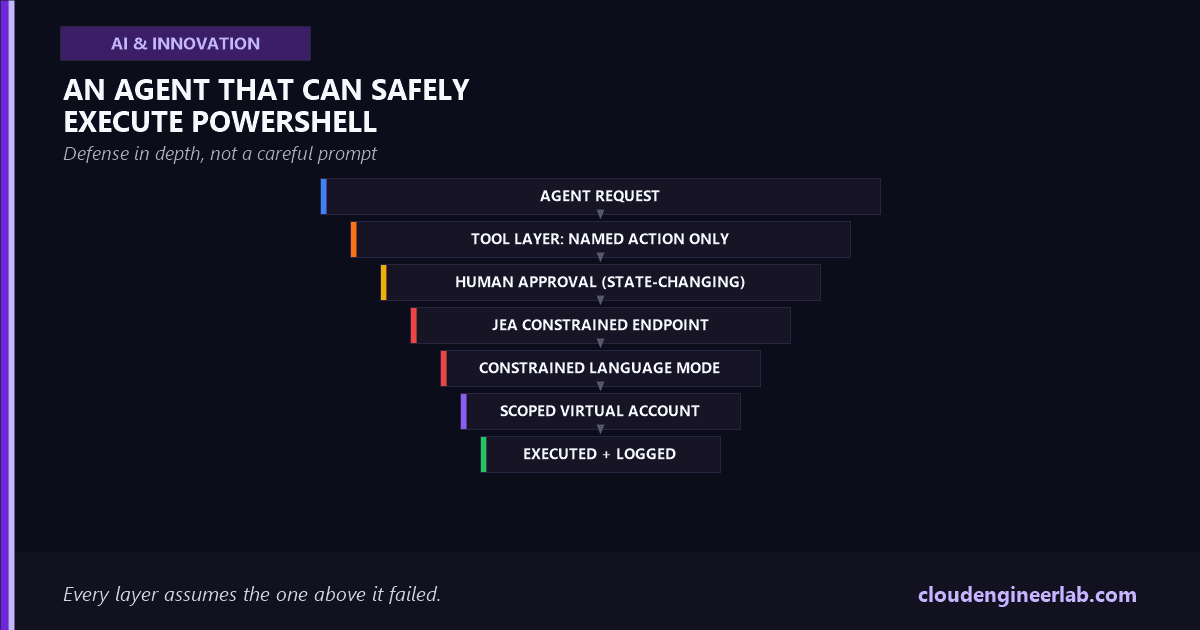
PowerShell can touch nearly everything on a Windows estate. Here's the layered architecture that lets an agent use it without becoming the attacker's shell.

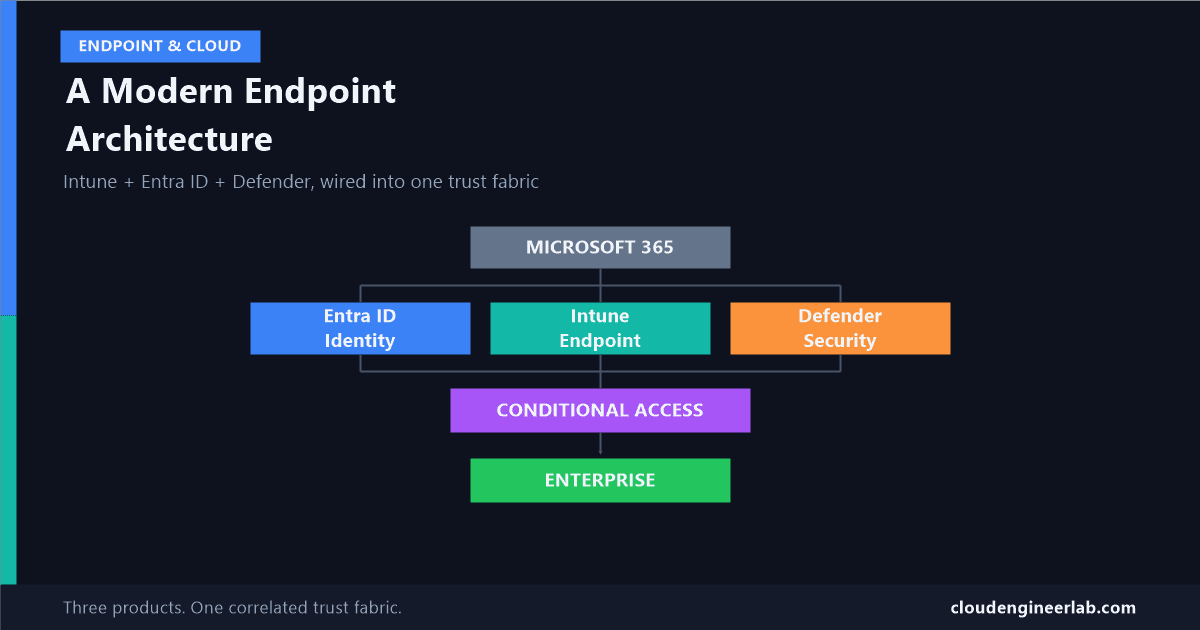
These three products aren't separate tools bolted together, they're one correlated trust fabric. Most tenants deploy all three and never actually wire them into it.

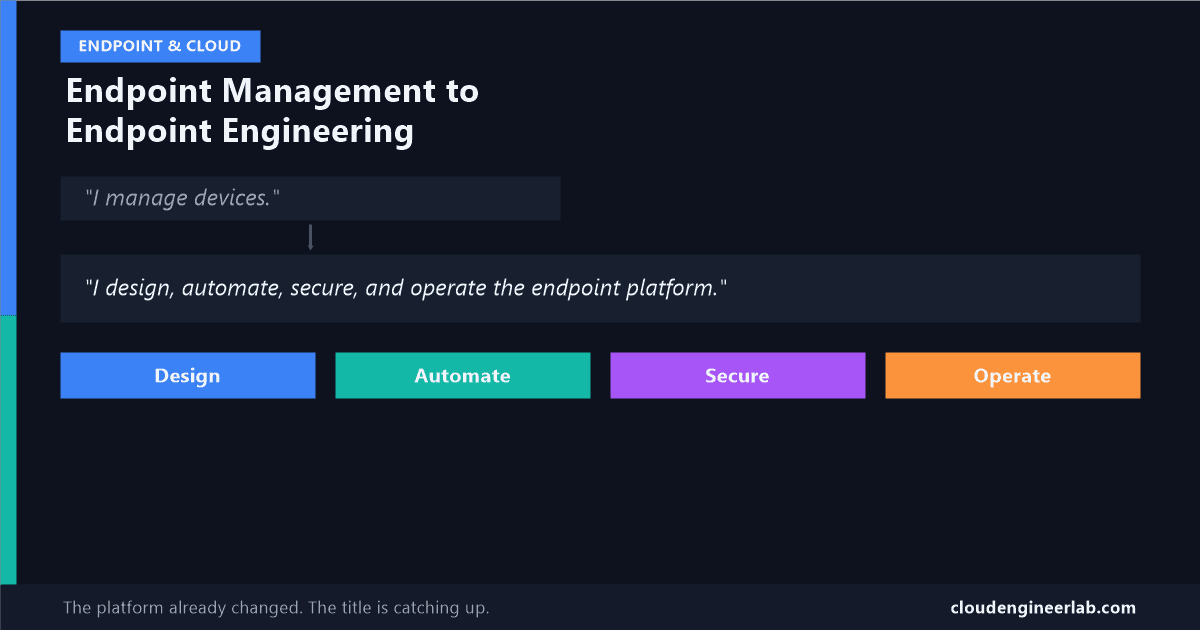
The routine parts of endpoint admin are being automated away, by Microsoft itself. What's left is a genuinely different job, and most job titles haven't caught up yet.

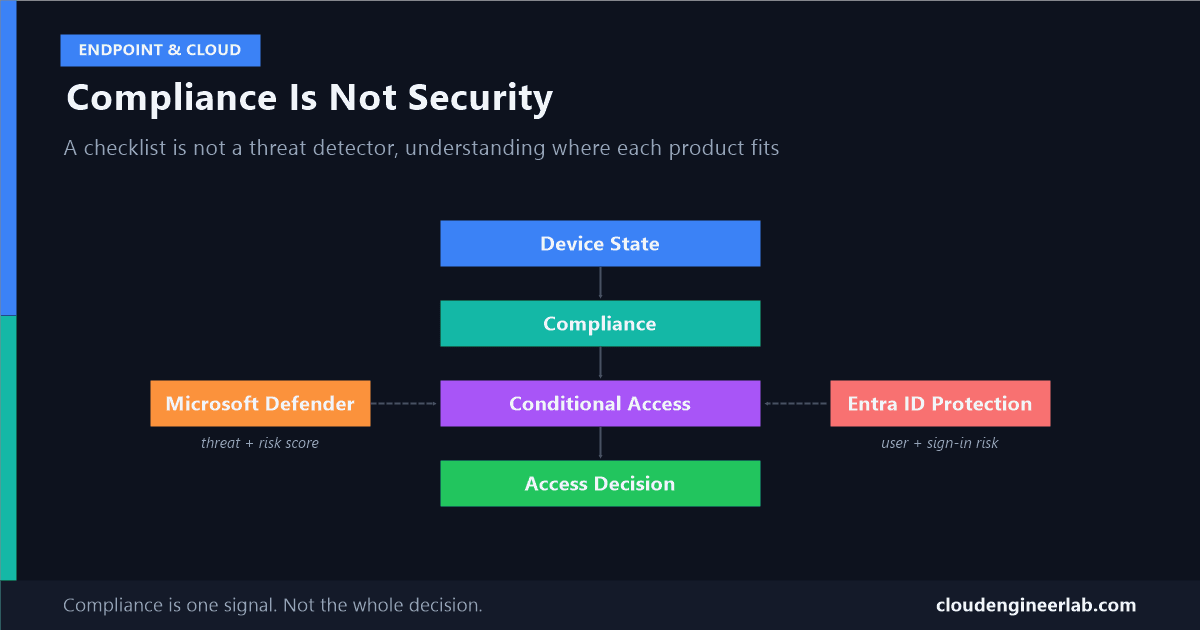
A fully patched, encrypted, PIN-locked device can still be actively compromised. Here's why compliance is a checklist, not a security guarantee, and what actually is.

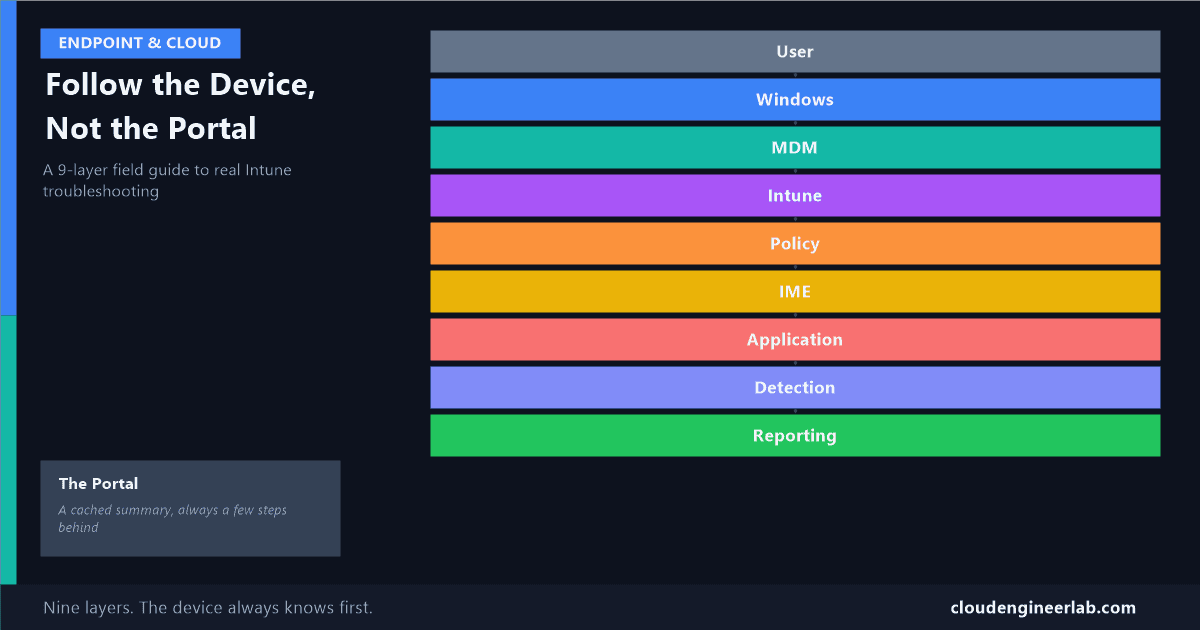
The admin centre is a reported view assembled from several independent systems, each with its own delay. Here's where the actual truth lives, layer by layer.

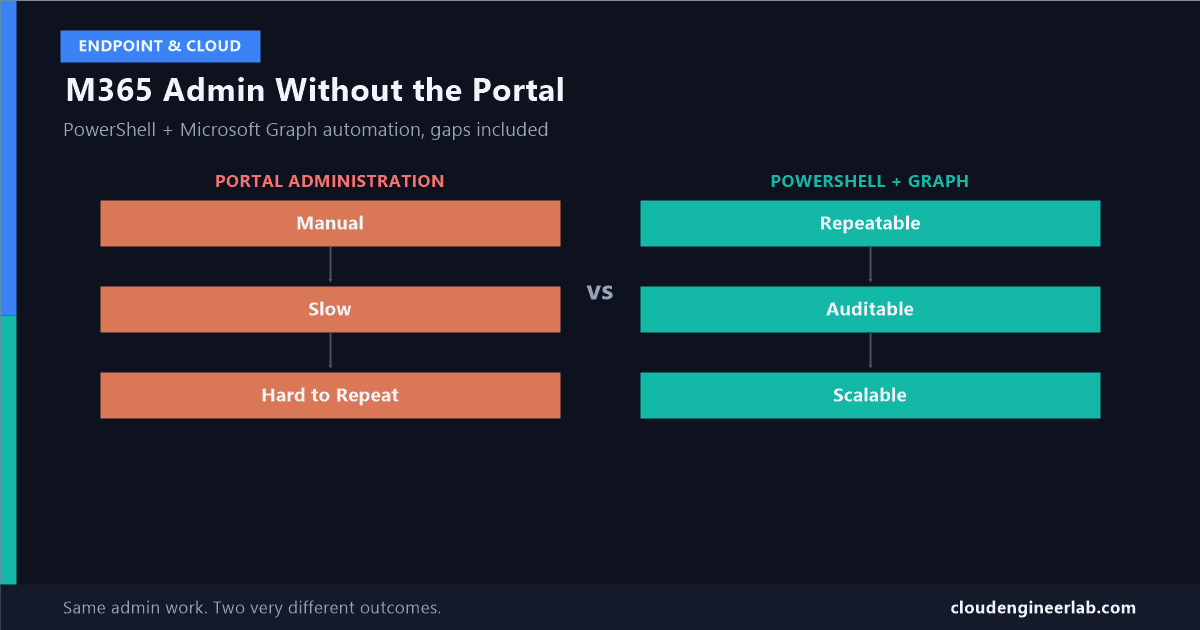
Manual admin work doesn't just cost time, it's unrepeatable by design. Here's what actually changes when you move it to PowerShell and Graph, honestly, gaps included.

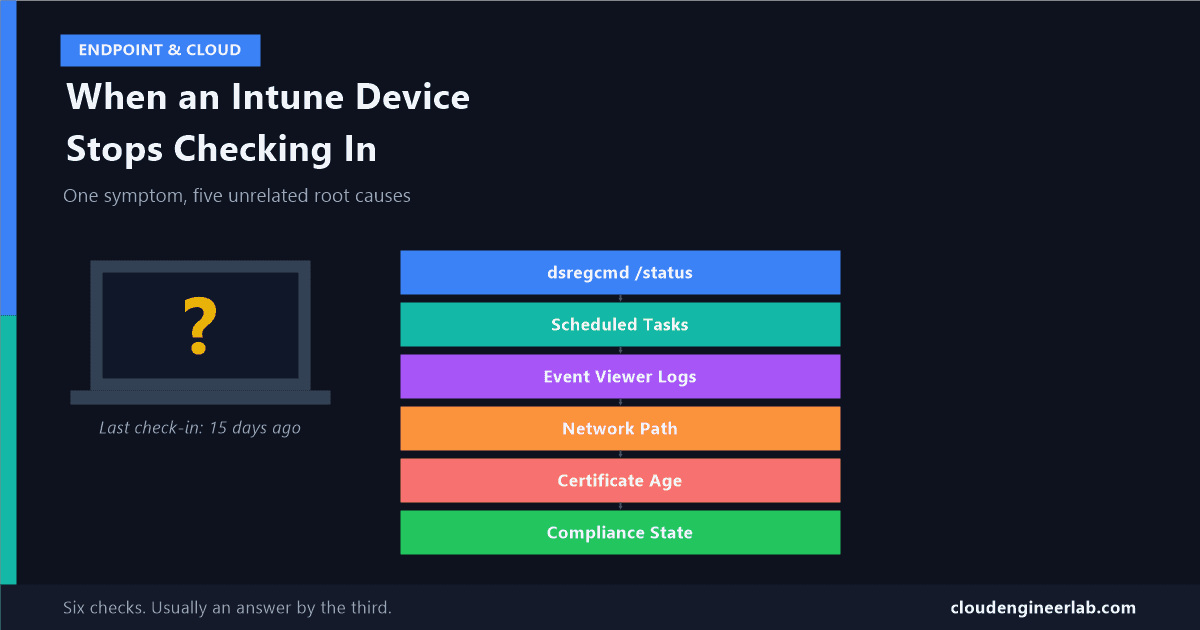
"Hasn't checked in" isn't one problem, it's at least five different problems wearing the same badge. A real diagnostic flow, log by log, command by command.

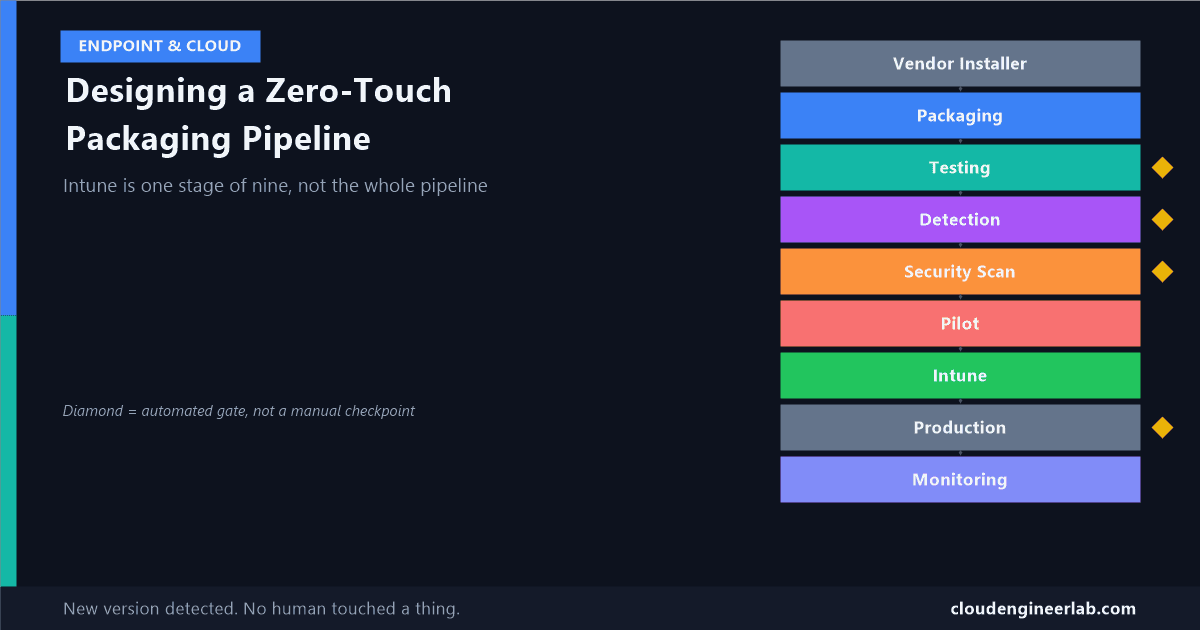
Intune is one stage in a nine-stage pipeline, not the whole story. Real tools for packaging, testing, scanning, and gating an app before it ever reaches a device.

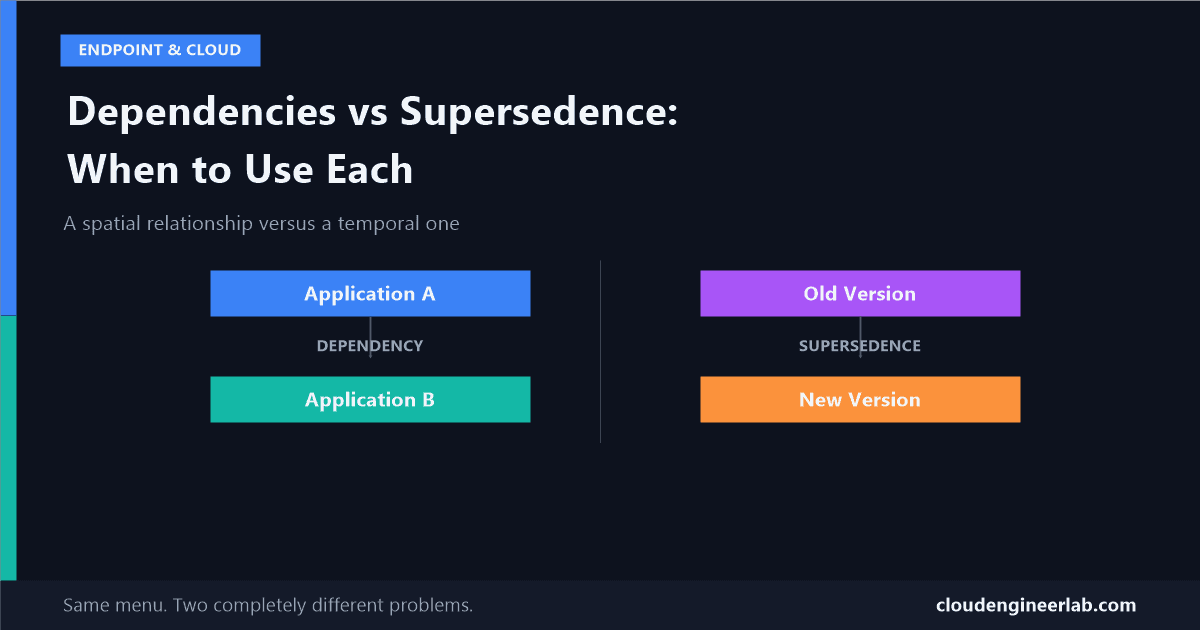
Both live in the same 'app relationships' menu, and picking the wrong one causes two very different failure modes. Here's the actual architecture distinction.

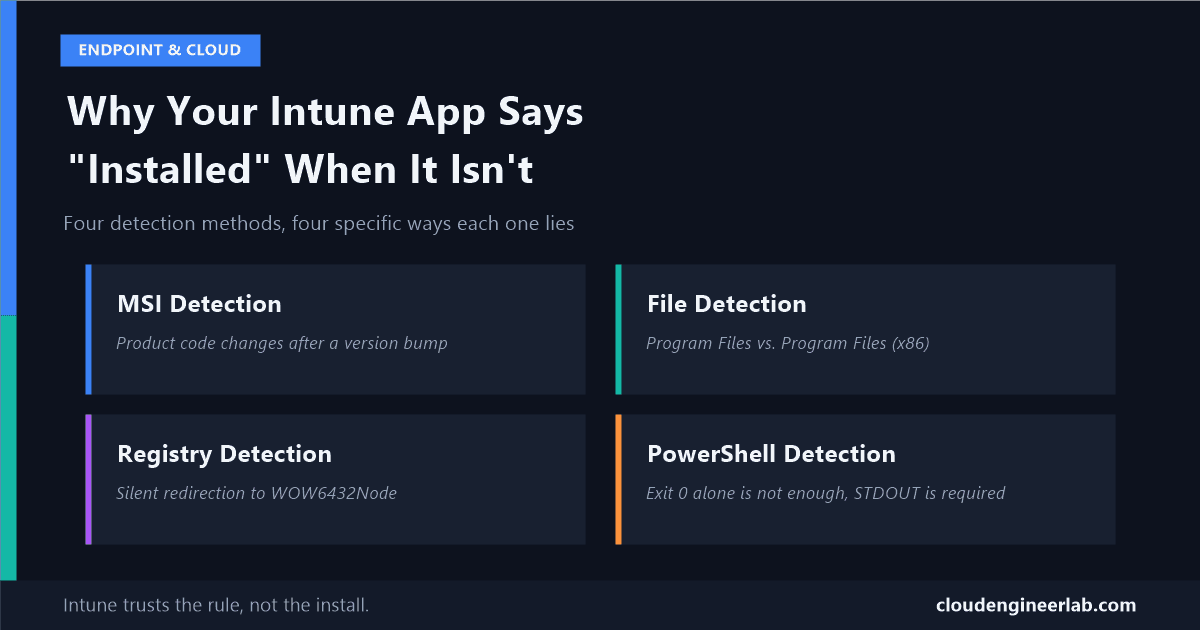
MSI product codes, WOW6432Node redirection, PowerShell STDOUT rules, and the HKCU trap: the practical reasons detection rules lie, and how to fix each one.

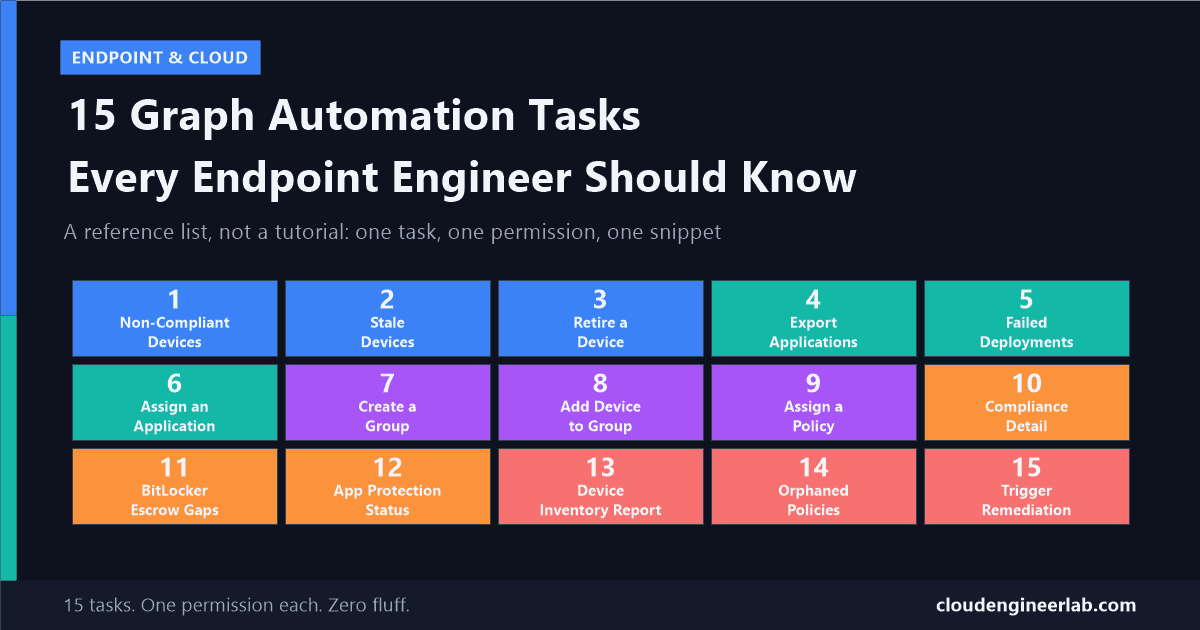
A reference list of 15 real, working Graph tasks, from finding stale devices to triggering remediation scripts, each with the exact permission and code.

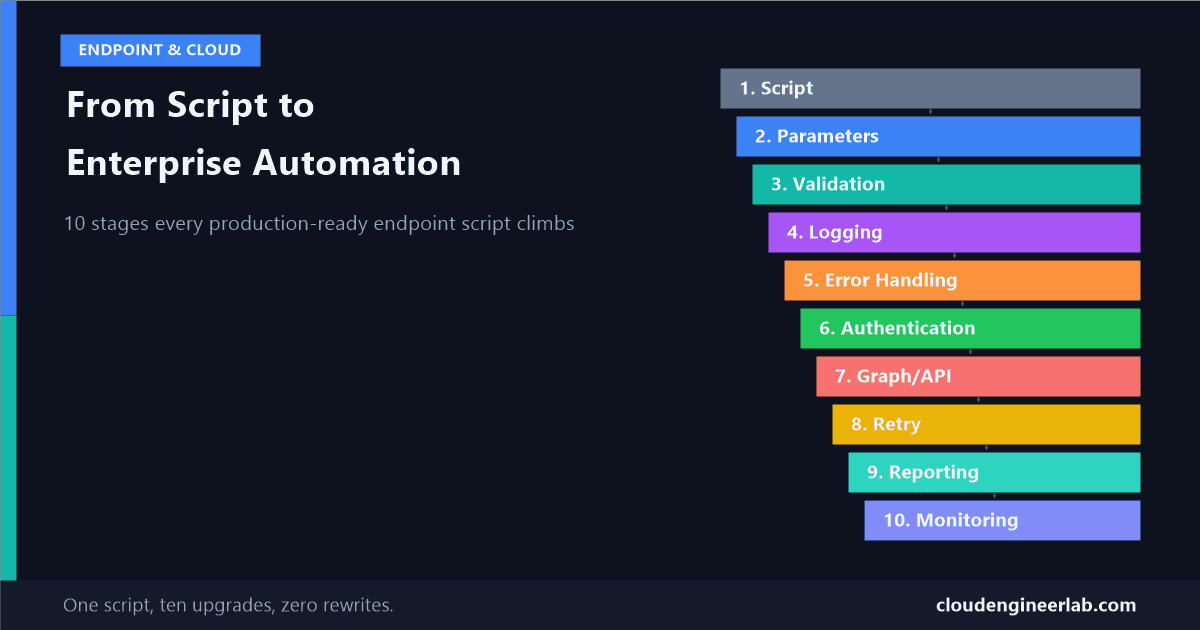
A single script evolves through 10 concrete stages, from hardcoded and fragile to authenticated, retried, reported, and monitored in production.

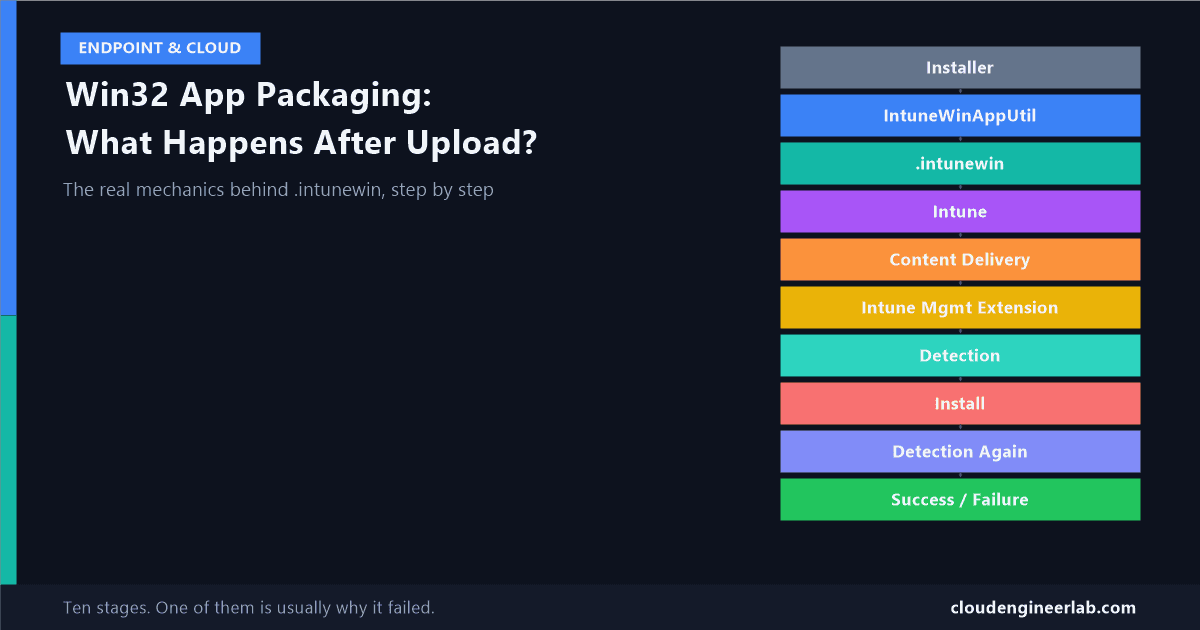
The mechanics behind the black box: what IntuneWinAppUtil actually does to your installer, how the file reaches a device, and why detection rules run twice.

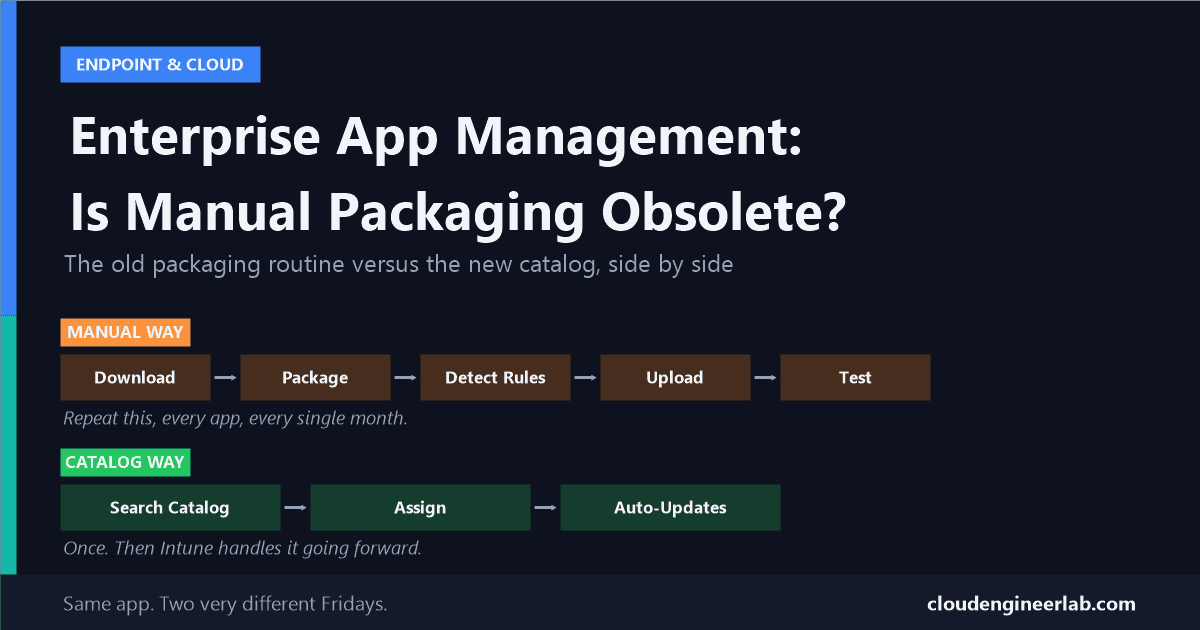
Microsoft now packages hundreds of common apps for you. Here's what that actually replaces, and where hand-packaging Win32 apps still holds its ground.

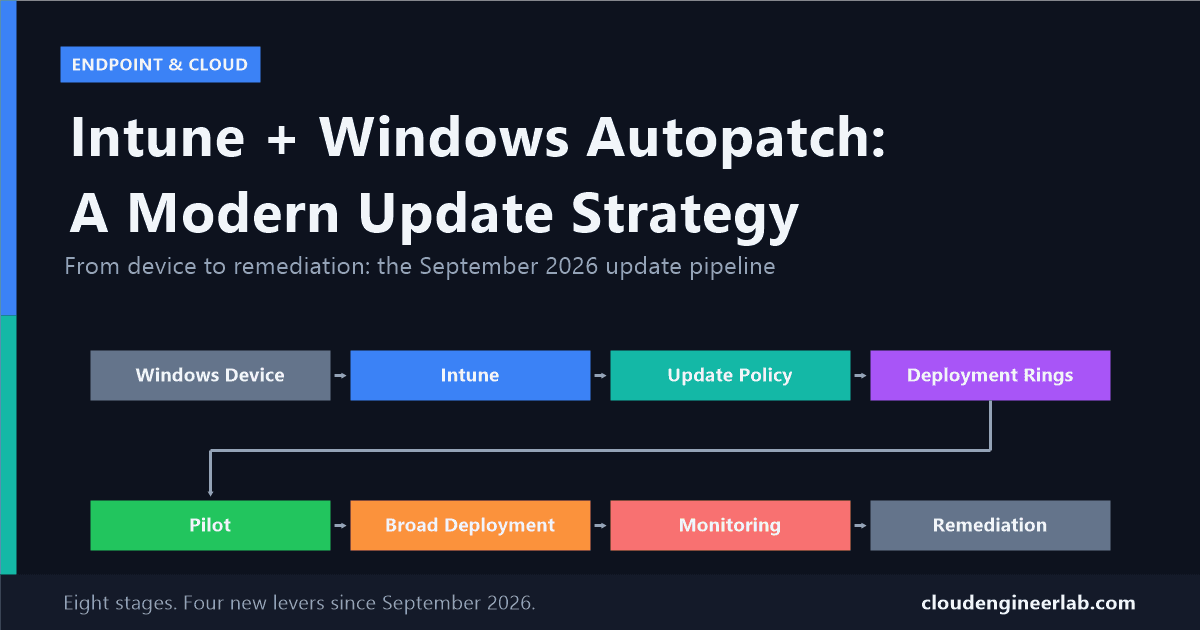
September 2026 gives Autopatch real control over quality updates, .NET Framework updates, and machine recovery. Here's how to design a ring strategy around it.

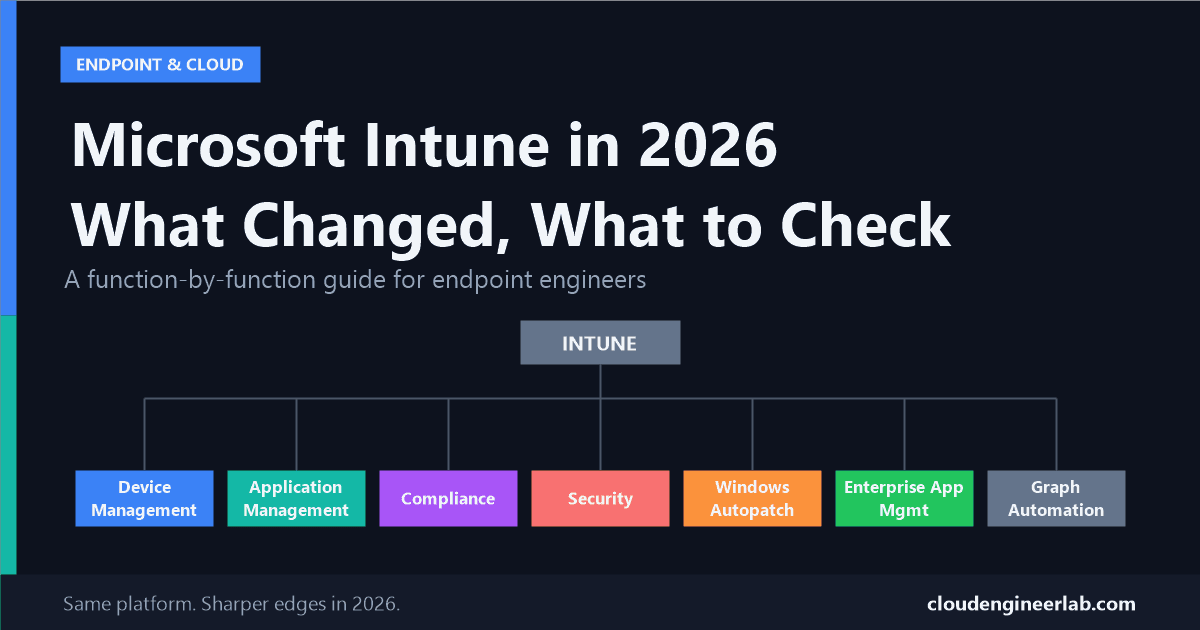
A function-by-function breakdown of what actually changed in Intune this year, and the specific checks every endpoint engineer should run in their own tenant.

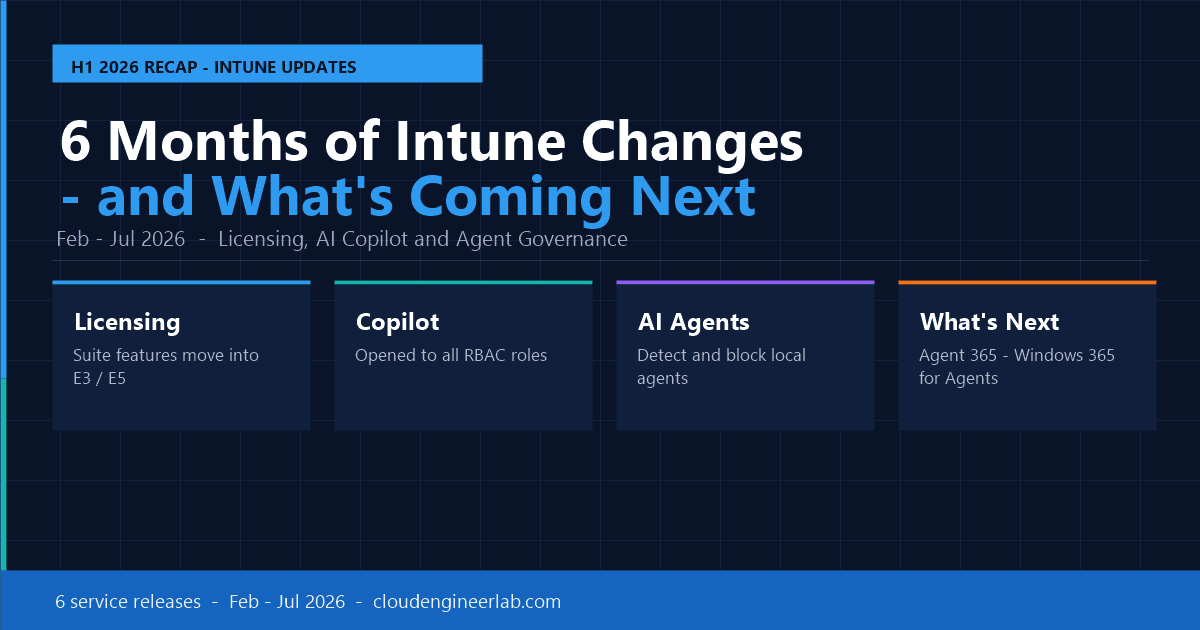
From the February to July 2026 service releases, Intune changed faster than ever: licensing, AI agents, and security. Here's what happened and what's next.

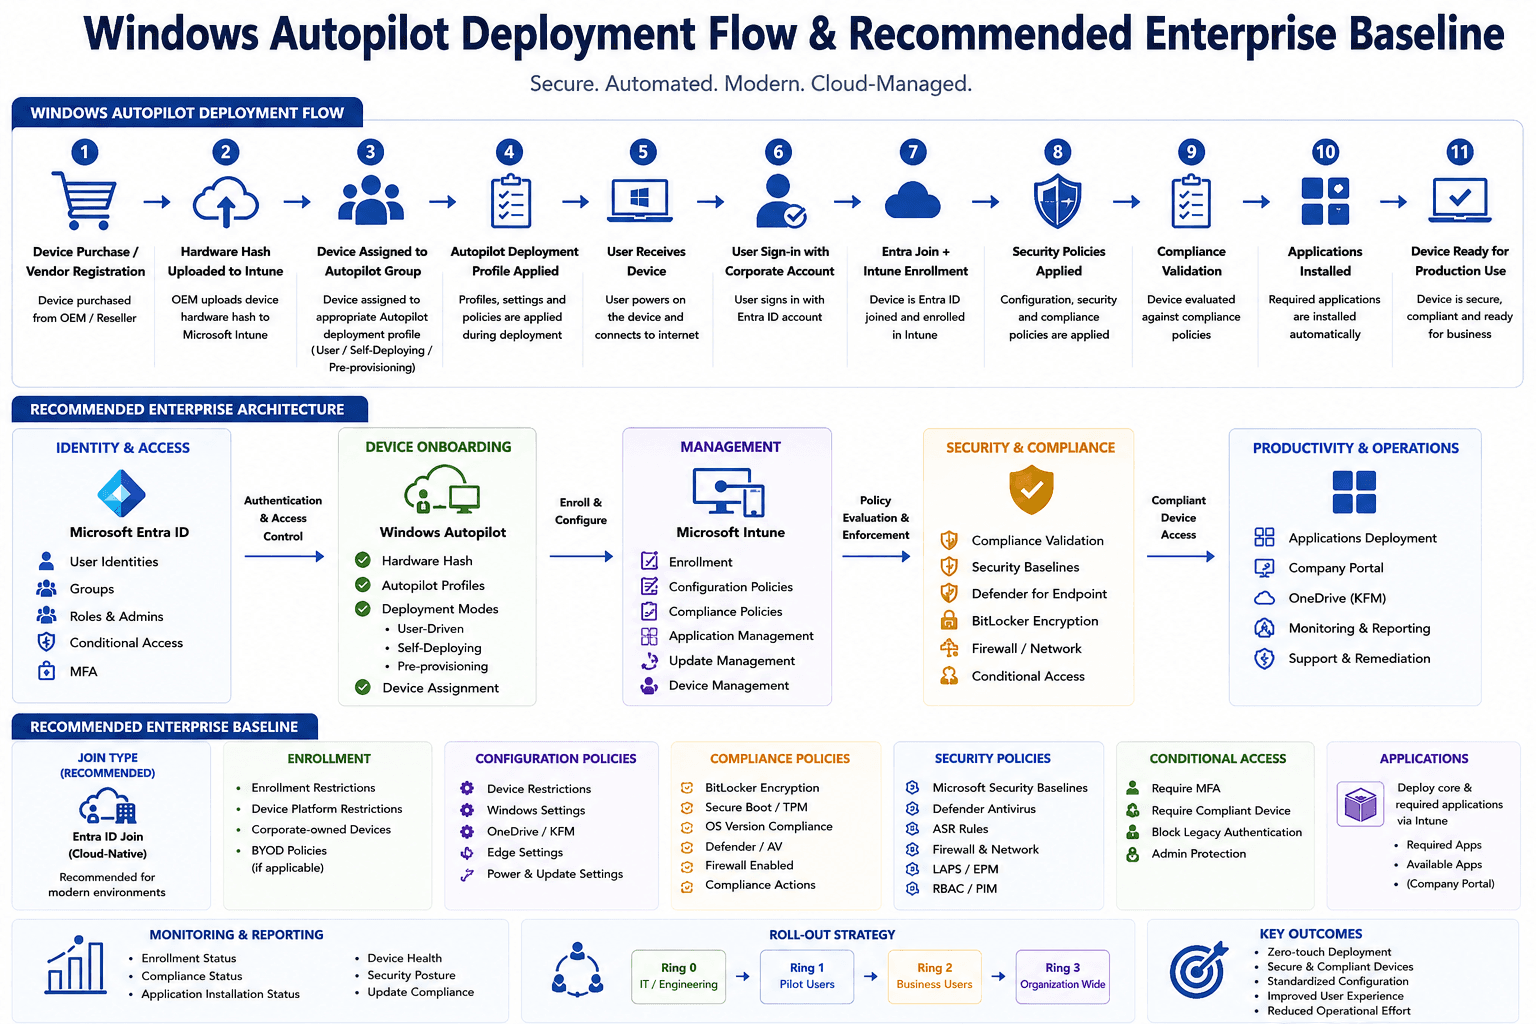
A complete guide to Windows Autopilot: every deployment mode explained, the full provisioning flow step by step, and the enterprise baseline every organisation should build on top of it.

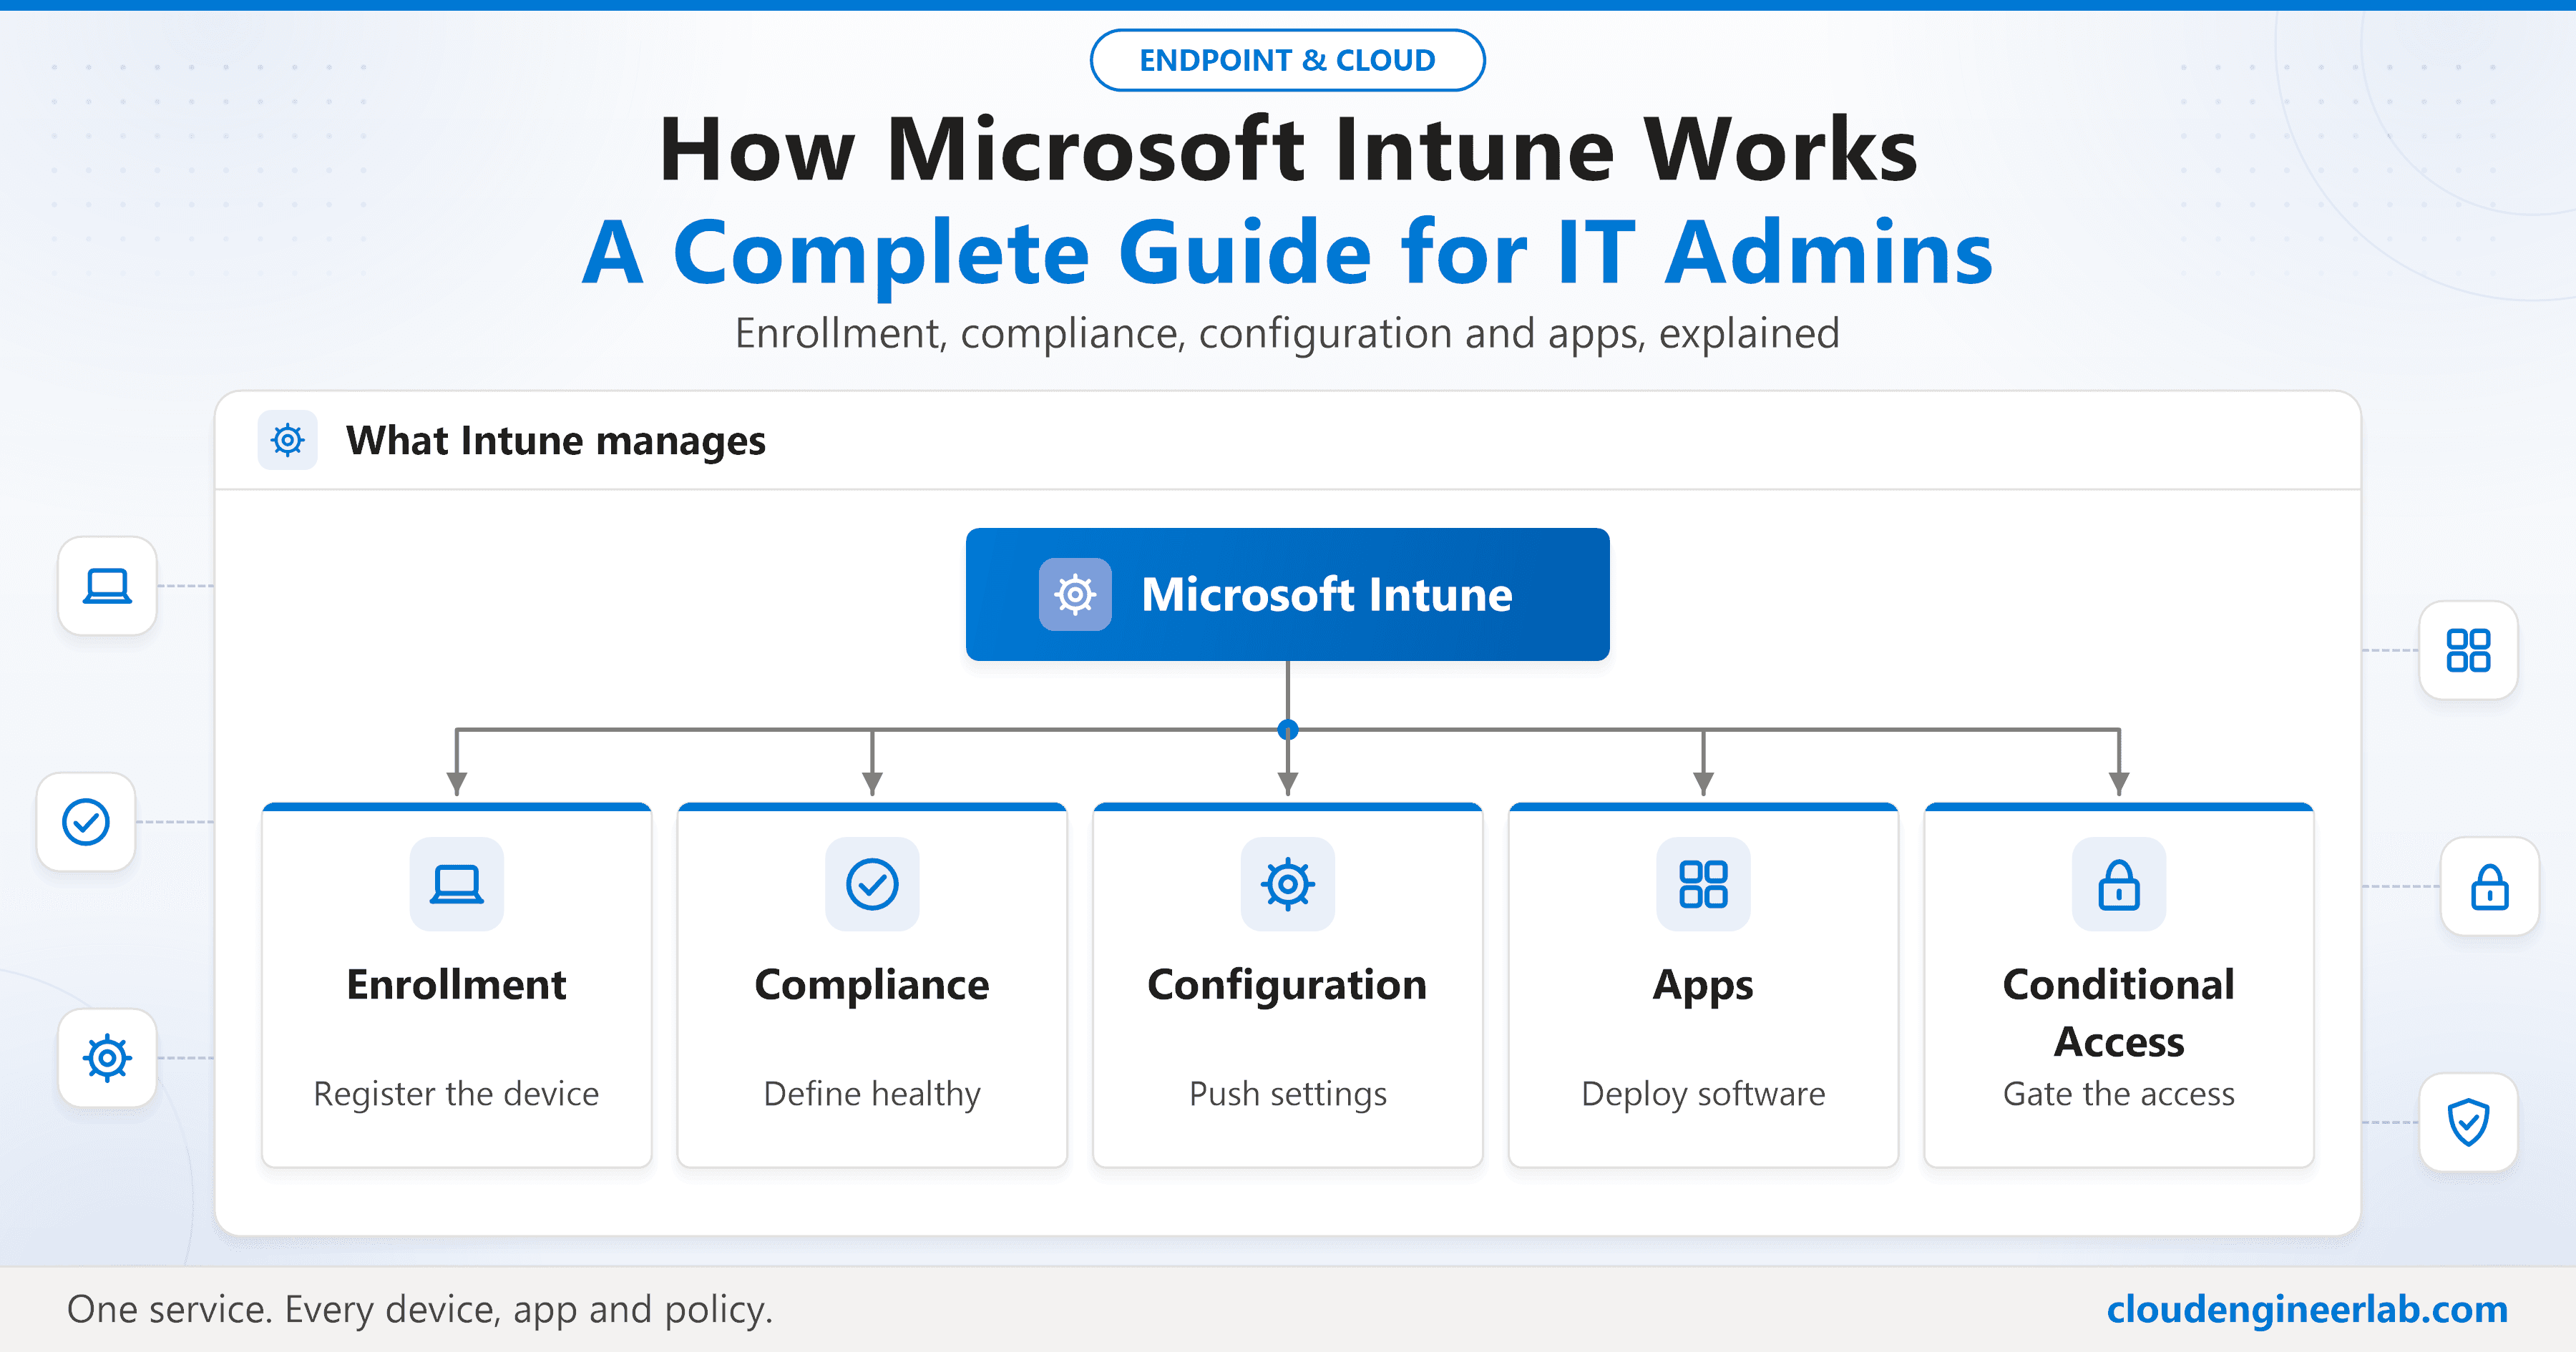
Microsoft Intune is the backbone of modern endpoint management. This guide explains how it works, how devices get enrolled, how compliance is enforced, and how it connects to Azure AD, with real-world examples from production environments.