Application Control: How to Stop Unapproved Software From Running
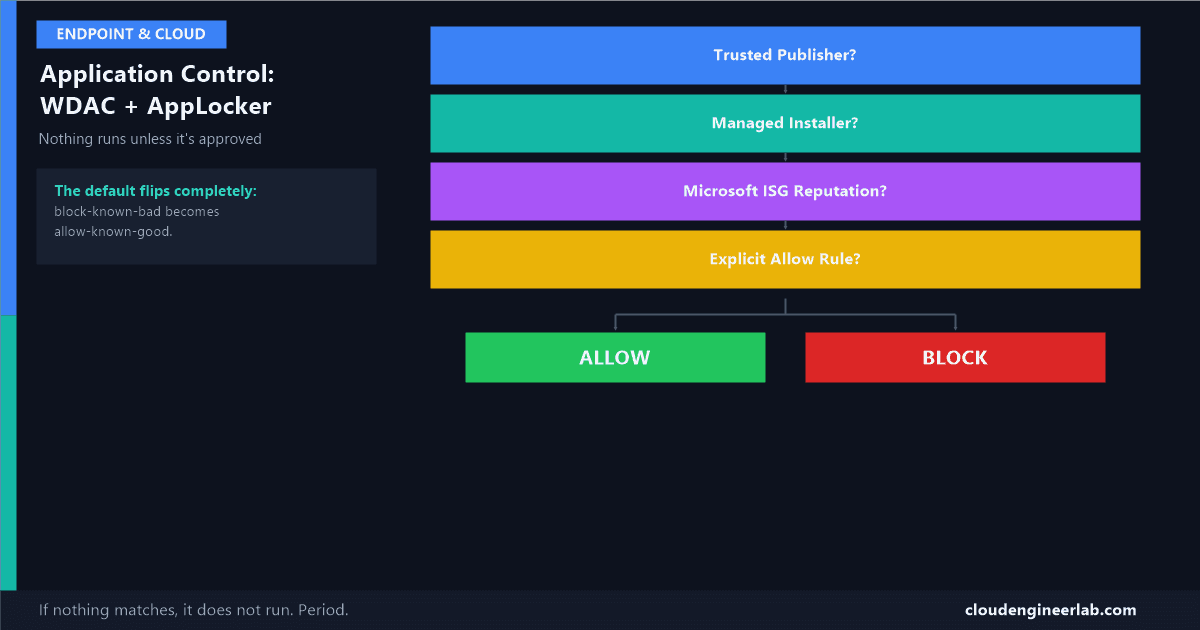
WDAC, AppLocker, and App Control for Business explained properly: how allowlisting actually decides what runs, and how to roll it out without breaking the fleet.
5 posts

WDAC, AppLocker, and App Control for Business explained properly: how allowlisting actually decides what runs, and how to roll it out without breaking the fleet.

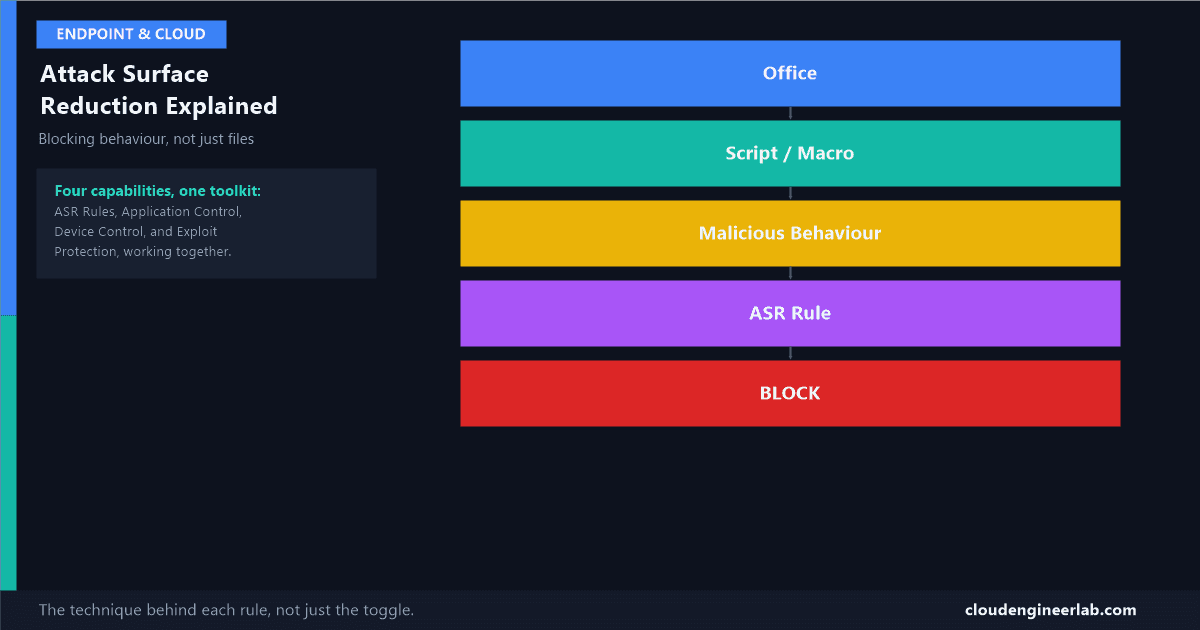
ASR rules don't detect malware, they block the specific techniques malware needs to work. Here's what each major rule actually stops, and how it fits into Intune's wider hardening toolkit.

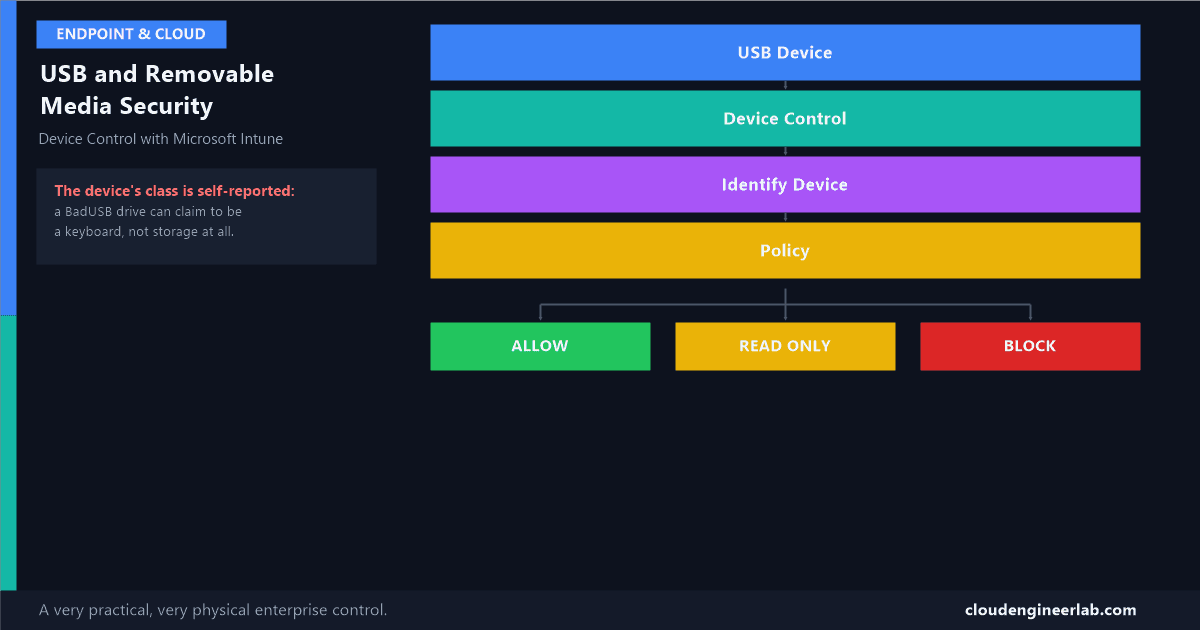
A USB drive is a fully hardened fleet's last unhardened door. How Intune actually identifies a plugged-in device and decides Allow, Block, or Read-only.

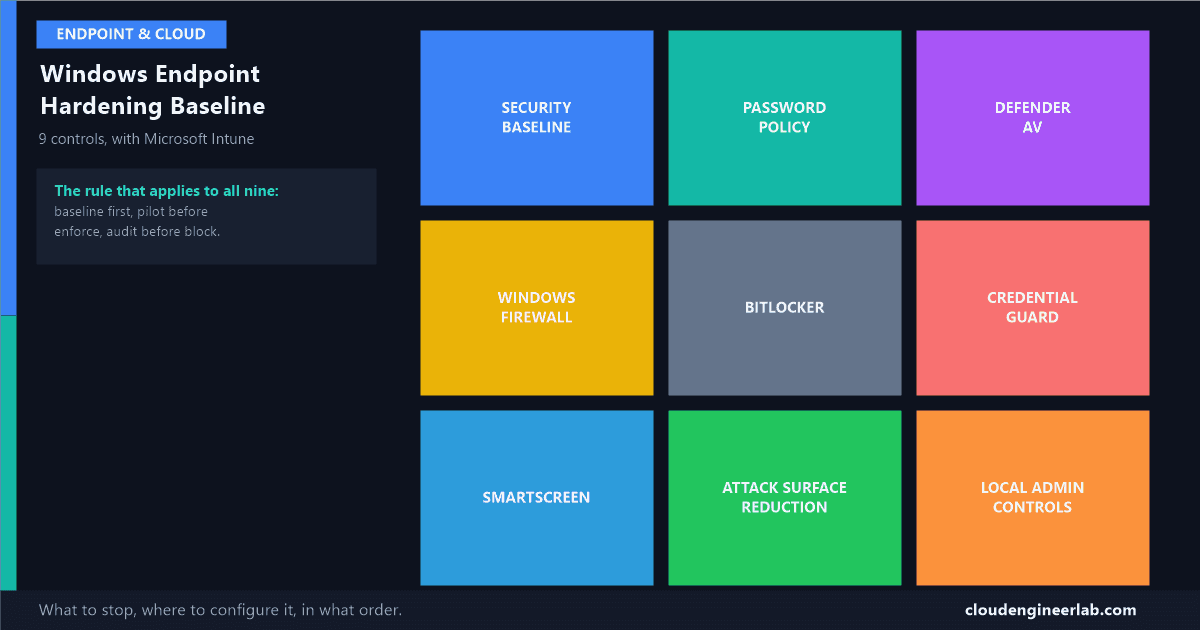
Nine controls that actually move the needle on Windows security, what each one stops, the exact Intune blade to configure it in, and the order to roll them out safely.

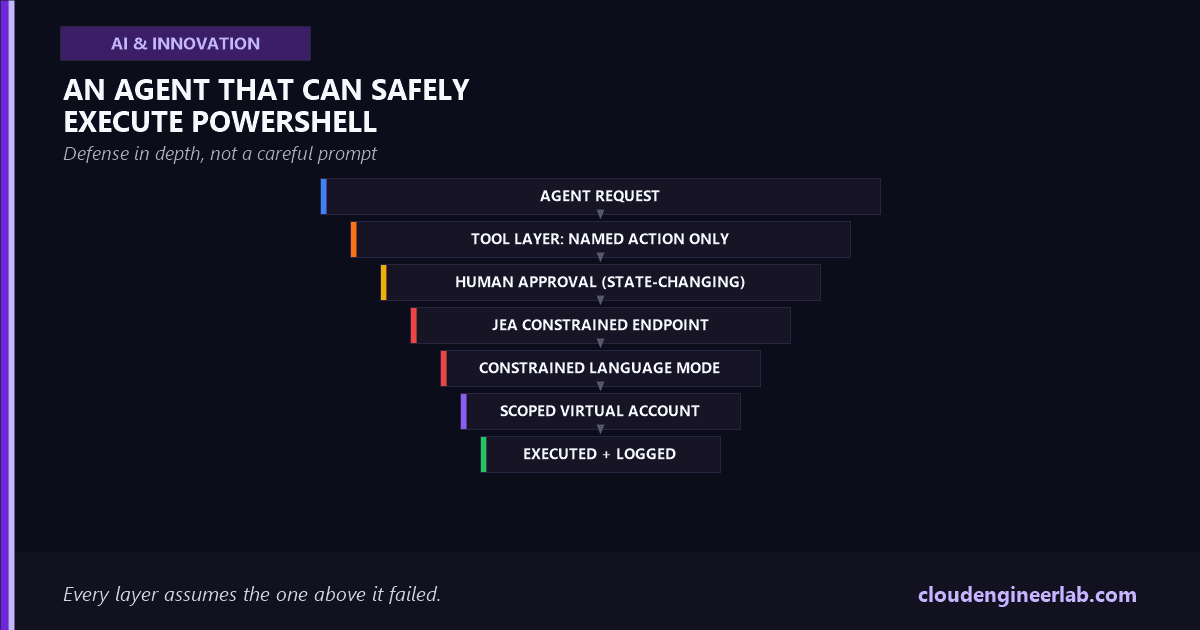
PowerShell can touch nearly everything on a Windows estate. Here's the layered architecture that lets an agent use it without becoming the attacker's shell.