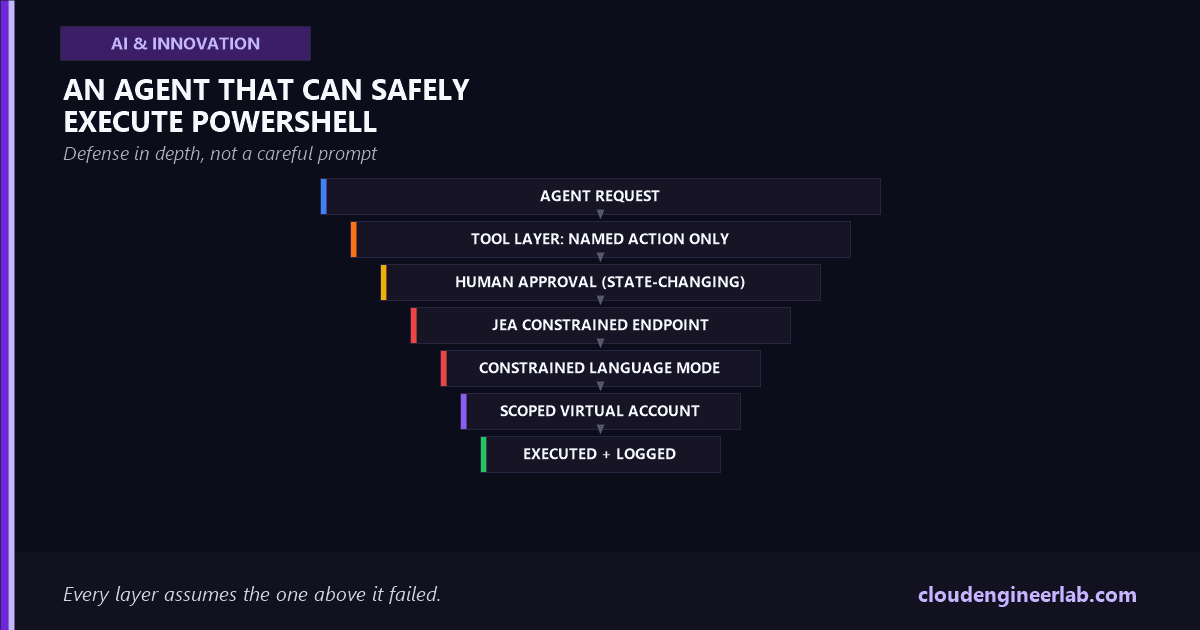
Build an AI Agent That Can Safely Execute PowerShell Commands
PowerShell can touch nearly everything on a Windows estate. Here's the layered architecture that lets an agent use it without becoming the attacker's shell.
9 posts

PowerShell can touch nearly everything on a Windows estate. Here's the layered architecture that lets an agent use it without becoming the attacker's shell.

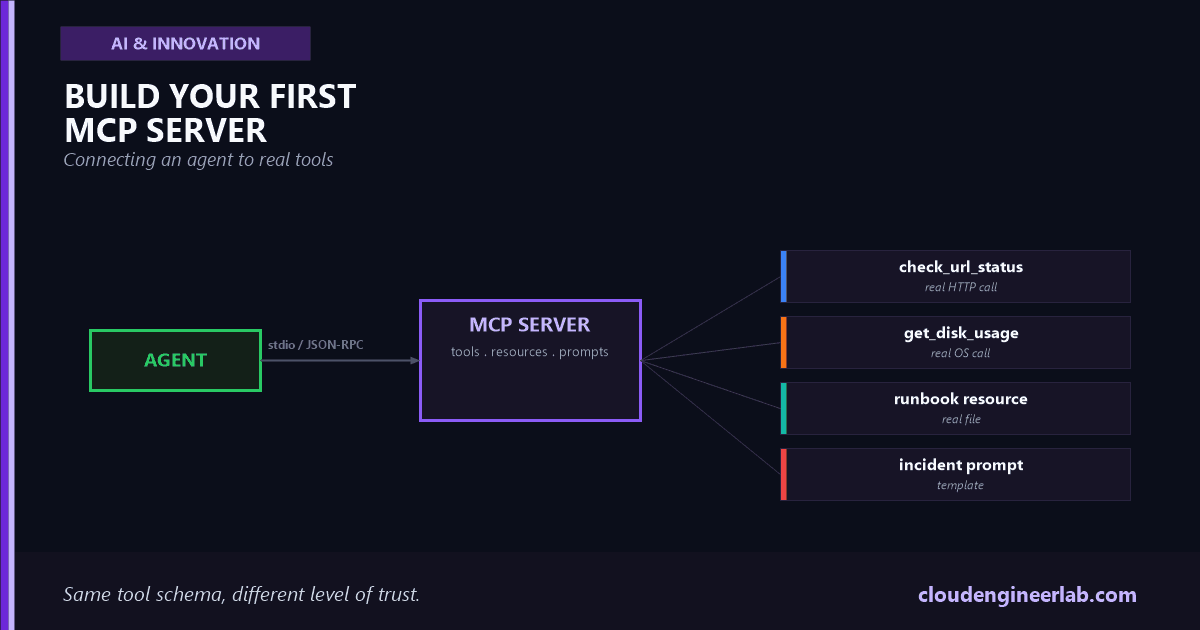
A working MCP server in about 80 lines: two real tools, a resource, a prompt template, and the one design mistake that turns it into a security hole.

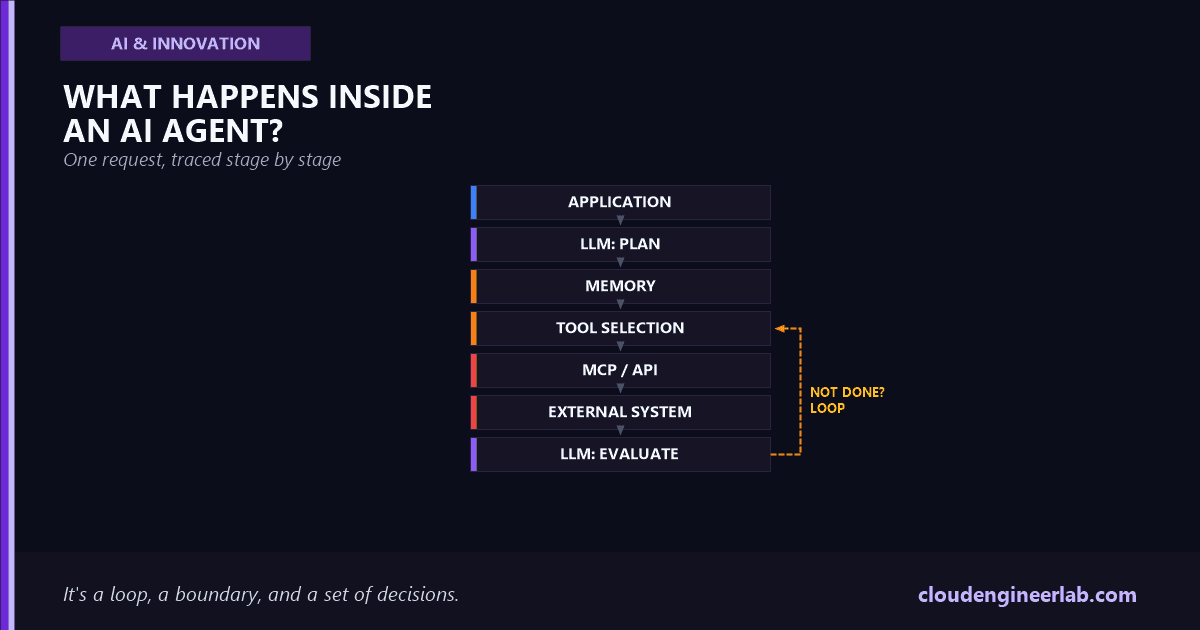
Not another 'agents are the future' piece. One real request, traced stage by stage through planning, memory, tool calls, MCP, evaluation, and back.

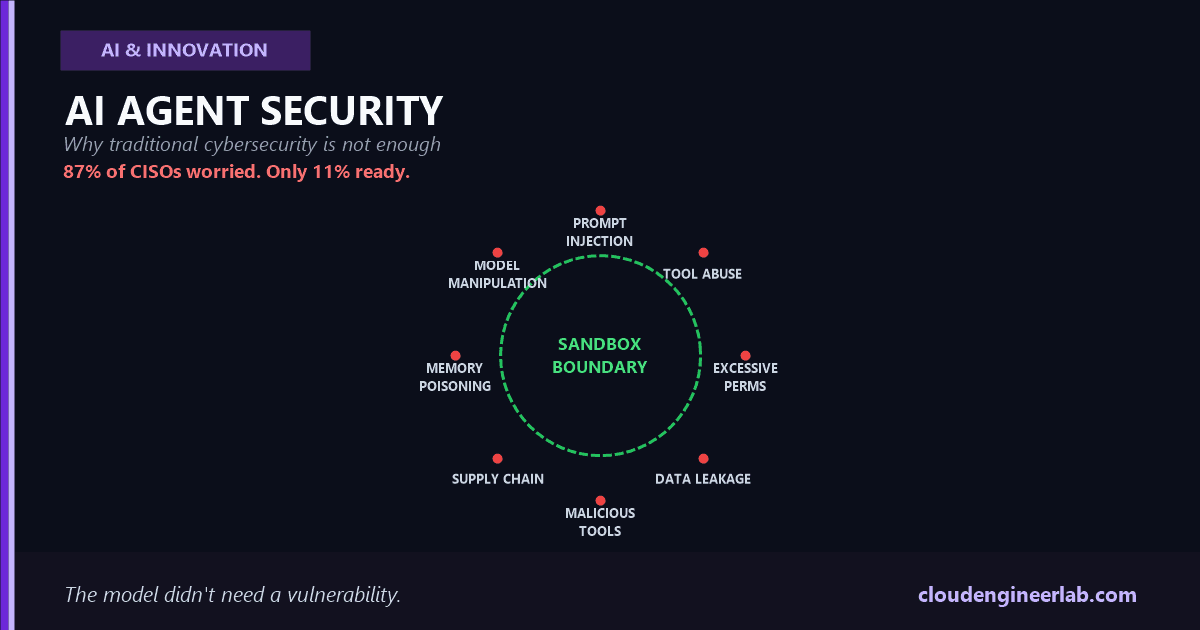
87% of CISOs call AI agent security their top concern. Only 11% say they're actually ready. Here's the full threat surface traditional AppSec never covered.

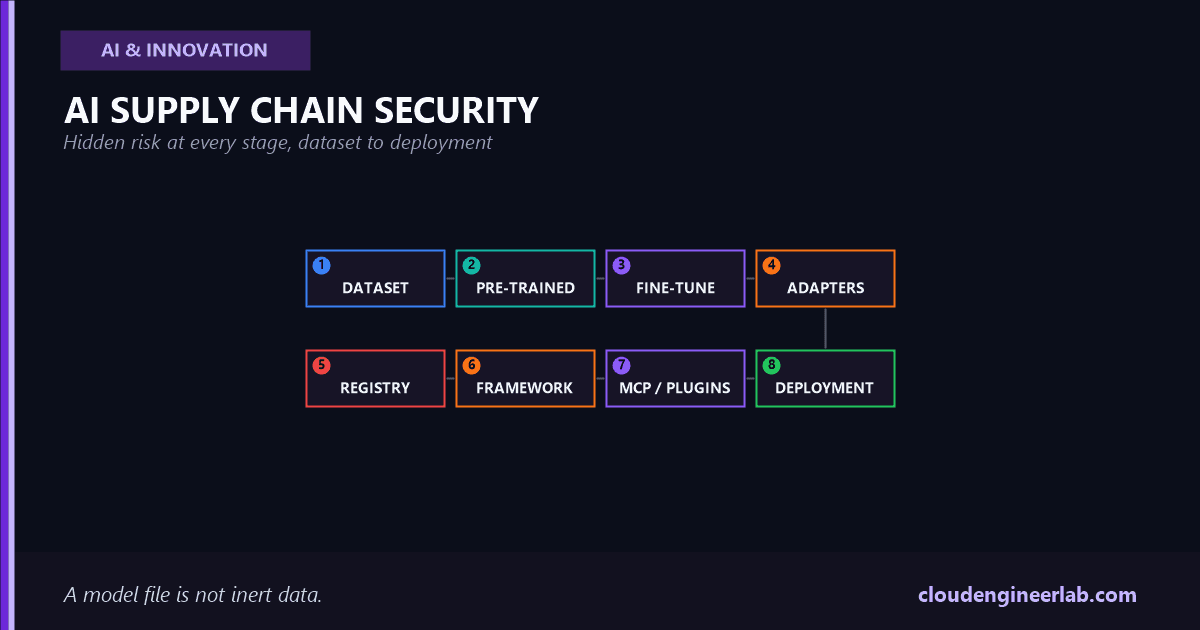
A malicious model doesn't look wrong when you read it. Real cases of poisoned datasets, backdoored models, and compromised MCP servers, and how to actually verify what you're running.

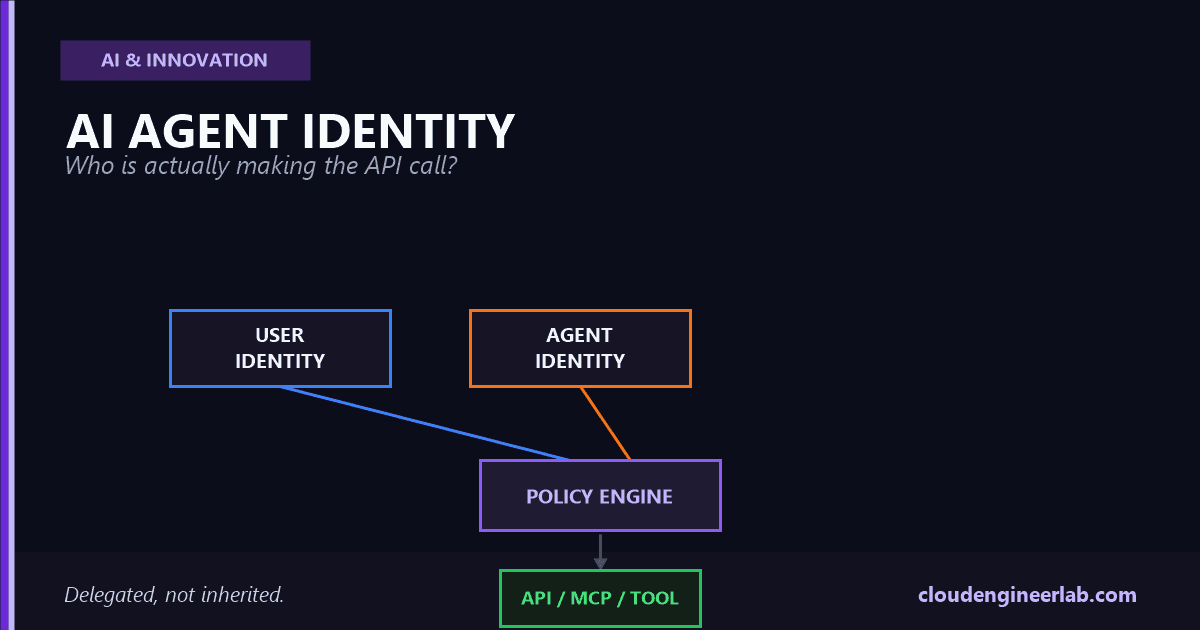
An agent acting for a user isn't the same as the user. A real architectural look at agent identity, delegation, OAuth, least privilege, and zero trust.

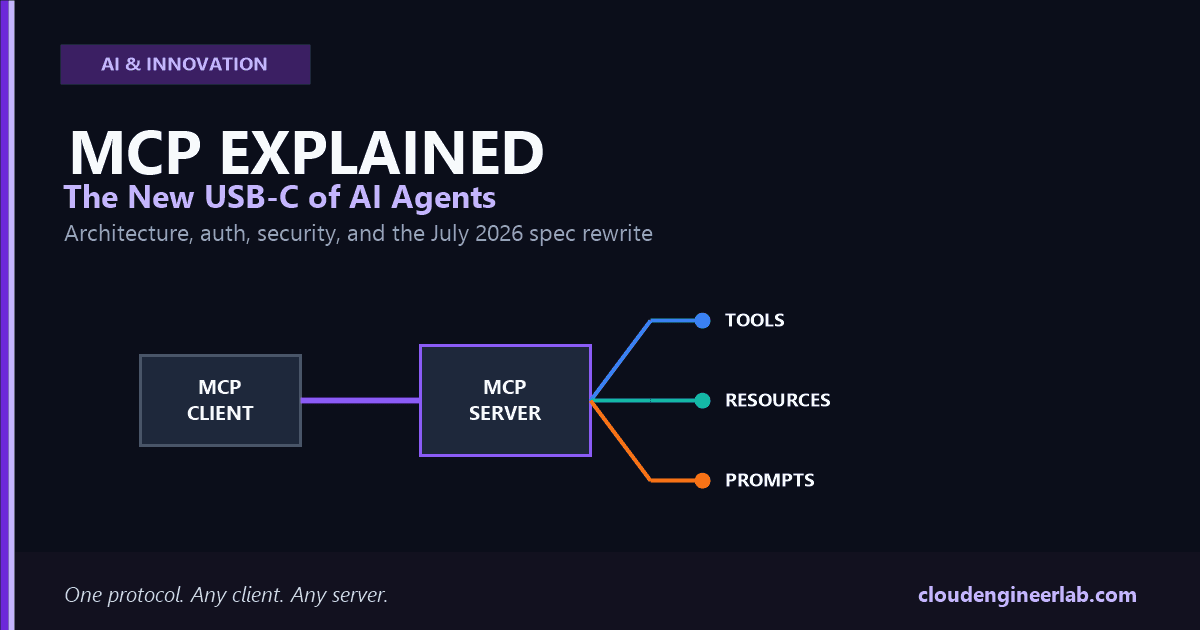
A deep architectural look at MCP: what problem it solves, how client-server and auth work, and what the July 2026 spec rewrite changed.

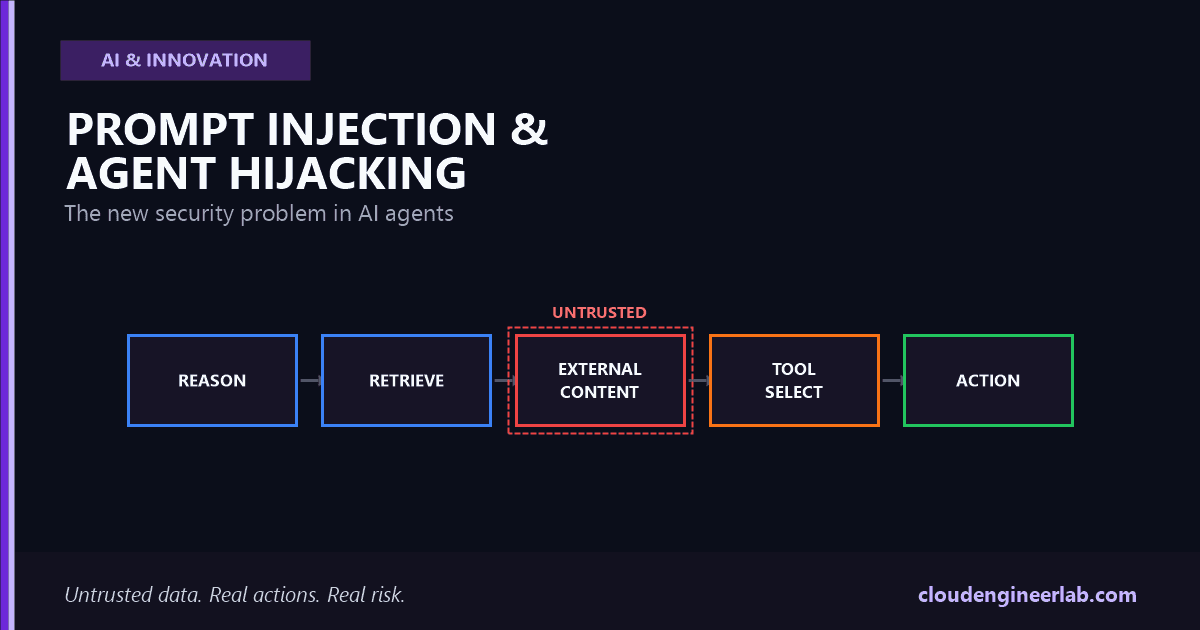
A zero-click email exploit. A poisoned GitHub PR title. Why giving an LLM tools and untrusted data is a systems security problem, not a content one.
Anthropic is moving faster than any AI lab in history. Claude 4 models, Claude Code, Model Context Protocol, Extended Thinking, and Computer Use are reshaping how enterprises build AI automation. Here is everything that matters and how to use it.