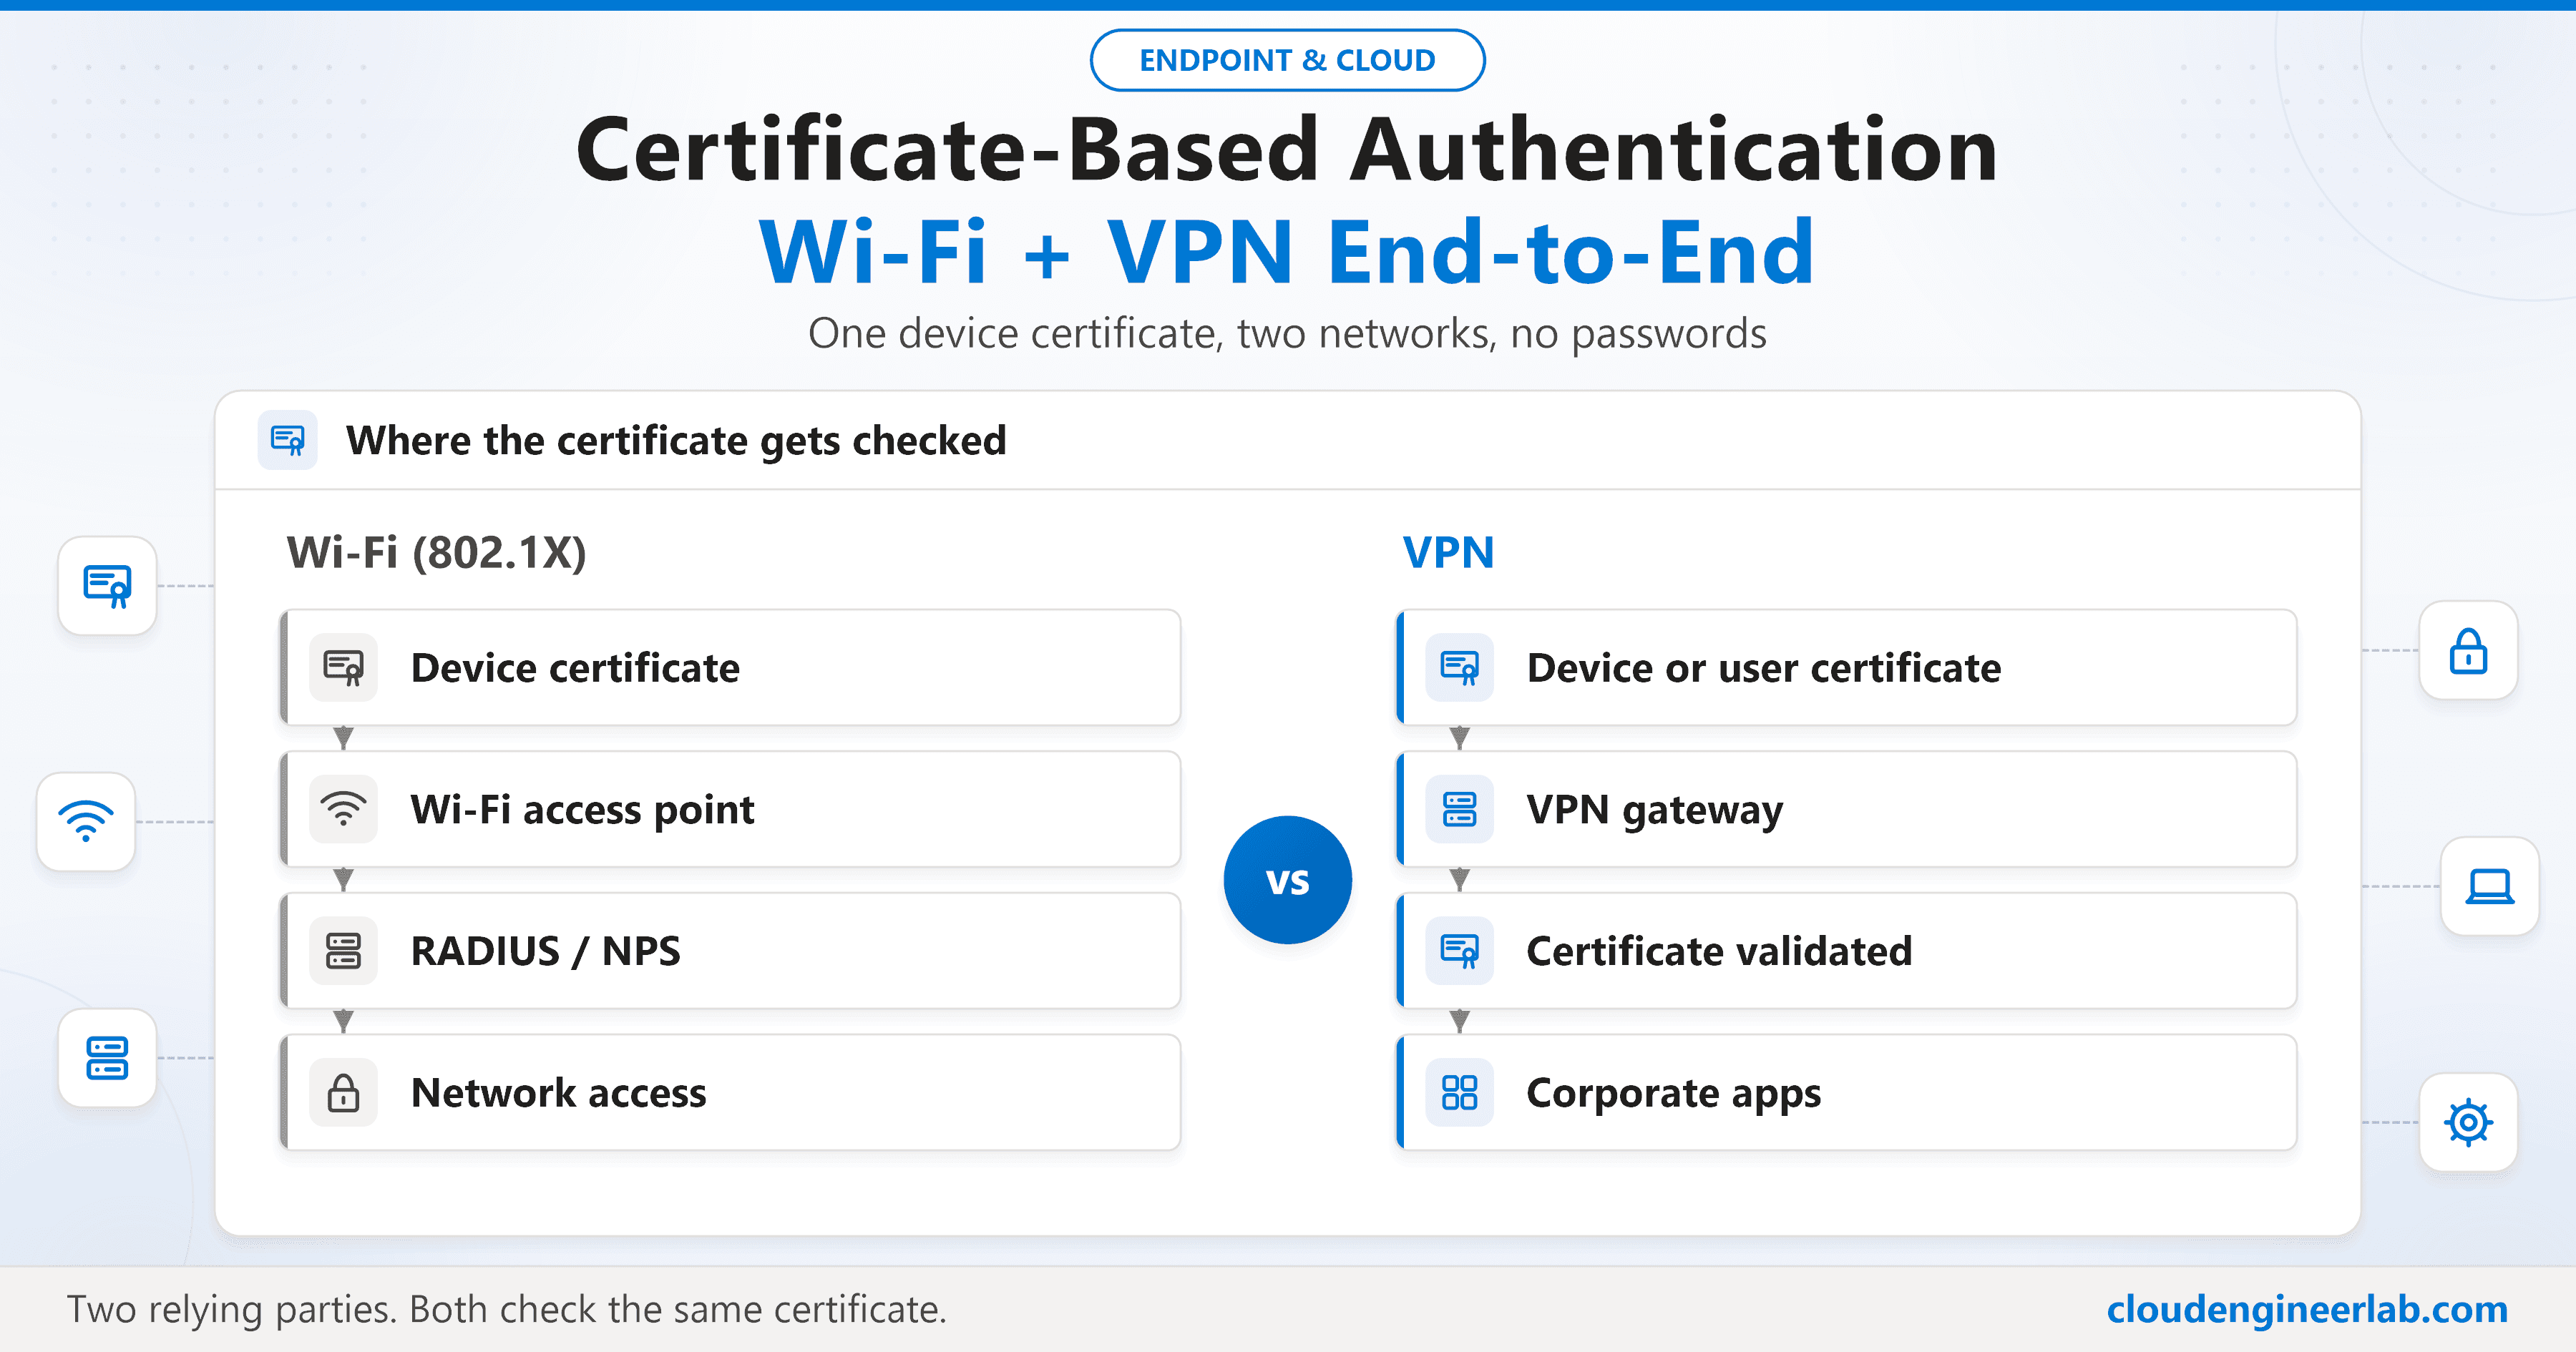
Certificate-Based Authentication with Intune: Wi-Fi + VPN End-to-End
What happens after the certificate lands: device vs user certificates, 802.1X, RADIUS and NPS, VPN authentication, EKUs, trust chains and troubleshooting.
5 posts

What happens after the certificate lands: device vs user certificates, 802.1X, RADIUS and NPS, VPN authentication, EKUs, trust chains and troubleshooting.

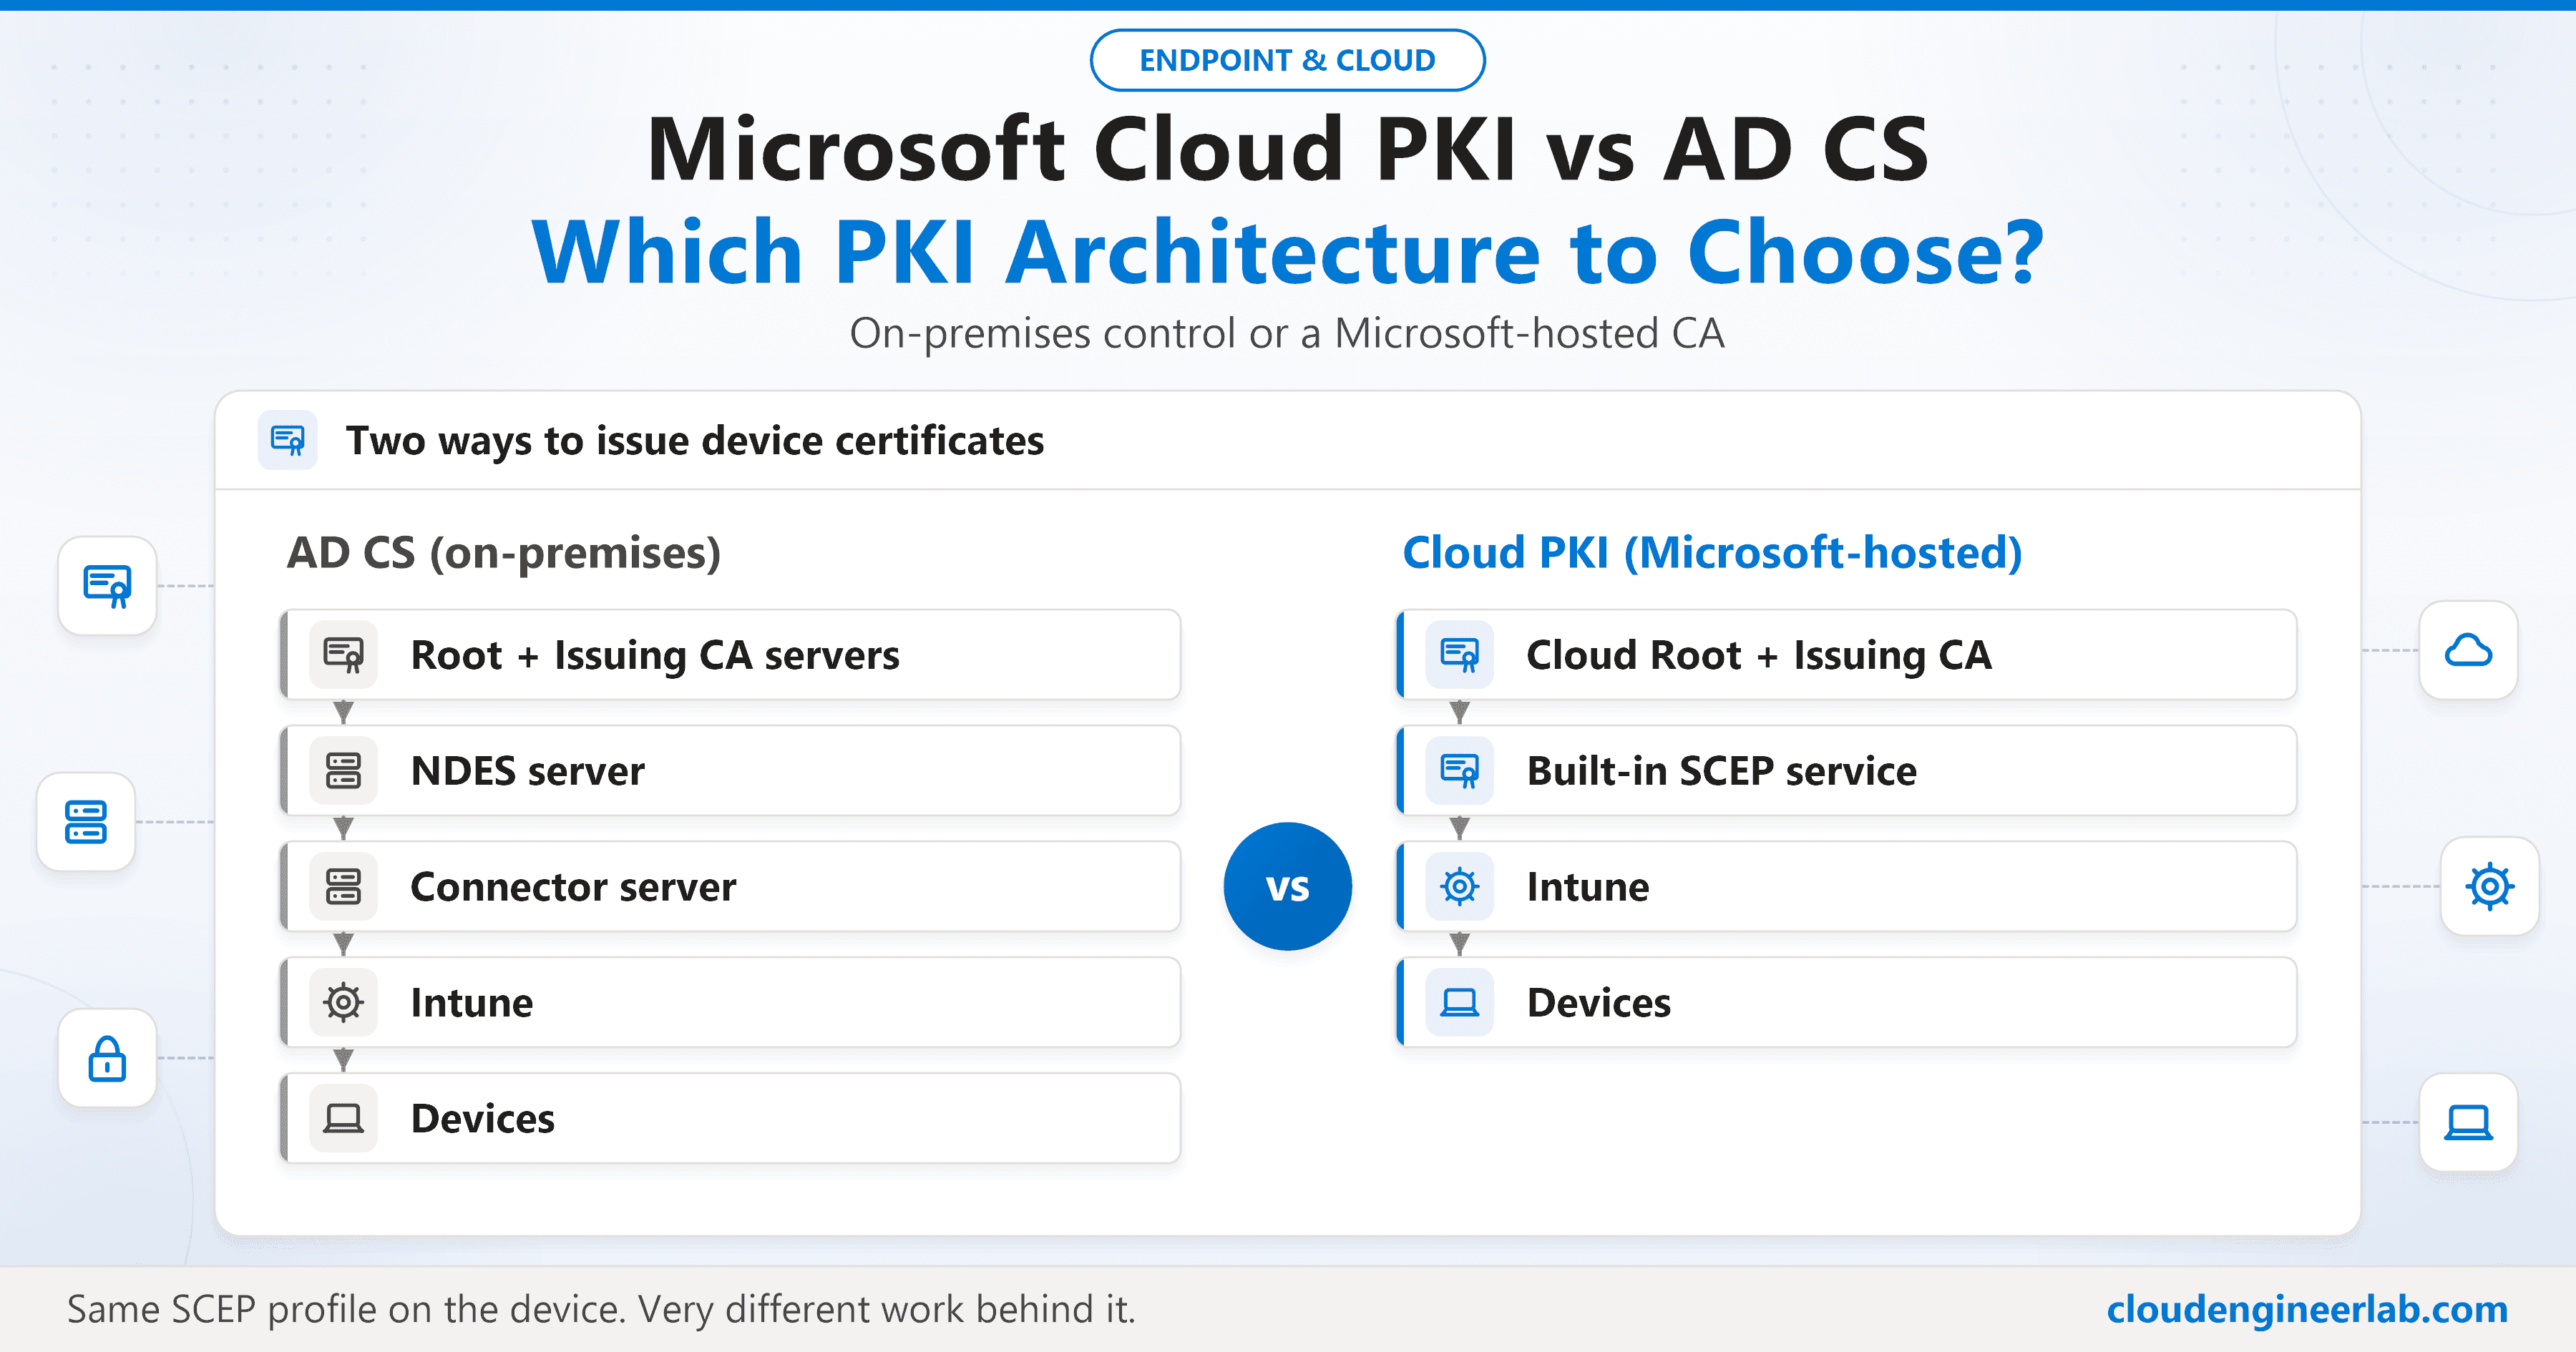
Cloud PKI removes the on-premises CA, NDES and the connector. AD CS can issue to anything. A practical comparison, and a guide to choosing, combining or moving.

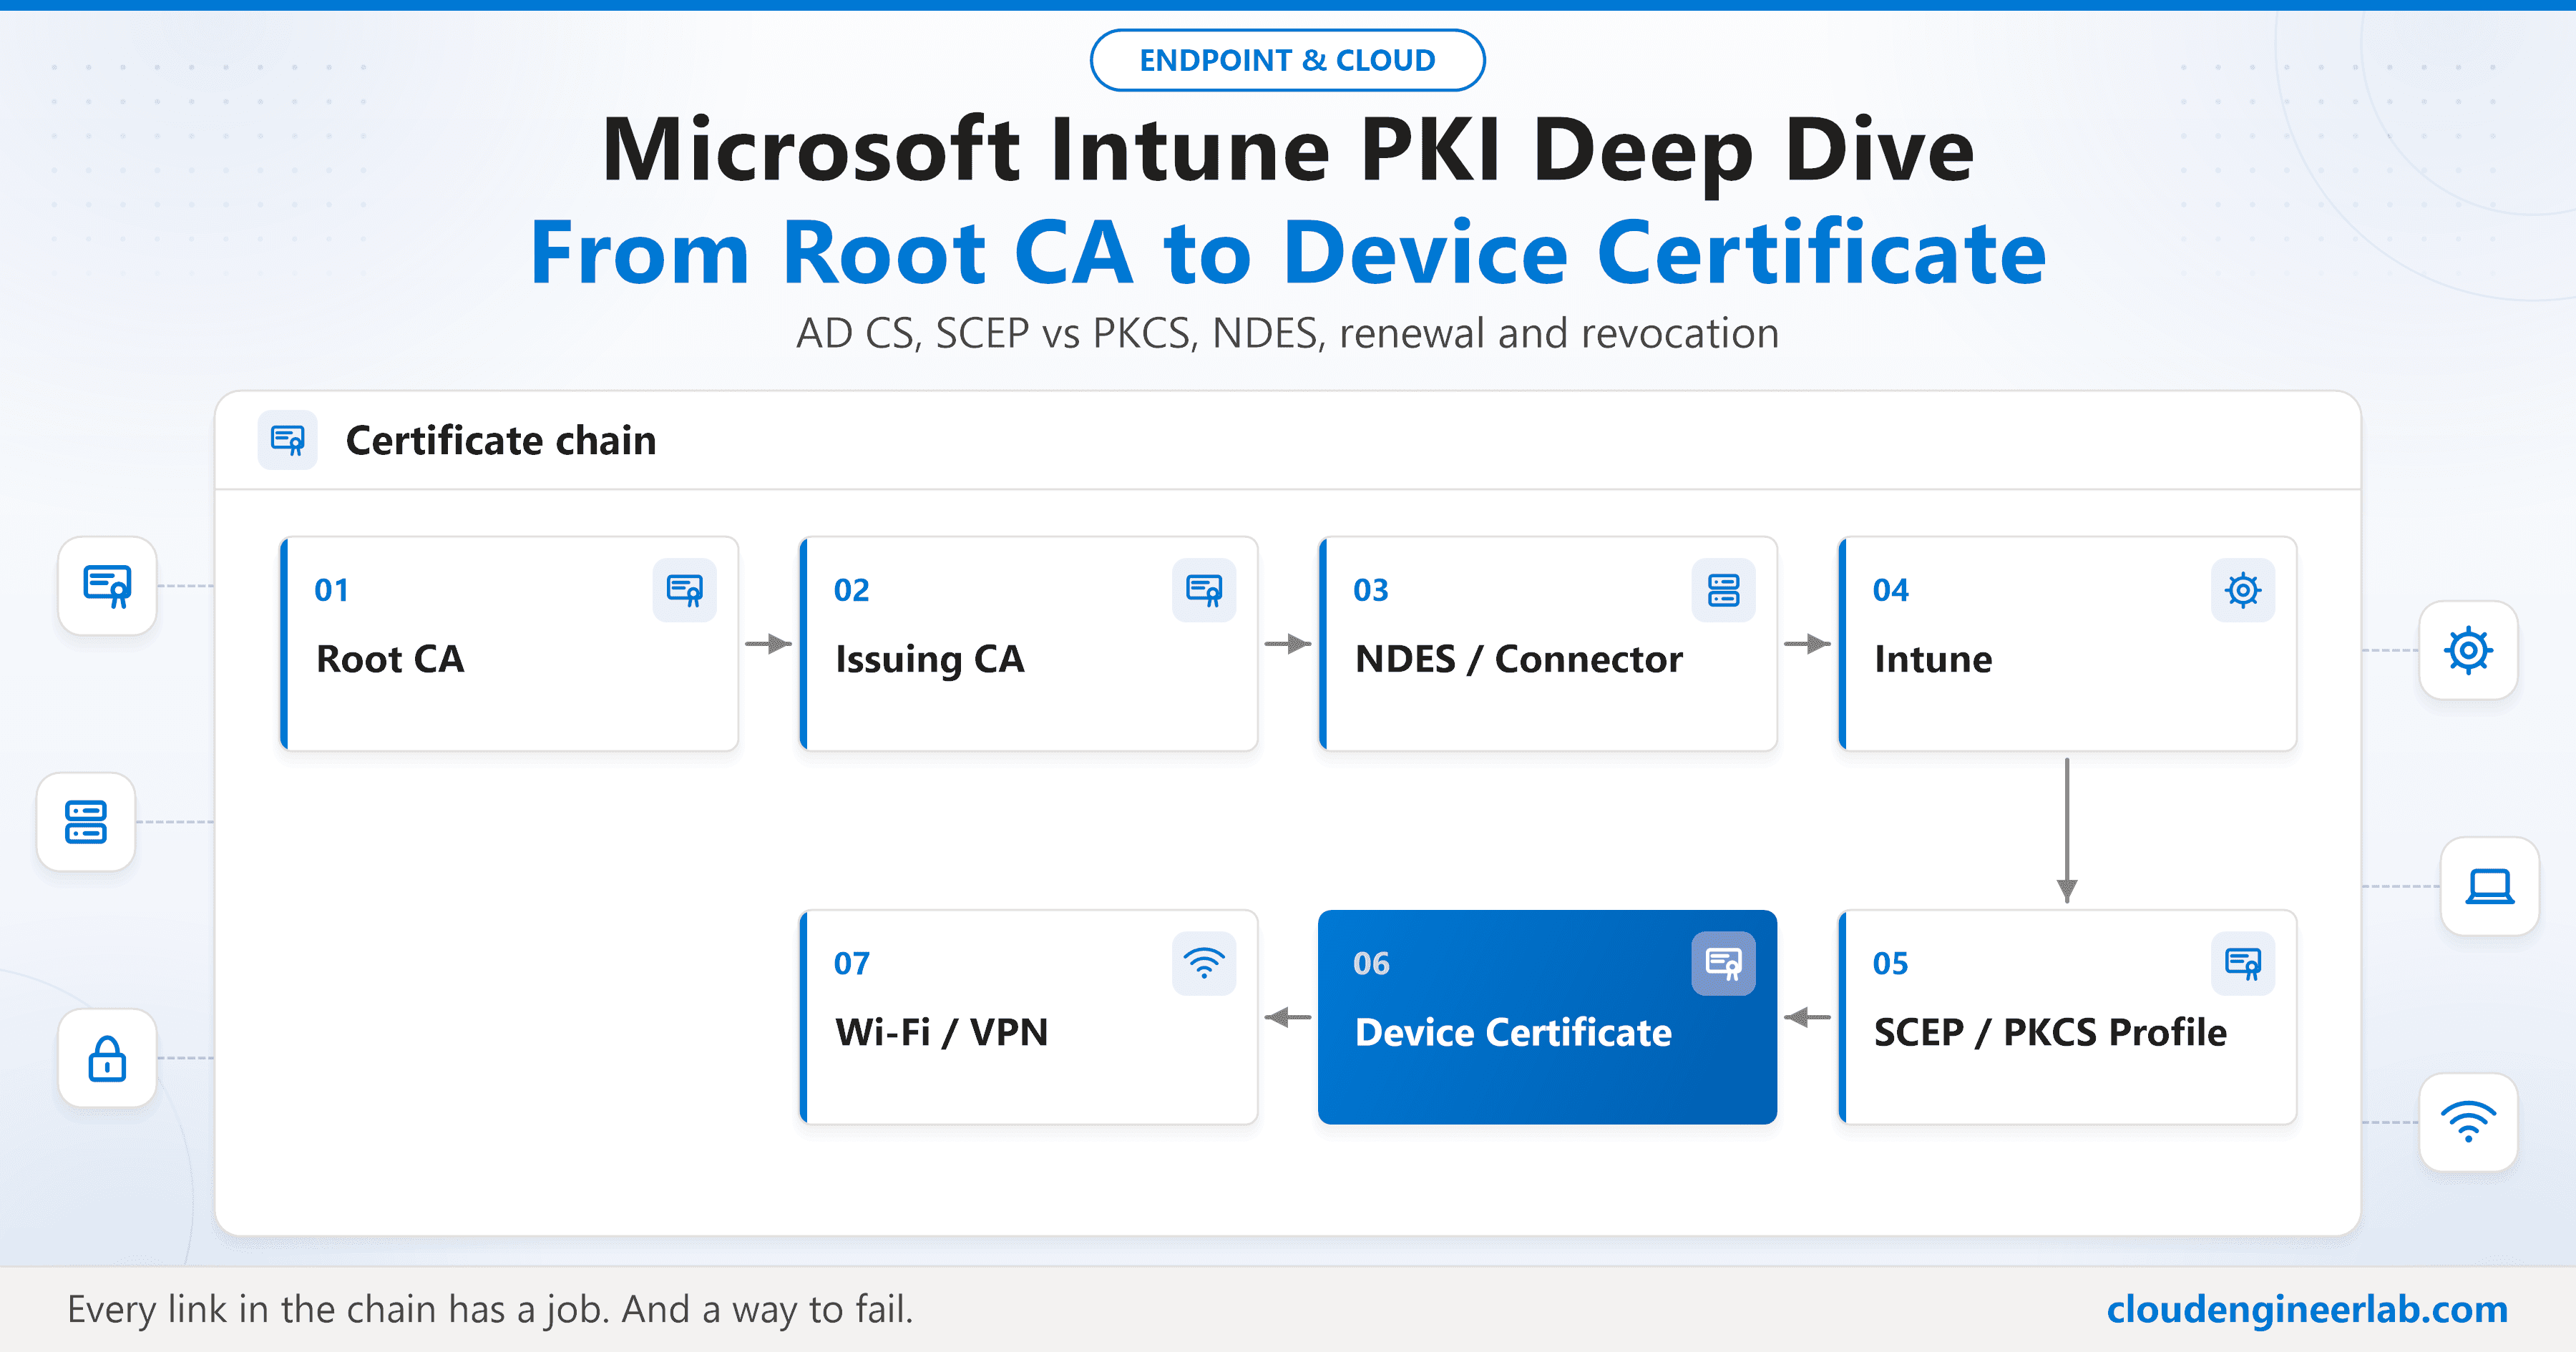
How a certificate gets from your Root CA onto an Intune-managed device: AD CS, templates, SCEP vs PKCS, NDES, the Certificate Connector, renewal and revocation.

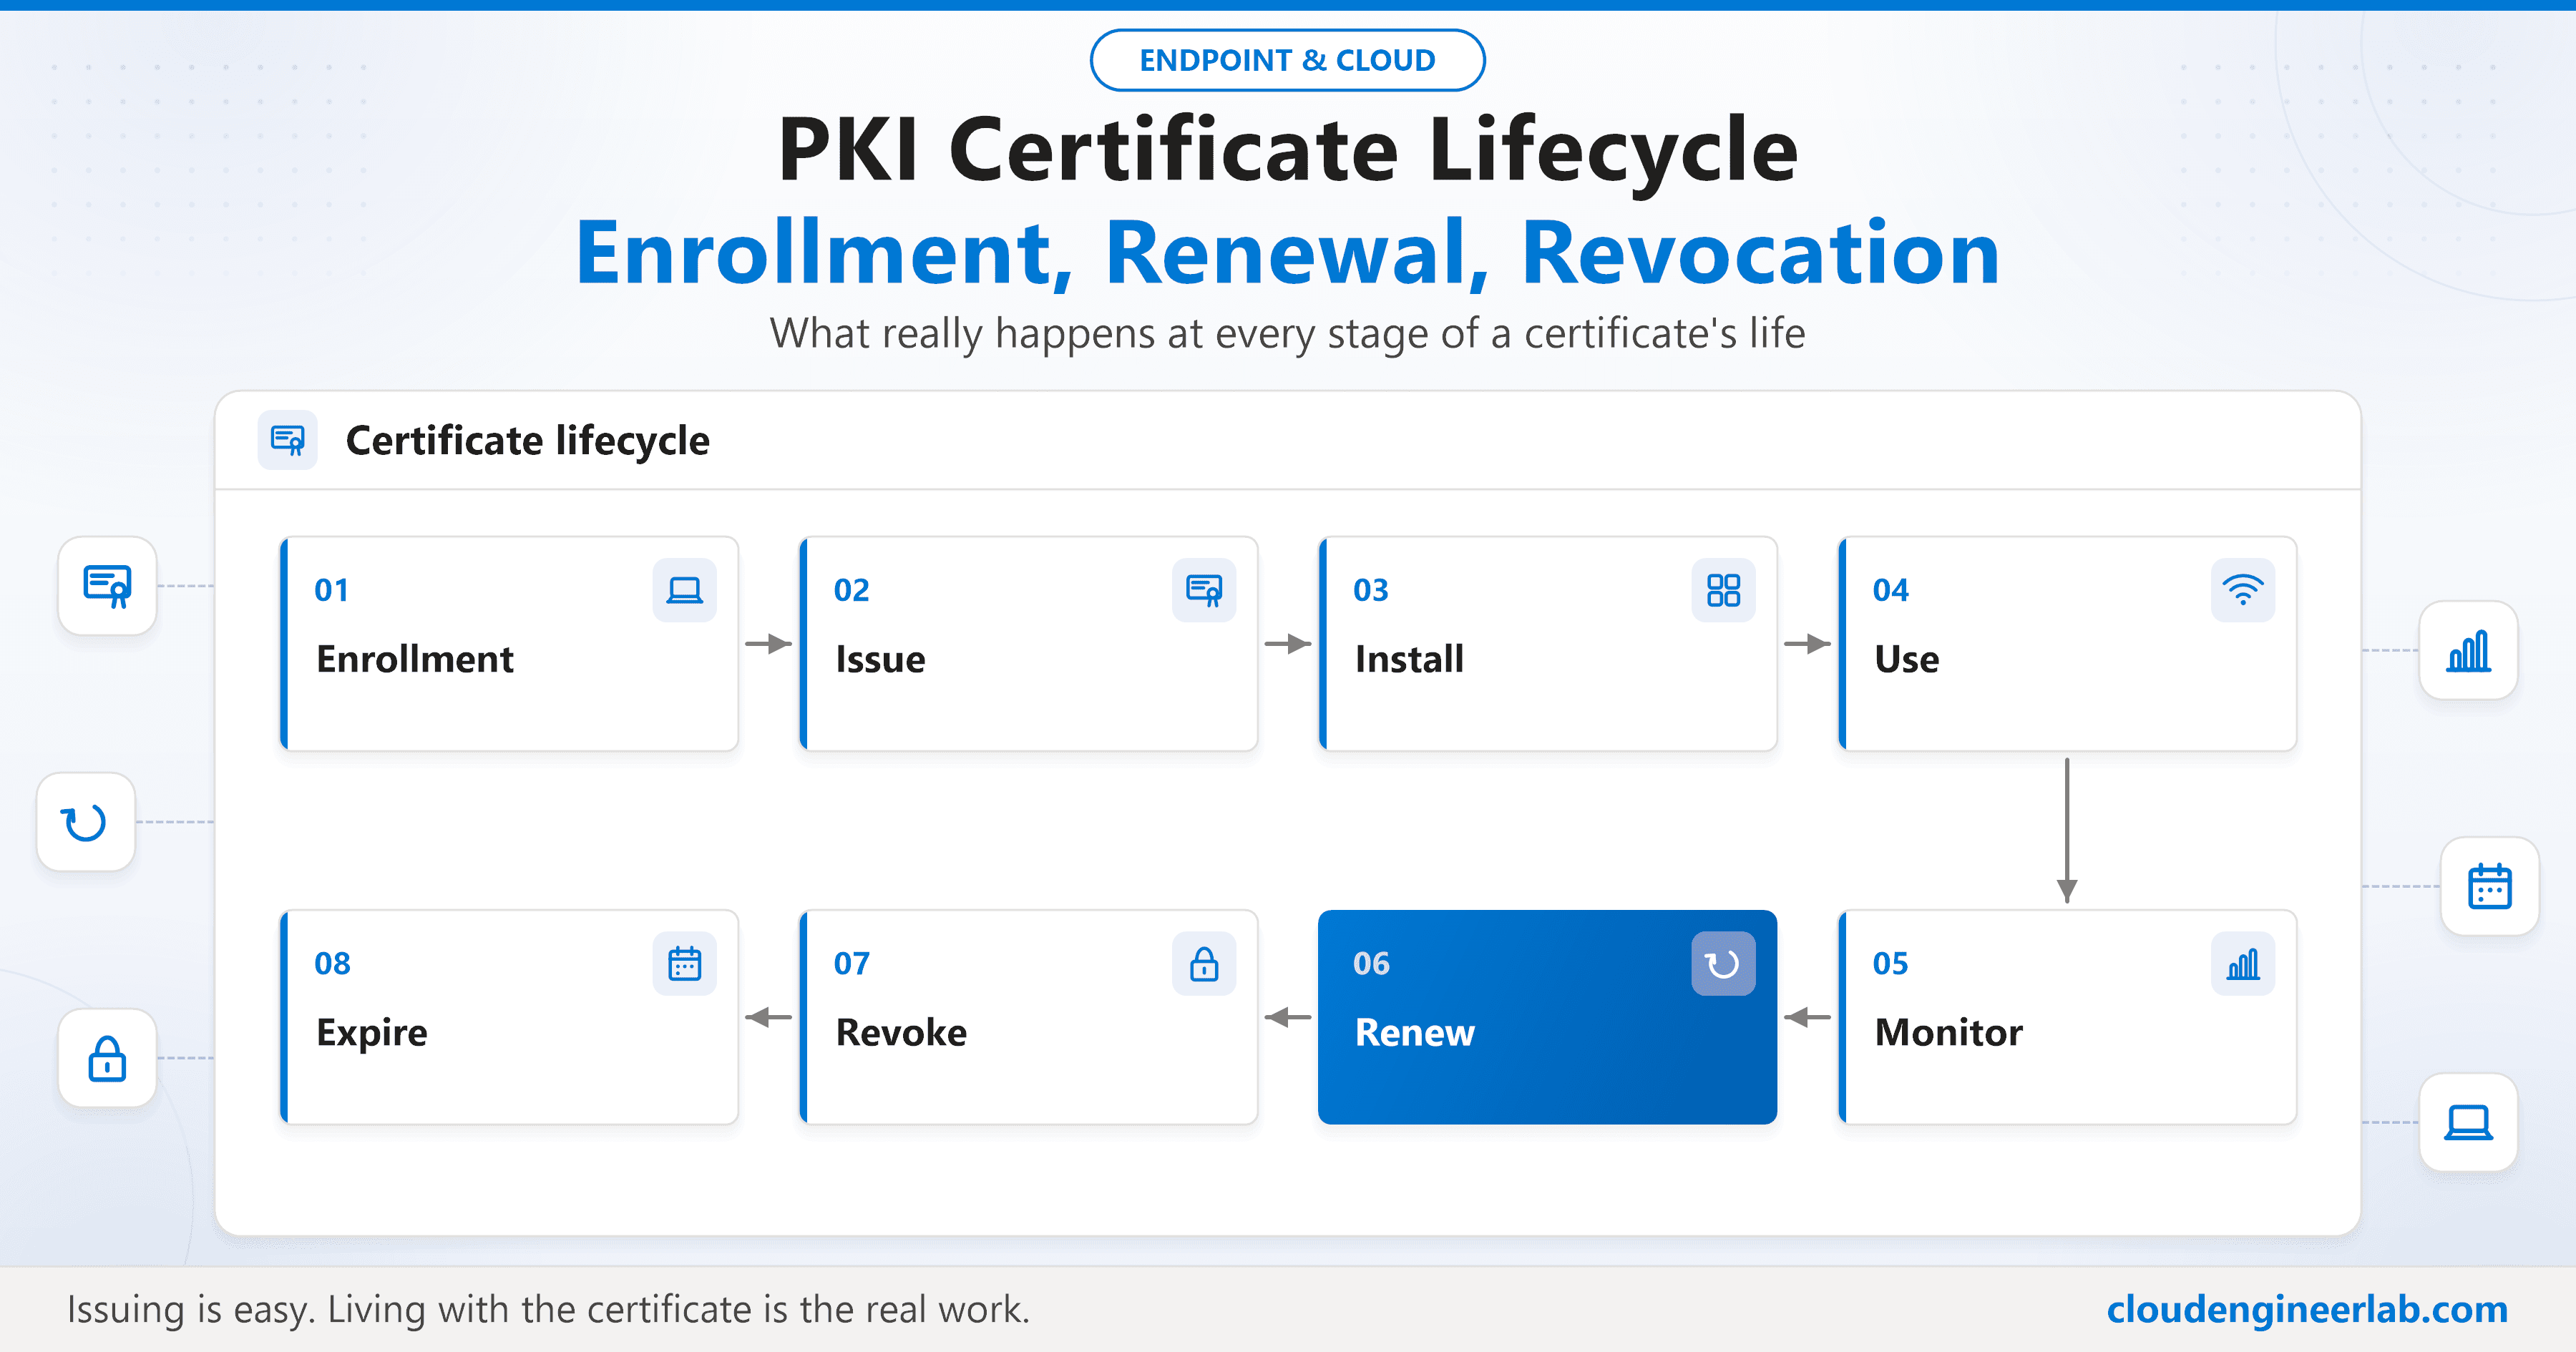
What happens when a certificate expires, a device is deleted or a user leaves: renewal thresholds, failed renewals, revocation timing, CRL vs OCSP.

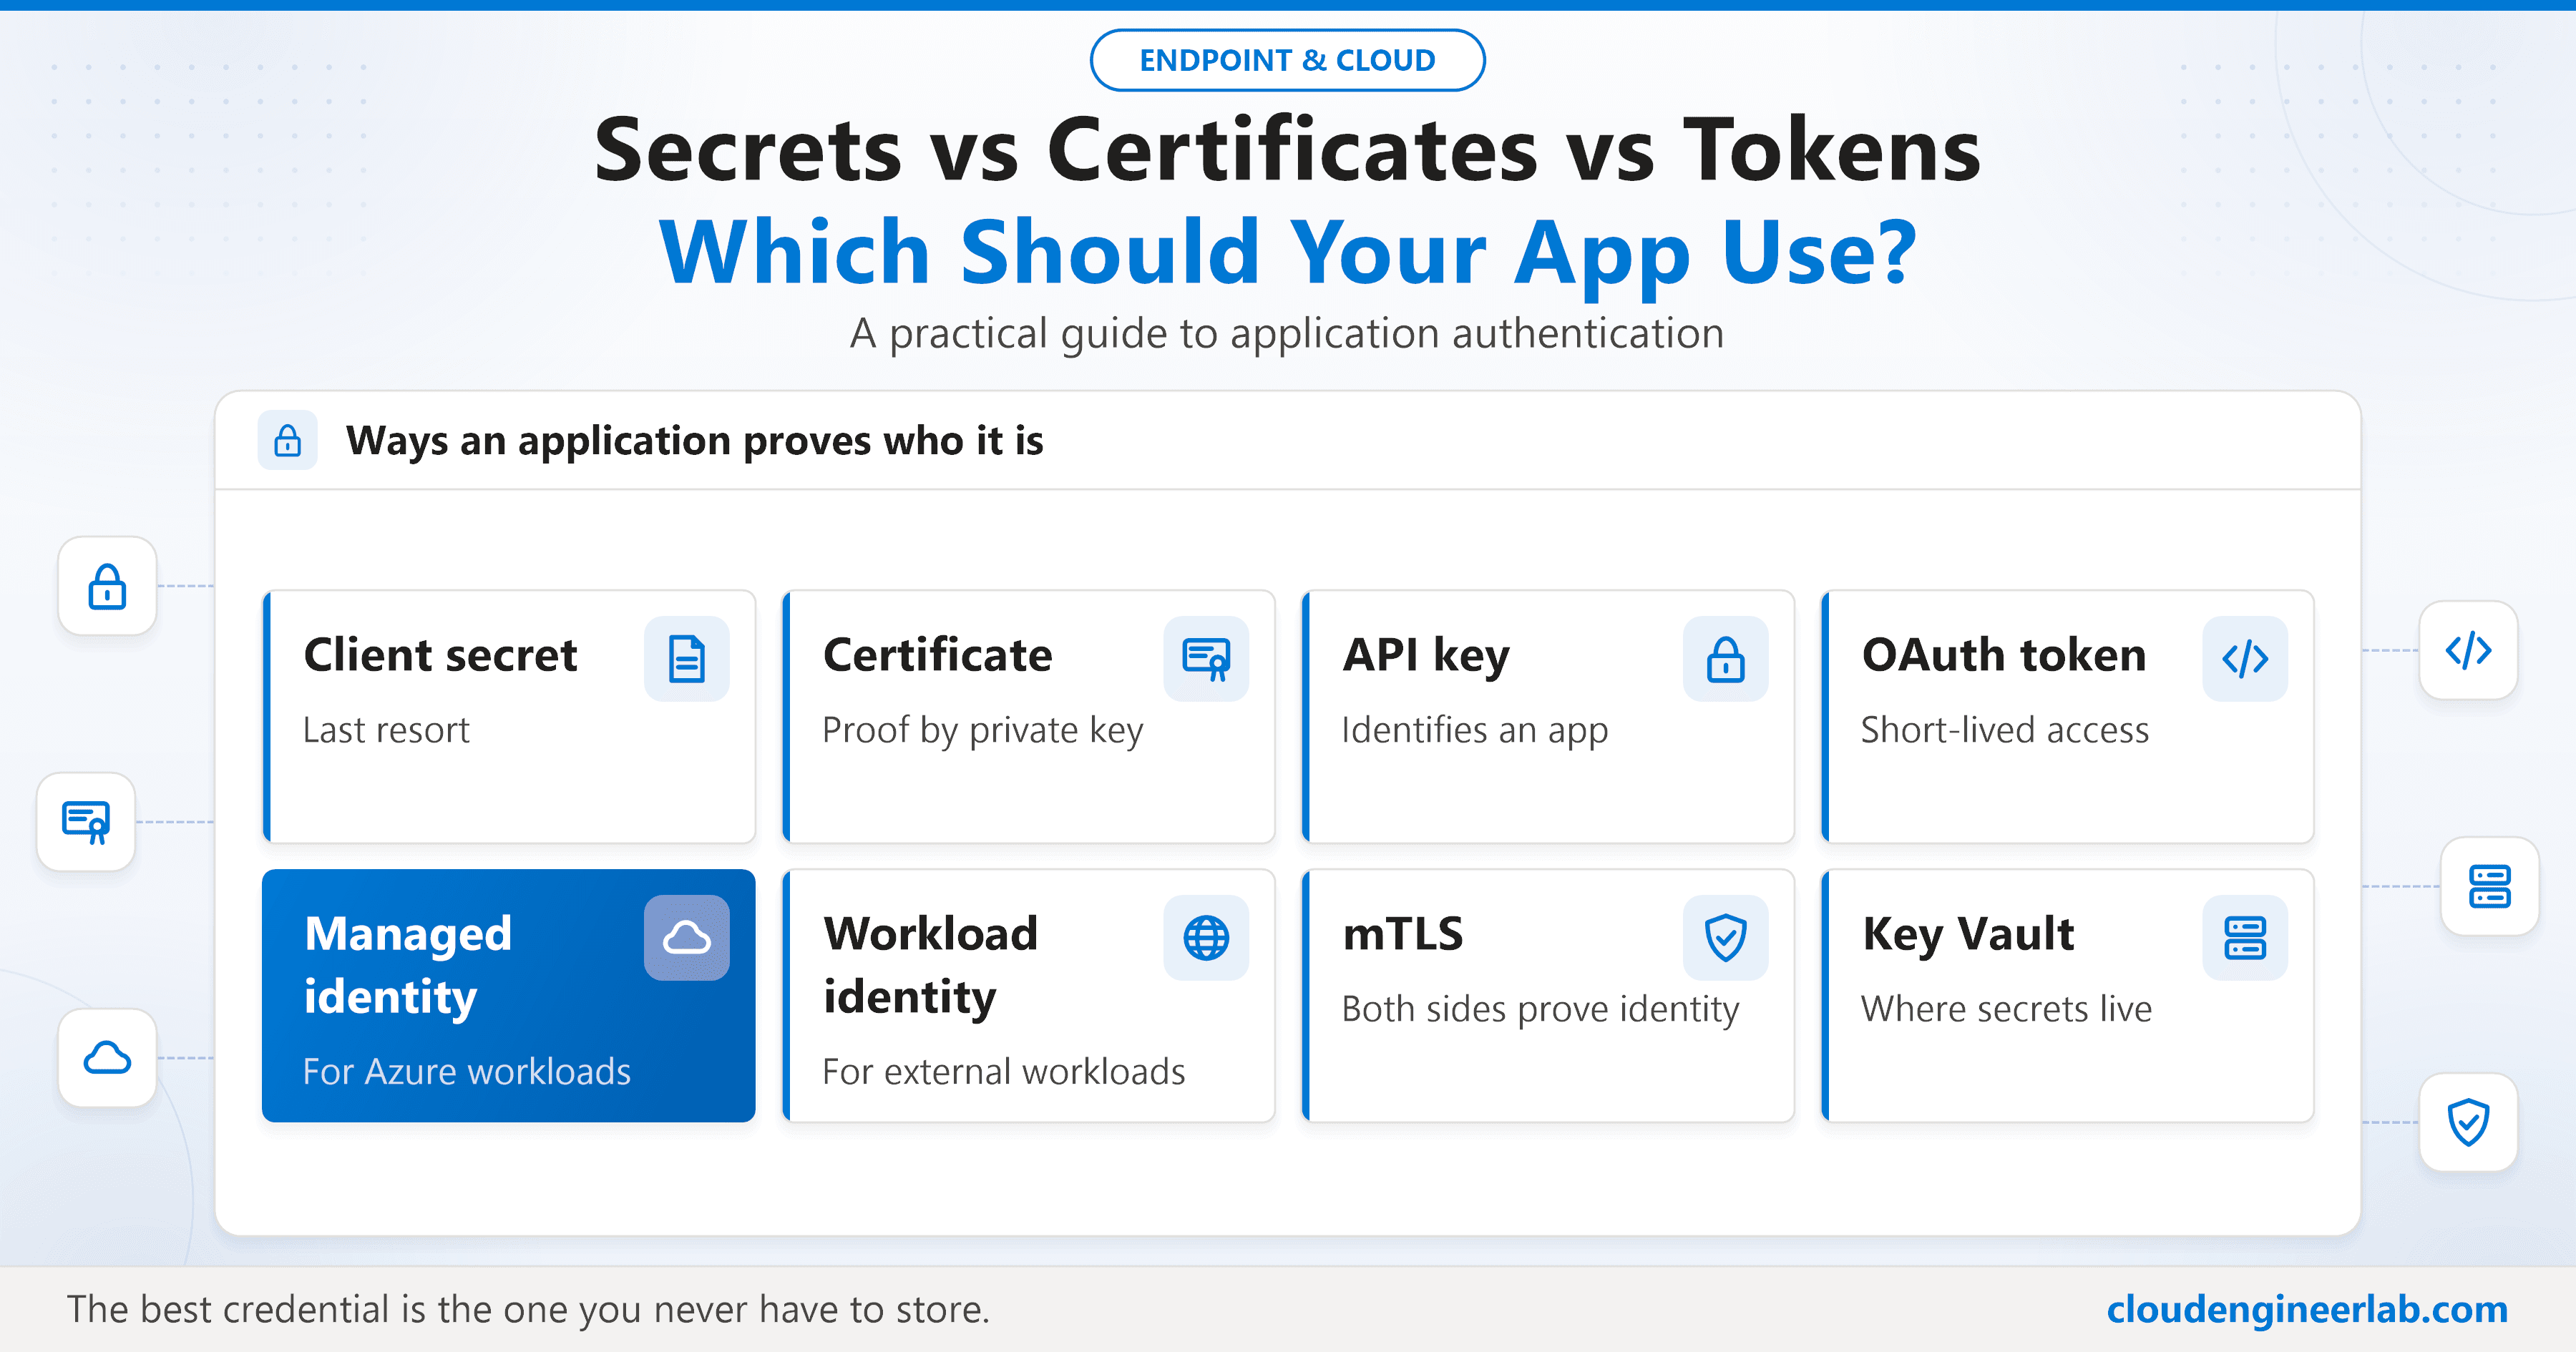
Client secret, certificate, API key, OAuth token, managed identity, workload identity or mTLS? A practical guide to how applications should prove who they are.