The Complete Intune Enterprise Architecture: Five Diagrams, One Flow
From a device coming out of the box to an application landing on it, in the actual sequence a real enterprise deployment runs, not five disconnected slides.
9 posts

From a device coming out of the box to an application landing on it, in the actual sequence a real enterprise deployment runs, not five disconnected slides.

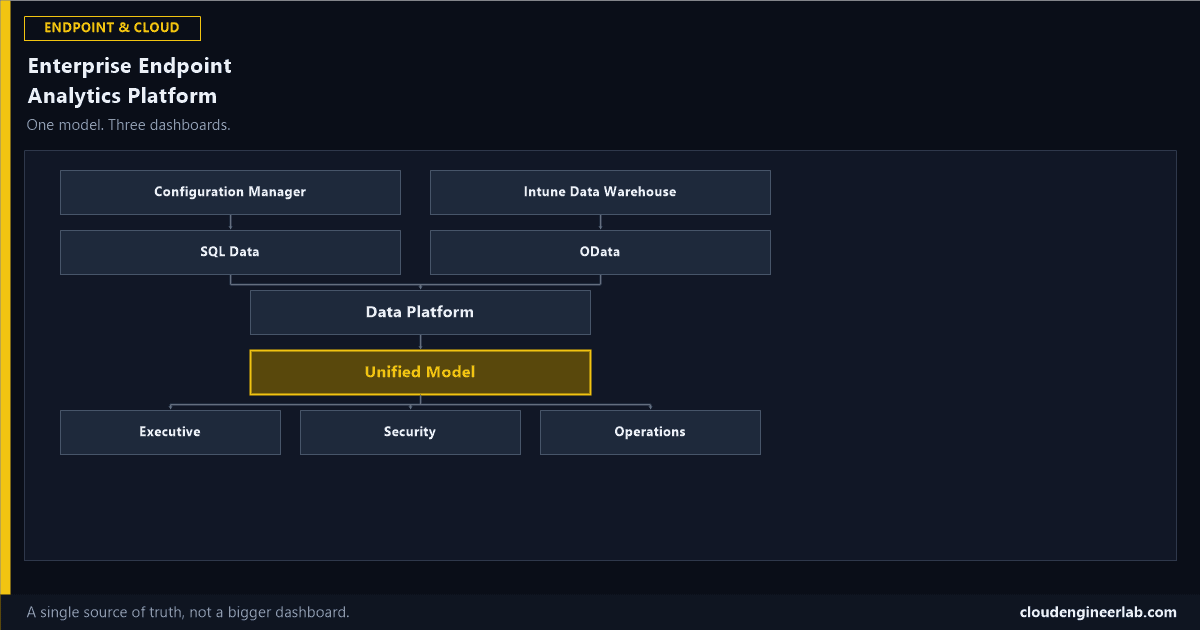
Not another dashboard. One governed model, one refresh strategy, one set of numbers everyone actually trusts, with three different reports built on top of it.

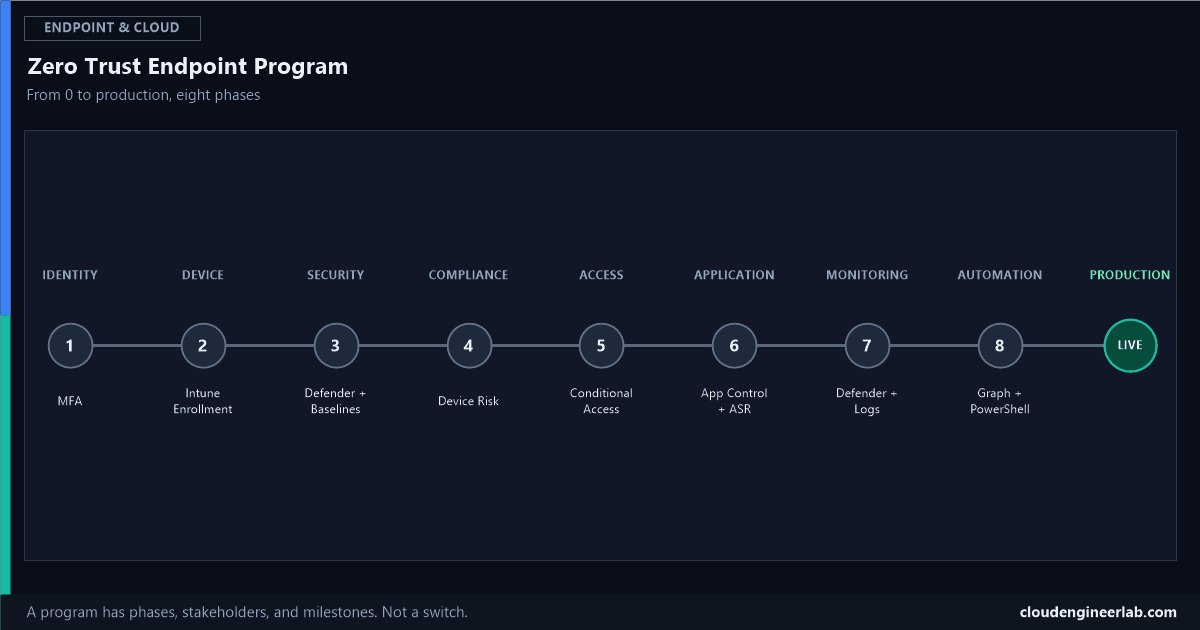
Deploying every control at once produces chaos, not Zero Trust. Eight phases, in the order a real enterprise program actually runs them, with the pitfall at each one.

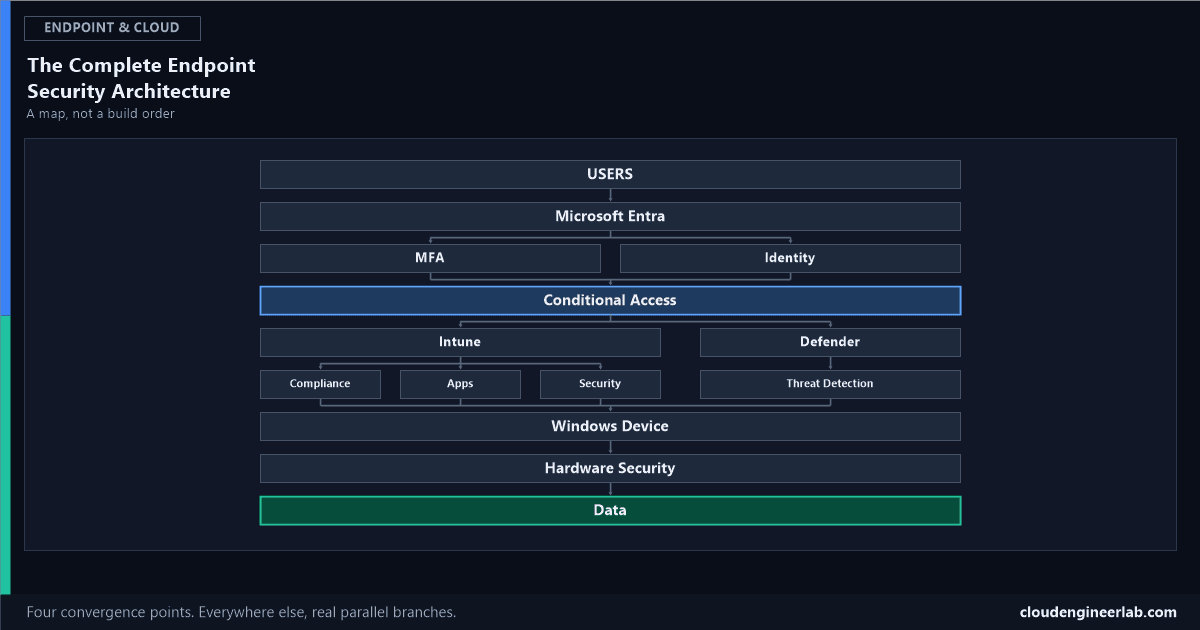
Every product covered on this site, placed on one map, showing exactly what branches in parallel and what has to converge before the next layer can trust it.

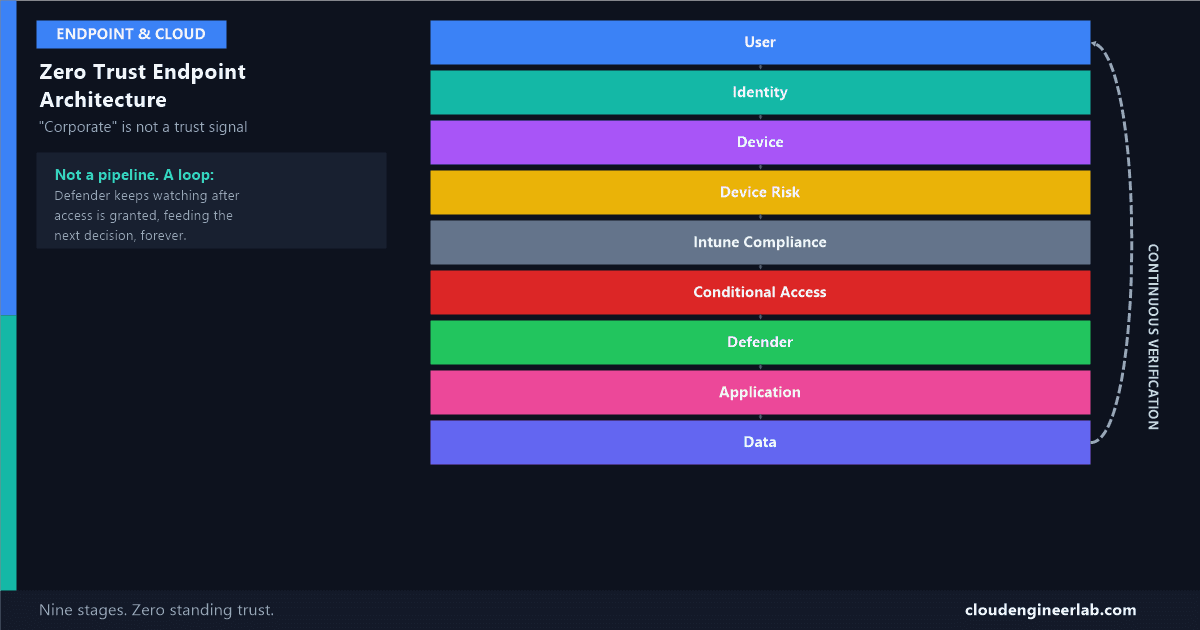
A domain-joined, company-issued laptop is not automatically trustworthy. Nine layers, one continuous loop, and why 'corporate' was never the actual trust signal.

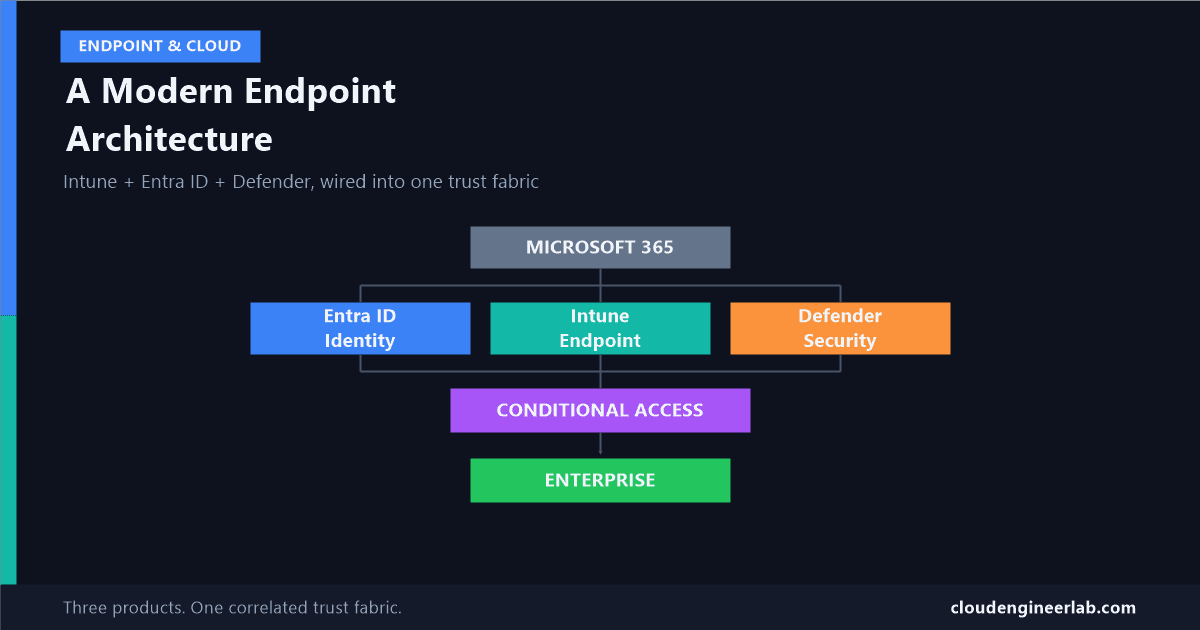
These three products aren't separate tools bolted together, they're one correlated trust fabric. Most tenants deploy all three and never actually wire them into it.

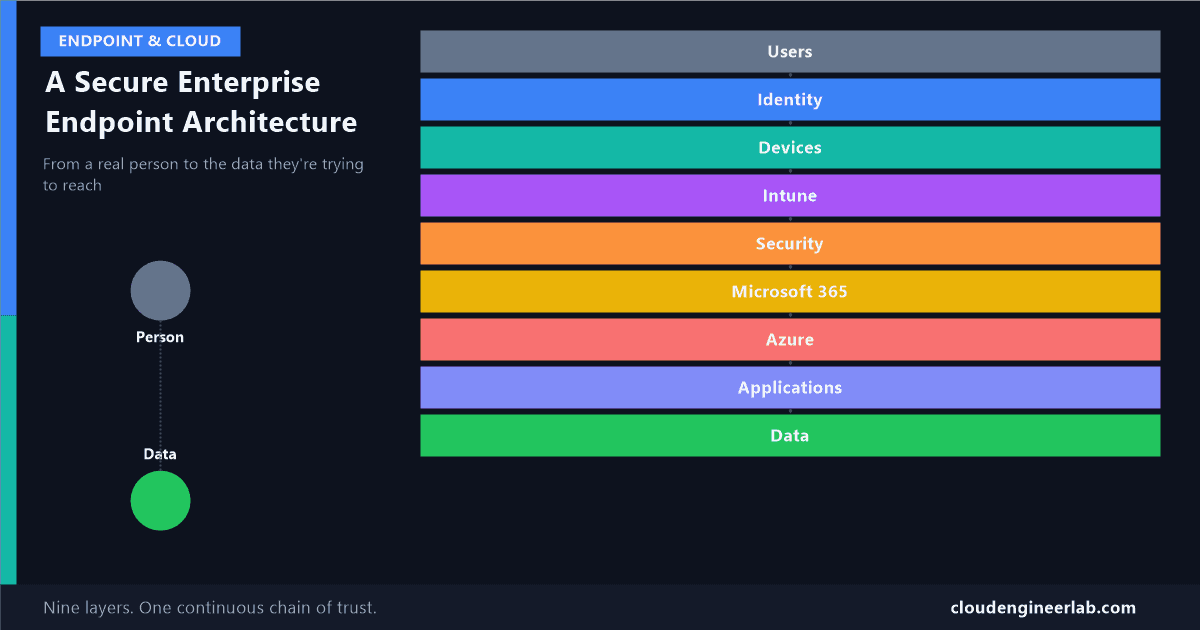
Listing Azure services answers the wrong question. The real one is how trust actually flows from a real person down to the data they're trying to reach.

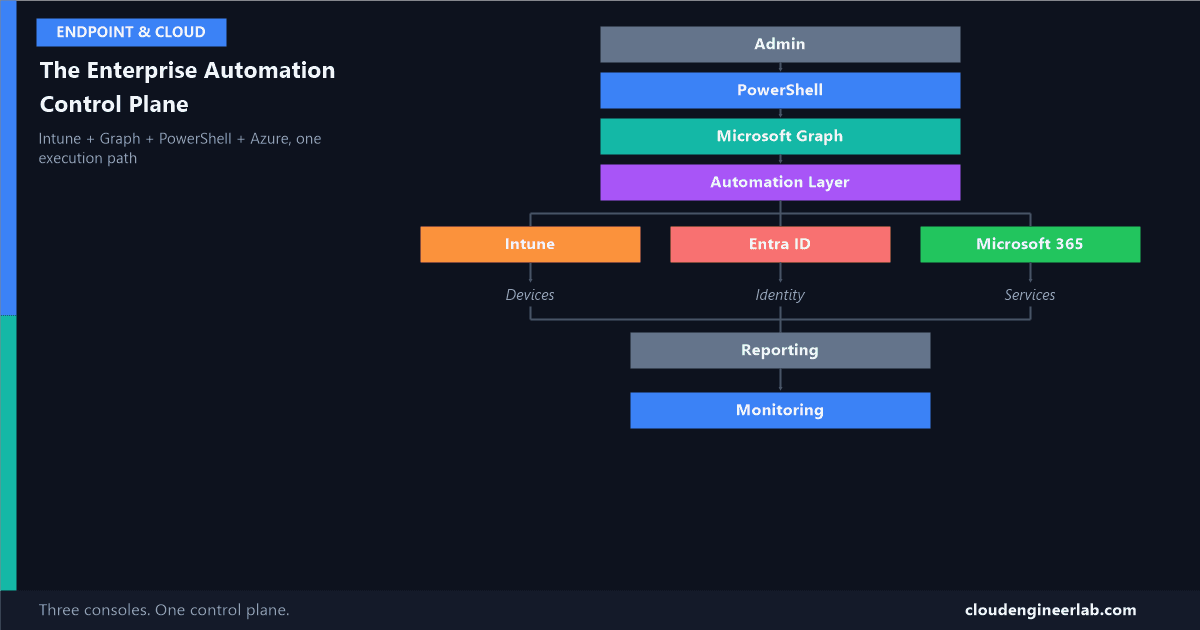
Most tenants run three separate admin experiences, Intune, Entra ID, M365, with three mental models and three audit trails. Here's what replaces all three with one.

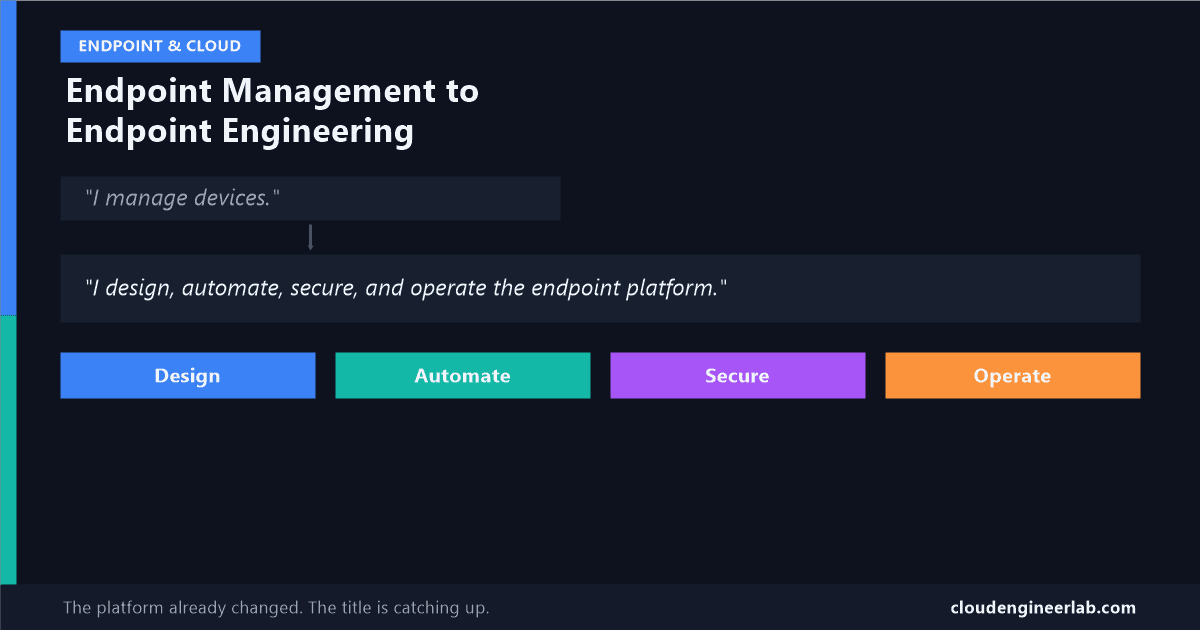
The routine parts of endpoint admin are being automated away, by Microsoft itself. What's left is a genuinely different job, and most job titles haven't caught up yet.